Cyber Essentials certification has no single completion time: your schedule depends on preparation, fixes and the certification body's assessment process. In 2026, plan the whole route from checking your systems to receiving the certificate, not just the time spent answering the questionnaire. Cyber Essentials Plus also requires a technical assessment, so its schedule includes arranging and completing those checks.
How long does Cyber Essentials certification take?
Your completion date depends on when your systems are ready and when your certification body finishes its assessment. Completing the questionnaire is not the same as completing certification. You must accurately describe the systems in scope and meet the scheme's requirements.
Separate the work into preparation, submission and assessment. That gives you a useful schedule instead of an unsupported promise about a fixed number of days.
| Stage | What you need to complete | What determines the timing |
|---|---|---|
| Preparation | Confirm scope, check systems and gather accurate answers | Access to information and the condition of your systems |
| Fixes | Correct gaps against the technical requirements | The changes needed and who can implement them |
| Submission | Review answers and obtain the required declaration | Internal review and access to the authorised signatory |
| Assessment | Receive the certification body's decision and address queries | Assessor turnaround and the completeness of your answers |
| Plus assessment | Complete independent technical checks, if required | Assessment scheduling, readiness and any corrective work |
If you need Plus, read the guide to preparing for a Cyber Essentials Plus audit. Make technical assessment readiness part of your initial plan, rather than a separate project after submission.
Why this matters
A customer deadline usually concerns the issued certificate, not your application date. Work backwards from the evidence that the customer actually requires.
For a 2026 tender or supplier review, check the required certification level and scope before setting your completion date. A certificate that excludes the relevant business activity does not answer the same question as a certificate covering it.
Set separate dates for readiness, submission and certificate receipt. You control the first two through preparation; agree the assessment timetable with your certification body.
Cyber Essentials: prepare the answers before you submit
Cyber Essentials uses an assessor-reviewed self-assessment. You answer questions about the systems in scope and make the required declaration about those answers.
The NCSC's Cyber Essentials scheme covers 5 technical control areas: firewalls, secure configuration, security update management, user access control and malware protection. Use the official requirements that apply to your application, rather than an old questionnaire saved from a previous submission.
The questionnaire asks about actual controls. A policy stating that you install updates does not establish whether your devices and software meet the update requirements.
What to have ready
- An agreed description of the organisation and systems in scope.
- An inventory of relevant devices, operating systems and software.
- Clear information about business cloud services and account access.
- Verified answers about security settings and update management.
- An owner for each outstanding technical change.
- An authorised person who can approve the declaration.
This route is best for businesses whose customer or contract requires Cyber Essentials without Plus. Its advantage is the assessor-reviewed questionnaire format; its limitation is that it does not provide the independent technical verification included in Plus.
Do not select the level solely to shorten the project. Check the buyer's requirement first, then prepare for the level that meets it.
Cyber Essentials Plus: include the technical assessment
Cyber Essentials Plus adds independent technical verification of the controls. Passing the questionnaire alone does not complete Plus certification.
IASME's published scheme guidance requires the Plus assessment to take place within 3 months of achieving Cyber Essentials. That window is a scheme requirement, not a promise that the whole project takes 3 months.
Confirm the applicable window and assessment arrangements with your certification body when planning your 2026 application. Leave room to correct issues identified during the technical assessment.
| Route | Best for | Main advantage | Main limitation |
|---|---|---|---|
| Cyber Essentials | Businesses meeting a Cyber Essentials requirement | Assessor reviews your declared controls | Does not include Plus technical verification |
| Cyber Essentials Plus | Businesses needing independently verified controls or meeting a Plus requirement | Adds hands-on verification of controls | Requires assessment arrangements and technical readiness |
Arrange access to the devices, accounts and people the assessor needs. A booked assessment does not remove the need to prepare those systems.
Treat Cyber Essentials and Plus as connected stages. Align their scope and discuss technical readiness before completing the questionnaire.
Why Cyber Essentials certification time varies
The timetable follows the work required to demonstrate compliance. These factors explain why an assessor's review turnaround is not the same as your end-to-end completion time.
- Scope clarity. Identify the systems and business activities covered before answering questions. Unresolved boundaries prevent a consistent submission.
- Device and software records. You need accurate information about the systems you use. Gather it from verified records, not memory.
- Technical gaps. Unsupported software, unsuitable settings or access-control gaps require action before you declare compliance.
- Responsibility for changes. Establish whether your internal team, outsourced IT provider or another supplier controls each setting.
- Assessment arrangements. Confirm the certification body's review process and, for Plus, the technical assessment arrangements.
- Answer quality. Complete, consistent answers give the assessor a clearer submission to review. Unclear answers require clarification.
Turn each unresolved item into an action with an owner and a completion date. Avoid a single task called certification: it conceals the work that determines your schedule.
How do you build a realistic certification schedule?
Build your 2026 schedule around completed work, not an assumed average. Ask the certification body which turnaround applies to your submission and what that turnaround excludes.
1. Confirm the requirement
Ask your customer whether it needs Cyber Essentials or Cyber Essentials Plus. Confirm which legal entity and business activities the certificate must cover.
Record the date the customer needs the issued certificate. Do not substitute an internal target for that contractual requirement.
2. Agree scope
Identify the devices, services and users covered by your application. Include the working arrangements relevant to that scope, such as remote access and business use of personal devices.
Document exclusions clearly and check that they are permitted. A narrower scope still needs to satisfy the customer's requirement.
3. Check controls
Review your systems against the applicable Cyber Essentials requirements. Check real settings, supported software and access arrangements.
Separate verified answers from items that still need investigation. An unanswered technical question is unfinished preparation, not a detail to resolve after signing.
4. Fix gaps
Assign each required change to someone with authority to make it. Agree how you will verify completion.
Check the result after the change. A closed support ticket is not a substitute for confirming that the system now meets the requirement.
5. Submit and assess
Review the questionnaire for accuracy and consistency. Obtain the required declaration, submit it and keep someone responsible for responding to assessment queries.
For Plus, coordinate technical access and assessment arrangements with your certification body. Keep the scope consistent across the connected assessments.
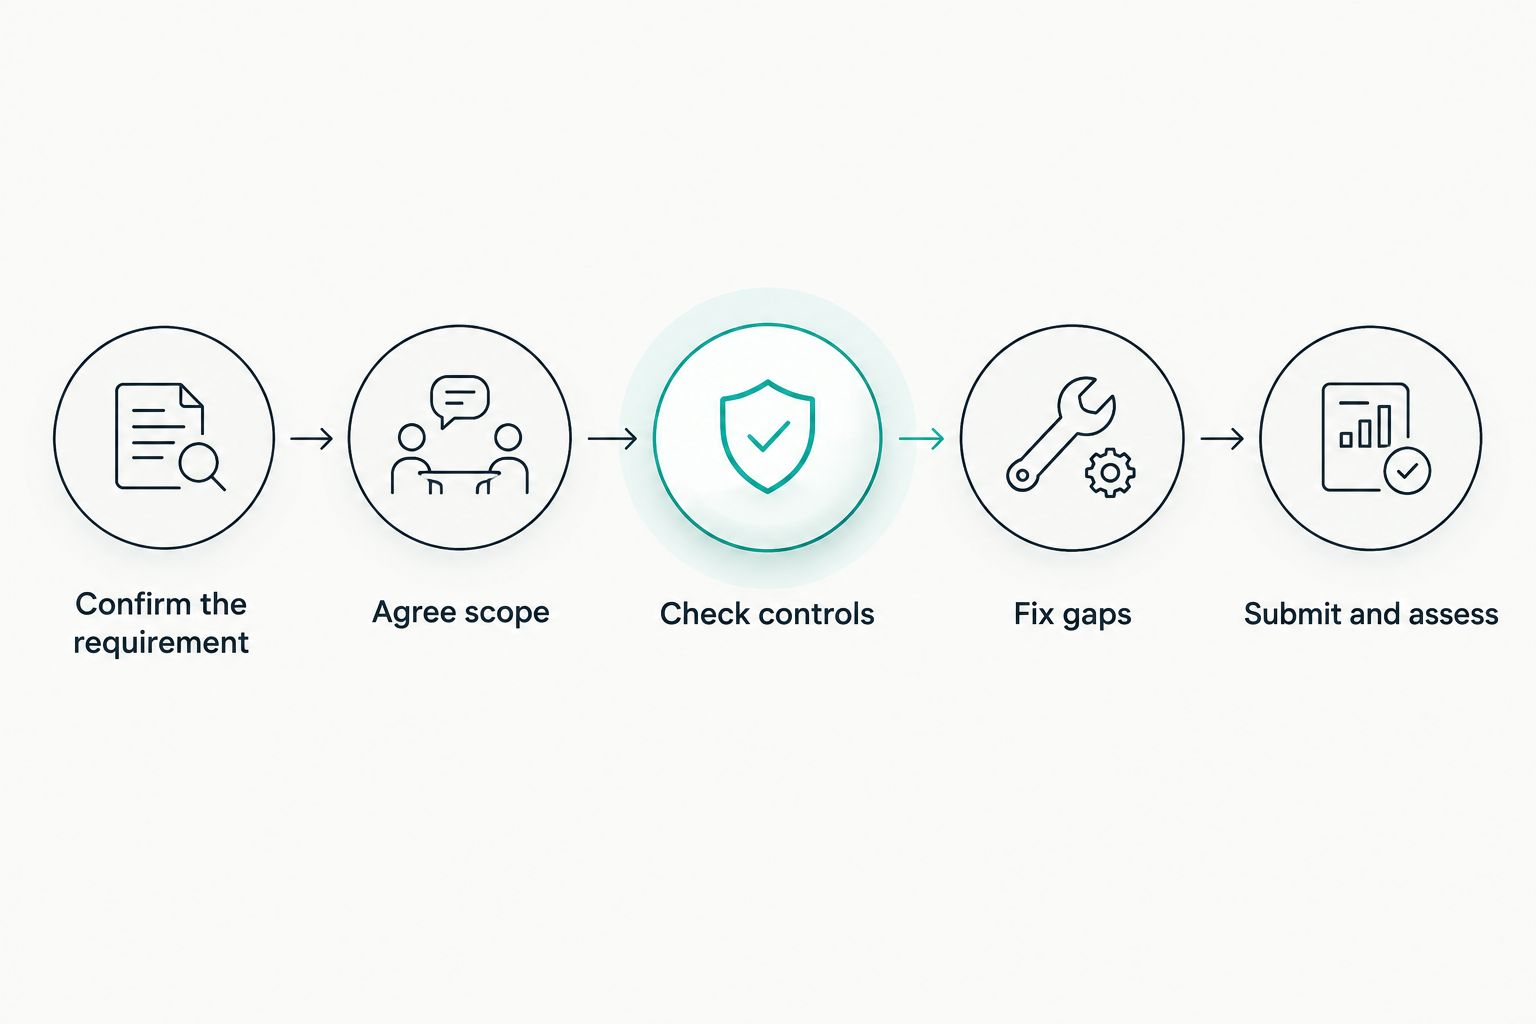
Resolve scope and technical gaps before you submit your answers.
Use these stages as a progress check. If a stage has unresolved work, show it explicitly rather than marking the whole application as nearly complete.
What should you ask your certification body about timing?
Ask questions that distinguish your preparation from the assessor's work. A turnaround estimate is useful only when you understand when its clock starts.
- Does the quoted turnaround begin at purchase, submission or receipt of a complete application?
- Does it use working days or calendar days?
- What happens when an assessor requests clarification?
- Who receives assessment queries, and how should you respond?
- For Plus, what must be ready before the technical assessment?
- What happens if technical checks identify something you must fix?
Keep the answers with your project plan. Your team then works against the same assumptions instead of using different interpretations of the promised turnaround.
Do not promise a customer a certificate date based only on submission. Confirm the remaining assessment steps first.
Can you get Cyber Essentials certified immediately?
Cyber Essentials certification requires assessor approval, so completing your answers does not produce an immediate certificate. You still need the certification body's decision.
If you have already checked the controls and resolved the gaps, your remaining work is submission and assessment. Ask the certification body about that specific position rather than requesting a generic end-to-end estimate.
Does Cyber Essentials Plus take longer than Cyber Essentials?
Cyber Essentials Plus includes additional technical assessment work, so your plan must cover more than the questionnaire. Assessment scheduling and any corrective work become part of the route to certification.
The 3 months allowed between achieving Cyber Essentials and completing the Plus assessment is not a recommended waiting period. Coordinate the assessments so that preparation remains relevant and the window does not become a last-minute constraint.
How long does Cyber Essentials certification last?
Cyber Essentials certification is valid for 12 months. Renewal requires a fresh assessment; you do not simply keep using an expired certificate.
Plan your next renewal while completing your 2026 application. Keep current records of devices, software and access so the next submission starts from verified information.
Where compliance automation fits
OneClickComply suits growing businesses managing Cyber Essentials compliance end-to-end. Its software automates cyber security compliance certifications, including Cyber Essentials, ISO 27001 and SOC 2.
Use OneClickComply when you want to manage compliance through software rather than treat each certification as an isolated administrative task. The practical fit is a growing business seeking end-to-end compliance management.
Automation does not replace the certification body's decision. You still need compliant systems, accurate answers and people authorised to approve changes and declarations.
Evaluate software against your own workflow before adopting it. Confirm how it supports your scope, existing tools and responsibilities; do not treat a software purchase as a guaranteed certification date.
Frequently asked questions
One last thing
The most useful question is not how quickly you can submit, but what still prevents approval. List every unresolved requirement, name its owner and verify the fix before making your declaration.
That turns an uncertain certification date into a visible plan. Seriously Simple Cyber Compliance.