Blog
Compliance and security guides
Practical guides on ISO 27001, SOC 2, Cyber Essentials, GDPR and NIS2, with costs, timelines, tool comparisons and how to automate your compliance programme.
Latest compliance guides
471 posts
Best vendor risk management software for manufacturing companies
Compare the best vendor risk management software for manufacturing companies. Choose by supplier access, production risk and clear approval workflows.
OneClickComply vs Amtivo: which is better in 2026
OneClickComply vs Amtivo: choose automation for compliance work or independent assessment for certification. Compare scope, ownership and next steps.
VP Networks alternatives in 2026
Compare VP Networks alternatives for 2026. Choose OneClickComply for compliance automation, or consultant-led support for programme leadership and advice.
Best ISO 42001 software for AI companies
Choose the best ISO 42001 software for AI companies by testing system records, impact reviews, approvals and exports. Pick the right platform for your team.
Best vendor risk management software ranked by price 2026
Find the best vendor risk management software ranked by price. Choose by workflow fit, compare matched quotes and check the work your team must handle.
Best compliance automation software for logistics companies
Compare the best compliance automation software for logistics companies. Choose OneClickComply for cyber certification, or match tools to your main gap.
Best penetration testing services for startups
Compare the best penetration testing services for startups. Choose manual web and API testing, define scope, and demand clear reports and retesting.
Best ISO 27001 software ranked by price 2026
Best ISO 27001 software ranked by price: choose by scope and work removed. Compare automation, ISMS and GRC options with a practical buying checklist.
Best policy management software for charities
The best policy management software for charities in 2026, ranked by use case with honest pros and cons, so you can pick the right tool and move on.
Best GRC software for startups
Find the best GRC software for startups in 2026. Compare certification automation, risk registers and policy tools with a practical demo checklist.
Best GRC software for financial services firms
Find the best GRC software for financial services firms. Choose cyber compliance, enterprise risk or audit tools by fit, with clear pros and cons.
Best SOC 2 audit firms in the UK
Best SOC 2 audit firms UK: shortlist Schellman, A-LIGN, BDO and Deloitte. Compare scope, signing authority and report types before choosing your auditor.
Best policy management software for retailers
Find the best policy management software for retailers. Match security automation, document control and staff acknowledgements to your retail workflows.
Best SOC 2 compliance software for healthtech companies
Compare the best SOC 2 compliance software for healthtech companies. Choose by remediation, evidence, monitoring and audit fit, with clear checks.
Best risk register software for construction firms
Compare the best risk register software for construction firms. Choose Microsoft Lists for shared project risks, or match a tool to cyber compliance.
Best compliance automation software for accountancy firms
Choose the best compliance automation software for accountancy firms. Compare cyber certification, workflow and policy tools against your firm's needs.
Best vendor risk management software for recruitment agencies
Best vendor risk management software for recruitment agencies: compare compliance, privacy, workflows and monitoring to choose the right fit for your team.
Best ISO 27001 software for insurance companies
Best ISO 27001 software for insurance companies: OneClickComply leads for growing teams. Compare automation, evidence, monitoring and audit workflows.
Is ISO 27701 certification worth it for a data-driven SaaS company in 2026?
Is ISO 27701 worth it for a SaaS company? Yes, when buyers need privacy assurance. Compare benefits, limits and readiness before you commit to an audit.
How long does it take to build a SOC 2 readiness programme from scratch?
How long does it take to build SOC 2 readiness? Scope and control gaps set the schedule. Separate readiness, evidence collection and audit milestones.
Can a virtual CISO service replace an in-house CISO entirely?
Can a virtual CISO replace an in house CISO? Yes, with clear limits. Compare leadership models, retained responsibilities and the checks to make first.
How much does data mapping software cost for GDPR compliance?
How much does data mapping software cost? Compare scoped quotes, setup work and ongoing reviews to build a GDPR budget around your actual requirements.
Can I get Cyber Essentials certified within a week?
Can you get Cyber Essentials certified in a week? Yes, if you're ready. Check the controls, assessor timing and practical steps before promising a date.
Is penetration testing worth it for a small SaaS company?
Is penetration testing worth it for a SaaS company? Yes, with clear scope and verified fixes. Learn when to test, what to include and how to act.
How much does ISO 14001 certification cost?
How much does ISO 14001 certification cost? It depends on scope. Separate audit fees, preparation and ongoing work to compare UK quotations clearly.
How much does ISO 45001 certification cost?
How much does ISO 45001 certification cost? Get a scoped quote, separate audit fees from preparation, and compare ongoing commitments for your UK business.
Is a GRC platform worth it for a UK SME in 2026?
Is a GRC platform worth it for a UK SME? Yes, when it removes recurring work. Compare manual processes, test real workflows and build your business case.
Best cyber insurance policies for UK small businesses
Hiscox, CFC, Beazley, AXA, Aviva and Simply Business ranked for UK small business cyber insurance in 2026 by coverage, response support and quote access.
Can vendor risk management be fully automated?
Can vendor risk management be automated? Yes, but keep human approval. Learn which tasks to automate, where review matters and how to test your workflow.
How much does ISO 9001 certification cost?
How much does ISO 9001 certification cost? Get a scoped quote, separate audit fees from preparation, and plan for surveillance and recertification.
Can a compliance platform fully replace spreadsheets?
Can a compliance platform replace spreadsheets? Yes, with the right coverage. Check evidence, ownership and exports before retiring your live trackers.
Best Drata alternatives in 2026: an honest comparison
Compare the 7 best Drata alternatives for ISO 27001, SOC 2 and Cyber Essentials, with frameworks, pricing models and who each platform suits best.
Best Vanta alternatives in 2026: an honest comparison
Compare the 7 best Vanta alternatives for ISO 27001, SOC 2 and Cyber Essentials, with frameworks, pricing models and who each platform suits best.
Can you achieve ISO 27001 certification without hiring a consultant?
Can you get ISO 27001 certified without a consultant? Yes. Learn what your team must own, where software helps and why independent audits still matter.
Can one platform manage both ISO 27001 and SOC 2 at the same time?
Can one platform manage ISO 27001 and SOC 2? Yes. Share controls and evidence, keep audits separate, and check what your compliance platform must handle.
Can a small business self-certify for Cyber Essentials without an assessor?
Can you self certify Cyber Essentials? You can complete the assessment yourself, but an assessor must approve it. See the steps and how Plus differs.
How much does an NHS DSPT submission cost?
How much does NHS DSPT submission cost? Budget for staff time, evidence and support. See what changes the workload and how to compare supplier quotes.
Can compliance automation software replace a full-time compliance manager?
Can compliance automation software replace a compliance manager? Not completely. See what to automate, who owns decisions and when you need to hire.
Can AI accurately complete security questionnaires?
Can AI accurately complete security questionnaires? Yes, with evidence and review. Learn how to check claims, handle gaps and approve accurate answers.
How much does it cost to migrate from spreadsheets to a compliance platform?
Budget the cost to migrate from spreadsheets to a compliance platform. Separate software, setup and staff time, then compare scope before approving a move.
How much does vendor risk management software cost?
How much does vendor risk management software cost? Compare scoped quotes, setup work and internal effort to build a budget that covers your supplier assessments.
How much does risk register software cost?
How much does risk register software cost? Compare the full scope, not just subscriptions. Check setup, migration, support and internal work before you commit.
How much does policy management software cost?
How much does policy management software cost? Budget beyond the subscription. Compare scope, setup, staff time and renewal terms before you choose a platform.
How much does a GDPR data protection impact assessment cost?
How much does a DPIA cost? Scope sets the budget. Compare assessment routes, check quote exclusions and plan separately for changes needed to reduce risks.
How much does ISO 22301 business continuity certification cost?
How much does ISO 22301 certification cost? Get a scope-based answer, separate audit fees from preparation, and compare quotes for your UK business in 2026.
How much does ISO 27701 certification cost?
How much does ISO 27701 certification cost? Get a scope-based quote, separate audit fees from preparation, and plan staff time and ongoing compliance work.
How long does vendor security due diligence take during onboarding?
How long does vendor due diligence take? Scope sets the schedule. Plan evidence requests, resolve blockers and assign approvals before your supplier goes live.
How long does it take to respond to a security questionnaire?
Security questionnaire response time depends on evidence, scope and approval. Build a realistic delivery plan, reuse checked answers and manage buyer follow-up.
How long does an ISO 42001 gap analysis take?
How long does an ISO 42001 gap analysis take? Scope determines the timetable. Learn what to prepare, what affects duration and how to avoid assessment delays.
How long does a penetration test take?
How long does a penetration test take? Scope sets the schedule. Separate testing, reporting, fixes and retesting to agree a realistic deadline before you book.
How long does a GDPR data protection impact assessment take?
How long does a DPIA take? There is no fixed GDPR deadline. Learn what controls the timeline, when ICO consultation applies and how to plan before launch.
Best ISO 27001 software for startups
The best ISO 27001 software for startups in 2026: OneClickComply, Vanta, Drata, Secureframe, Sprinto and Scrut compared on evidence automation, setup speed and audit support.
How long does a SOC 2 Type II audit take?
How long does a SOC 2 Type II audit take? Plan beyond the observation period. Understand preparation, auditor testing and report delivery before you commit.
How long does ISO 27001 certification take?
How long does ISO 27001 certification take? No fixed timeline applies. Plan around readiness, evidence, audit bookings and the final certification decision.
How long does Cyber Essentials certification take?
How long does Cyber Essentials certification take? Readiness sets the pace. Plan preparation, assessor review and Cyber Essentials Plus checks for 2026.
Is GDPR compliance software worth it for a small business in 2026?
Is GDPR compliance software worth it? Yes, when it reduces recurring privacy work. Compare manual processes, software and advice before your business buys.
Is ISO 42001 certification worth it in 2026?
Is ISO 42001 worth it? Yes, when buyer requirements or AI risks justify certification. Compare your options, check readiness and decide your next step in 2026.
Is outsourcing your DPO worth it in 2026?
Is outsourcing a DPO worth it? Yes, with clear scope and independent advice. Compare internal and external roles, check UK GDPR duties and define ownership.
Is compliance automation software worth it for a small business in 2026?
Is compliance automation software worth it? Yes, when it removes repeat work. Compare manual processes, test evidence workflows and build your business case.
Is a virtual CISO worth it for a growing startup in 2026?
Is a virtual CISO worth it? Yes, when your startup needs security leadership. Compare options, define the scope and separate advice from implementation in 2026.
Is Cyber Essentials worth it for a small business in 2026?
Is Cyber Essentials worth it for your small business? Yes, when buyers require it or you need a security baseline. Compare both levels and decide what fits.
Is ISO 27001 certification worth it for a SaaS startup in 2026?
Is ISO 27001 worth it for a SaaS startup? Yes, when buyers require it. Compare certification, preparation and deferral to choose your next step clearly in 2026.
Is SOC 2 compliance worth it for an early-stage startup in 2026?
Is SOC 2 worth it for a startup? Start when buyers require it. Compare Type I and Type II, assess readiness and decide when to audit without overcommitting.
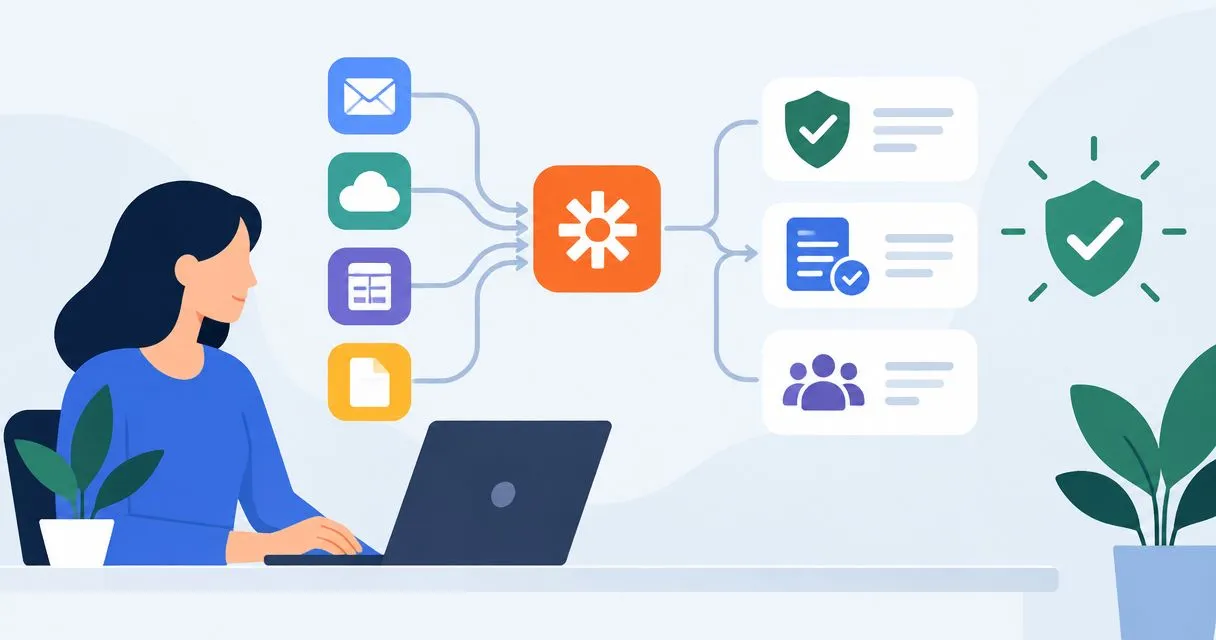
Zapier to no-code compliance automation: complete 2026 workflow
Zapier compliance automation: route evidence for review, check repeat submissions and test failures. Build a no-code workflow without automating audit approval.
AWS to continuous ISO 27001 evidence: complete 2026 workflow
AWS ISO 27001 evidence collection: automate AWS records, map controls and retain review history. Follow the 2026 workflow without treating exports as proof.
How to connect ChatGPT and Claude to your compliance platform
Connect ChatGPT and Claude to your compliance platform with MCP. Start read-only, test access, verify evidence sources and keep record changes behind approval.
GitHub commits to SOC 2 evidence: complete 2026 workflow
Build GitHub SOC 2 evidence with approvals, checks and deployment links, not commits alone. Follow the setup, validate records and reconcile missed changes.
Slack to instant audit alerts: complete 2026 workflow
Slack audit alerts compliance: use event-driven notifications, keep evidence in its source, and test ownership, duplicate handling and delivery before launch.
Automatically enrol new hires in security training via HR sync
HR system security training automation should enrol eligible hires once. Set up HR sync, prevent duplicate assignments and retain evidence of training completion.
How to connect Jira to automatic risk remediation tracking
Build a Jira risk register integration that tracks remediation without closing risks too early. Map fields, prevent duplicate tasks and verify evidence in 2026.
Risk register software for universities: complete 2026 guide
Choose risk register software for higher education institutions around ownership, evidence and reporting. Compare options and test your university workflow.
Google Workspace to ISO 27001 evidence: complete 2026 workflow
Build Google Workspace ISO 27001 evidence with scoped exports, verified API collection and documented reviews. Keep audit records traceable and access clear.
How to connect Microsoft 365 to your compliance evidence library
Connect Microsoft 365 compliance evidence safely with SharePoint and Power Automate. Set permissions, test file collection and keep reviewed audit records clear.
Policy management software for retailers: complete 2026 guide
Choose policy management software for retail and e-commerce brands by workflow, not features. Compare options, test staff access and keep approval evidence.
SOC 2 compliance for healthtech companies: complete 2026 guide
Choose SOC 2 compliance software for healthtech companies by audit fit. Define scope, protect patient data and compare manual, automated and advised routes.
ISO 27001 software for public sector suppliers: complete 2026 guide
ISO 27001 software for public sector suppliers should support your contract scope. Compare approaches, manage evidence and prepare for independent audits.
ISO 27001 software for manufacturers: complete 2026 guide
ISO 27001 software for manufacturing companies: OneClickComply suits growing firms seeking automation. Scope systems, assign owners and check audit evidence.
Risk register software for construction firms: complete 2026 guide
Risk register software for construction and engineering firms needs clear owners and review triggers. Compare options and keep cyber risks separate from site safety.
Policy management software for healthcare: complete 2026 guide
Policy management software for healthcare providers needs clear owners, versions and approvals. See when OneClickComply fits cyber certification, not clinical policy.
Amtivo alternatives for ISO 27001 certification
Compare amtivo alternatives for ISO 27001 in 2026. Choose OneClickComply to manage compliance work, or compare certification bodies for an independent audit.
Compliance automation for construction firms: complete 2026 guide
Compliance automation for construction and engineering firms starts with scope. OneClickComply suits growing firms managing cyber certification work end-to-end.
Compliance automation for life sciences firms: complete 2026 guide
Compliance automation for pharmaceutical and life sciences companies starts with a clear cyber scope. Compare options and keep regulated quality decisions separate.
Best Sprintlaw alternatives for UK startups
Compare Sprintlaw alternatives for UK startups in 2026. Choose OneClickComply for cyber compliance management or a UK solicitor when you need legal advice.
LegalVision alternatives in 2026
Compare LegalVision alternatives in 2026. Choose OneClickComply to manage cyber certification, Lawhive for legal advice or Vanta for compliance software.
Rocket Lawyer alternatives in 2026
Compare Rocket Lawyer alternatives in 2026. OneClickComply is the choice for ISO 27001, Cyber Essentials and SOC 2; see when legal document tools fit instead.
Best SOC 2 compliance software ranked by price 2026
Best SOC 2 compliance software ranked by price: OneClickComply is the multi-framework pick for 2026. Compare Vanta and Drata using a practical quote checklist.
Best compliance automation software for e-commerce brands
OneClickComply leads for e-commerce brands running ISO 27001, Cyber Essentials and SOC 2 together in 2026 — compared against Vanta, Drata, Secureframe and Sprinto.
LexisNexis alternatives in 2026
Compare LexisNexis alternatives for compliance and vendor risk in 2026: OneClickComply automates ISO 27001, SOC 2 and Cyber Essentials evidence collection.
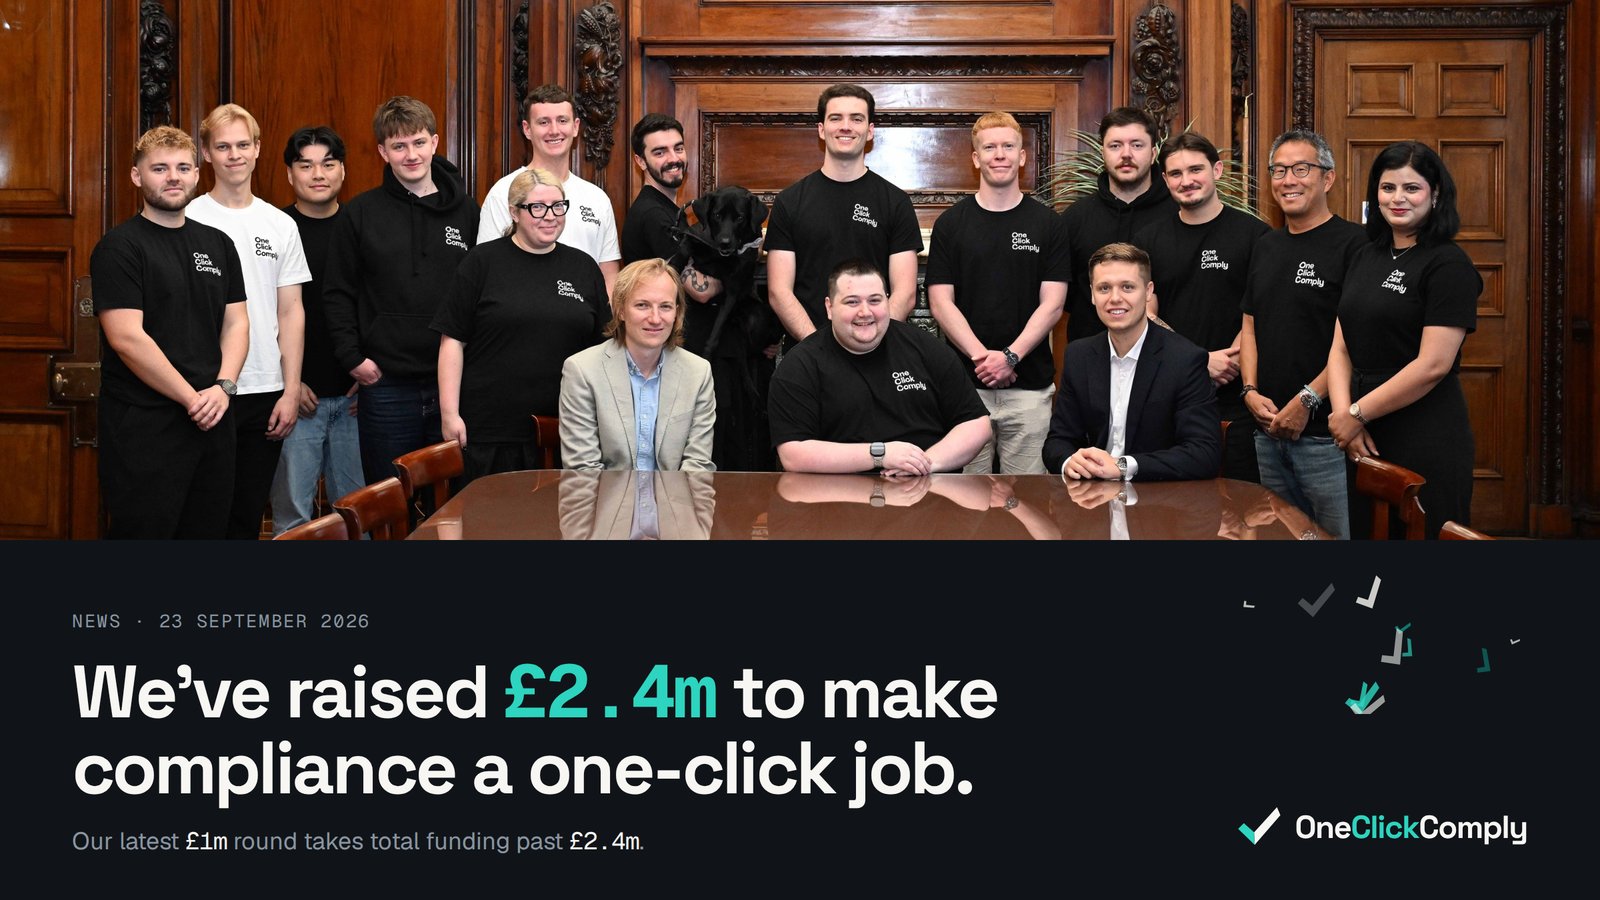
We've raised £2.4m to make compliance a one-click job
Our latest £1m round, from the North East Accelerate Fund, Venture Sunderland Fund and Northstar EIS Growth Fund, takes total funding past £2.4m.
Best compliance automation software ranked by price 2026
Best compliance automation software ranked by price model for 2026: OneClickComply wins overall, plus Vanta, Drata, Sprinto and Scrut Automation compared.
Best GRC platforms for UK SMEs
OneClickComply tops the 2026 ranking of the best GRC platforms for UK SMEs, compared against Vanta, Drata, ISMS.online, Secureframe and Sprinto.
Best GRC software for MSPs
OneClickComply tops the ranked list of the best GRC software for MSPs in 2026, covering ISO 27001, Cyber Essentials and SOC 2 across client accounts.
Best ISO 27001 software for healthcare providers
OneClickComply leads the best ISO 27001 software for healthcare providers in 2026 — compared against Vanta, Drata, Secureframe, Sprinto and ISMS.online.
Best ISO 27001 software for fintech firms
OneClickComply ranks best ISO 27001 software for fintech firms in 2026 — compared against Vanta, Drata, Secureframe and Sprinto by use case, not features.
Best ISO 27001 software for law firms
OneClickComply ranks best ISO 27001 software for law firms in 2026, compared against Vanta, Drata, Secureframe, ISMS.online and Sprinto on features that matter.
Best compliance automation software for professional services firms
Compare the best compliance automation software for professional services firms in 2026. See which option fits lean teams, broad frameworks and guided audits.
Best compliance automation software for banks
OneClickComply leads our 2026 ranking of compliance automation software for banks, compared against Vanta, Drata, OneTrust, Ncontracts and MetricStream.
Best compliance automation software for insurance underwriters
See the best compliance automation software for insurance underwriters in 2026, ranked for evidence collection, framework coverage, vendor risk and team fit.
Best compliance automation software for UK SMEs
Compare the best compliance automation software for UK SMEs in 2026 — OneClickComply, Vanta, Drata, Secureframe, and DIY tracking, ranked with pros and cons.
Best compliance automation software for startups
See which compliance automation software fits startups best in 2026 - OneClickComply, Vanta, Drata, Secureframe and Sprinto compared on frameworks and speed.
Best SOC 2 compliance software for startups
OneClickComply leads for startups needing SOC 2 plus ISO 27001 in 2026, compared against Vanta, Drata, Secureframe and Sprinto on evidence automation.
Best SOC 2 compliance software for UK SaaS companies
OneClickComply is the best SOC 2 compliance software for UK SaaS companies in 2026, automating evidence collection across SOC 2, ISO 27001, and Cyber Essentials.
Best SOC 2 compliance software for fintech companies
Compare the best SOC 2 compliance software for fintech companies in 2026 — OneClickComply, Vanta, Drata, Secureframe, and Sprinto, ranked by use case.
Best Risk Register Software for UK SMEs (2026)
Best risk register software for UK SMEs in 2026: OneClickComply wins for ISO 27001 and Cyber Essentials programmes. Compare tools, pros, cons and pricing notes.
Best Risk Register Software for MSPs in 2026
OneClickComply ranks the best risk register software for MSPs in 2026 — compare picks for multi-client ISO 27001, Cyber Essentials, and SOC 2 registers.
Best Risk Register Software for Financial Services 2026
Best risk register software for financial services firms in 2026: OneClickComply wins for ISO 27001, SOC 2 and DORA automation. Compare 6 platforms and pick.
Best Policy Management Software for UK SMEs (2026)
Compare the best policy management software for UK SMEs in 2026. OneClickComply, Vanta, Drata and OneTrust ranked with honest pros, cons and best-for labels.
Best Policy Management Software for HR Teams (2026)
OneClickComply leads our 2026 ranking of policy management software for HR teams, compared against PowerDMS, MetaCompliance, NAVEX, and Confluence.
Best Policy Management Software for Financial Services 2026
OneClickComply ranks best for financial services policy management in 2026, covering ISO 27001, SOC 2, Cyber Essentials, and DORA in one platform.
Virtual CISO Services for Universities: 2026 Verdict
Virtual CISO services for universities compared for 2026: governance, vendor risk and automated audit evidence for higher education institutions.
Compliance Automation for Payroll Software Providers 2026
Compliance automation for payroll software providers in 2026: map SOC 2, ISO 27001, Cyber Essentials and PCI DSS, then automate evidence with OneClickComply.
Best ISO 27001 Software for MSPs 2026: OneClickComply Wins
Compare the best ISO 27001 software for MSPs in 2026 — OneClickComply, Vanta, Drata, Secureframe, and Sprinto — with honest pros, cons, and verdicts.
Cyber Essentials for Estate Agents: 2026 Guide
Cyber Essentials for estate agents in 2026: the five controls, renewal rules, and why corporate landlords now require it. Manual steps plus the faster automated route.
Compliance Automation for Insurtech Startups (2026)
Compliance automation for insurtech startups in 2026: ISO 27001, SOC 2, and Cyber Essentials steps, comparison table, and how OneClickComply automates evidence.
Vulnerability Management for Kubernetes: 2026 Guide
Vulnerability management for Kubernetes in 2026: image scanning, runtime detection, patch cadence, and mapping scan output to ISO 27001 and SOC 2 evidence.
Compliance Automation for Challenger Banks: 2026 Guide
Compliance automation for challenger banks in 2026: map ISO 27001, SOC 2, Cyber Essentials and operational resilience in one evidence library, not five audits.
DORA Compliance for Cloud Service Providers: 2026 Guide
DORA compliance for cloud service providers explained: gap analysis, third-party risk register, and contract clauses to pass 2026 client due diligence.
Vendor Risk Management for Pension Providers (2026)
Vendor risk management for pension providers in 2026: how to tier suppliers, automate due diligence, and stay ahead of TPR and DORA third-party rules.
ISO 27001 for MSPs (2026): Requirements & Verdict
ISO 27001 for MSPs in 2026: scope your ISMS across client tenants, automate evidence collection, and pass audits. See what actually works and what fails.
Best DPIA Software UK 2026: Ranked and Reviewed
Best DPIA software UK 2026 ranked: OneClickComply wins overall, OneTrust for enterprise, DPOrganizer for budget. Compare features, pros, cons and verdicts.
Best Cyber Security Tabletop Exercise Providers UK 2026
Compare cyber security tabletop exercise providers UK firms use in 2026: NCSC-assured, CREST-accredited, retainer and insurer-panel options ranked with verdicts.
Best Cloud Access Security Broker UK Picks for 2026
Compare the best cloud access security broker UK options for 2026 — Microsoft Defender for Cloud Apps, Netskope, and Skyhigh Security ranked by use case.
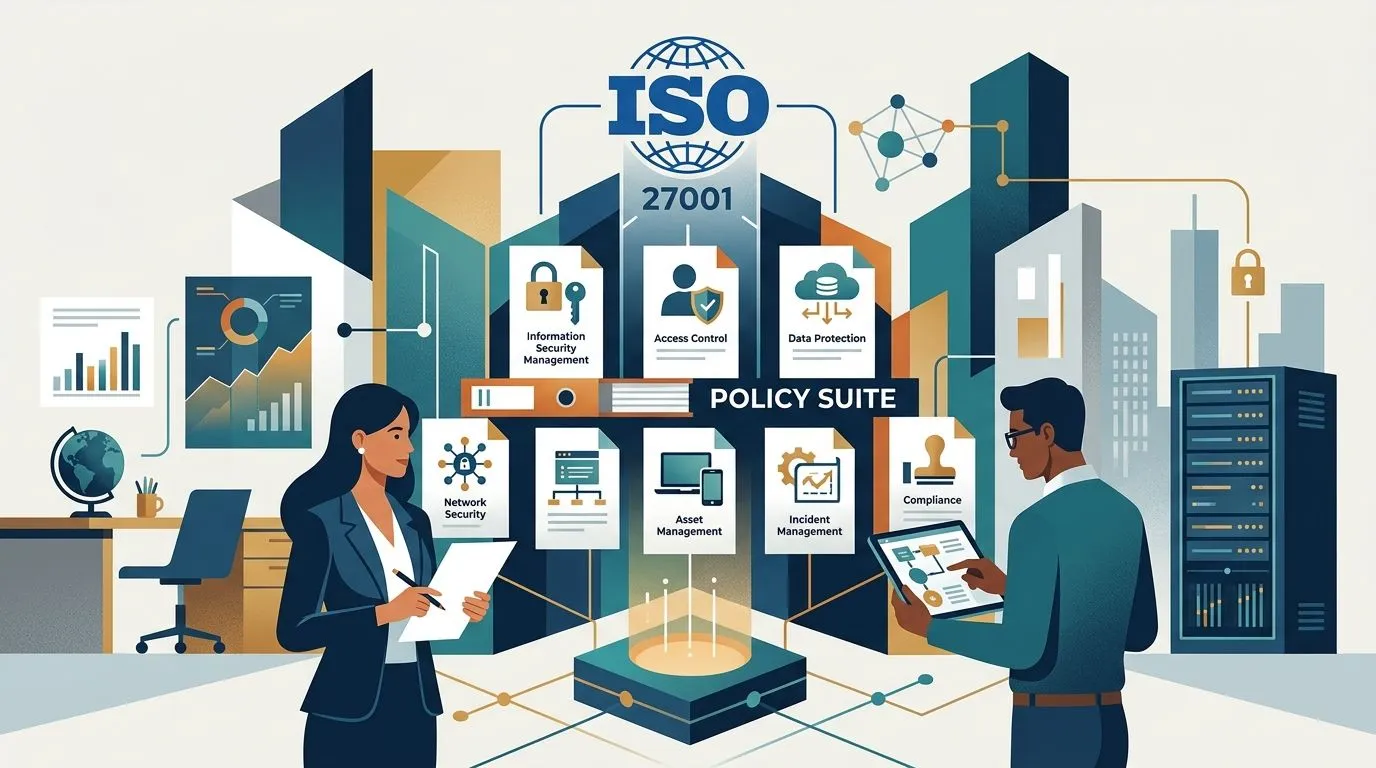
Information Security Policy Suite for ISO 27001 (2026)
How to write an information security policy suite for ISO 27001: 93 Annex A controls, 4 themes, and a step-by-step build order for 2026 certification.
Penetration Testing Open Banking API: 2026 Verdict
Penetration testing for open banking APIs in 2026: what CREST-accredited testing covers, PSD2 and DORA requirements, and how to scope a fintech API test.
Best Managed Vulnerability Scanning Services UK 2026
Intruder tops managed vulnerability scanning services UK businesses trust in 2026. Compare Tenable, Qualys, Rapid7, Holm Security and Bulletproof by use case.
Compliance Automation for Insurance Underwriters 2026
Compliance automation for insurance underwriters in 2026: automate ISO 27001, Cyber Essentials and SOC 2 evidence and cut questionnaire turnaround to hours.
How to Build a Cyber Security Risk Register (2026)
A cyber security risk register scores each risk, assigns an owner, and maps it to ISO 27001 Annex A controls - build a working register in 7 steps for 2026.
Board Cyber Security Governance Training: 2026 Guide
Board cyber security governance training explained: what to cover, how often, and who leads it. Practical 2026 framework for directors and compliance leads.
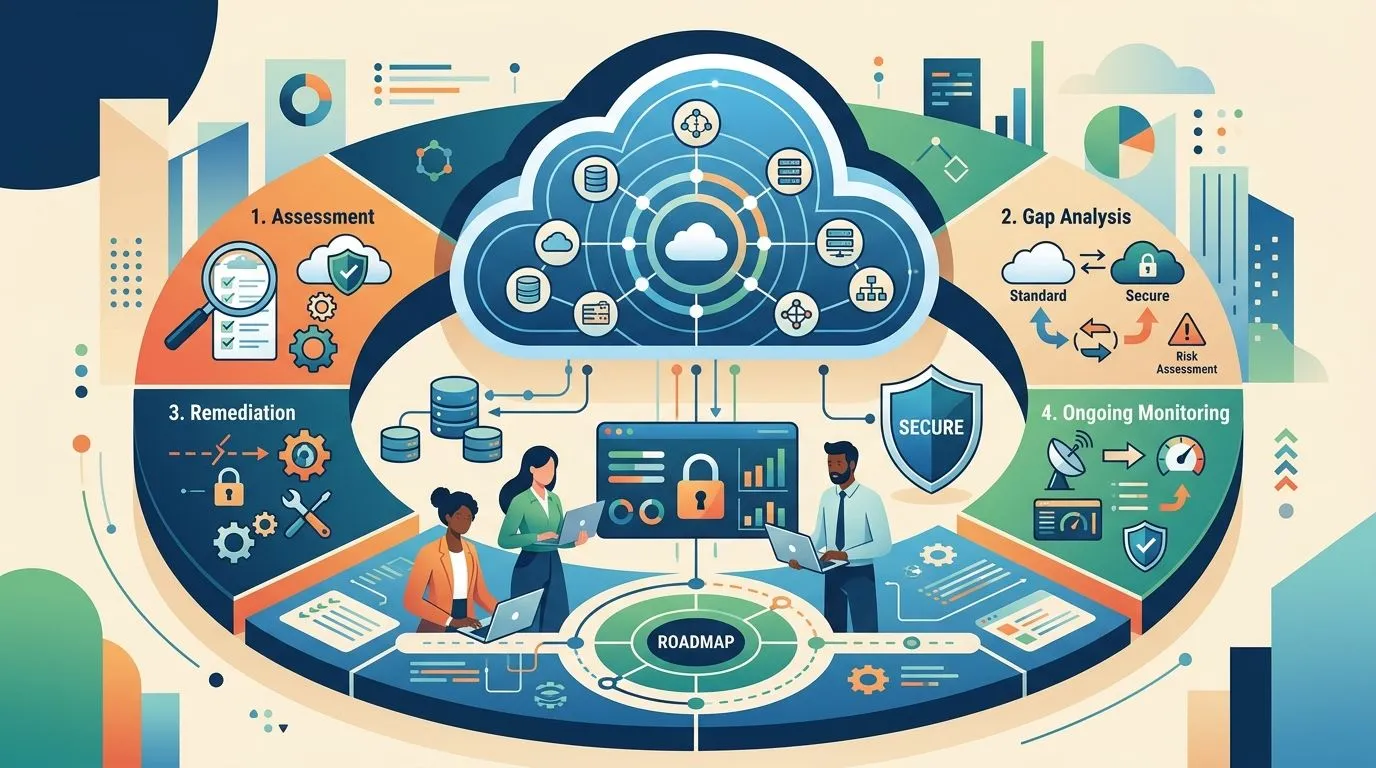
Cloud Security Configuration Review Programme: Build It Right 2026
Build a cloud security configuration review programme in 2026: pick a baseline, set cadence, automate evidence. Steps, frameworks, and FAQ inside.
Best Outsourced DPO Services for UK Charities (2026)
The DPO Centre, DPO Solutions, and 3 more outsourced DPO services for UK charities ranked for 2026 - pros, cons, and which fits your charity's risk.
Best Managed Firewall Services for UK SMEs in 2026
Compare managed firewall services for UK SMEs in 2026 - Sophos, Meraki, Fortinet, WatchGuard, SonicWall, and MSP-managed options ranked by fit and audit-readiness.
Best Outsourced SOC Services for UK SMEs (2026)
Compare outsourced SOC service models for UK SMEs in 2026 — MDR, managed SIEM, vCISO oversight and compliance-integrated monitoring, with clear best-for picks.
GDPR Compliance for AI & ML Companies (2026 Guide)
GDPR compliance for AI and machine learning companies in 2026: lawful basis, DPIAs, Article 22, and how OneClickComply automates the evidence.
Best Vulnerability Disclosure Platforms UK 2026
HackerOne, Intigriti, Bugcrowd, YesWeHack and Open Bug Bounty compared for UK businesses — the best vulnerability disclosure programme platform for 2026 by team size.
GDPR Training for UK SME Employees: 2026 Guide
GDPR data protection training for UK SME employees in 2026: role-based modules, tracked completions and refresh cycles that pass audits. What works, what fails.
Best Whistleblowing Software UK (2026): Top 6 Ranked
Compare the best whistleblowing software UK firms use in 2026 - NAVEX, Safecall, WhistleB, Vault Platform, Whispli and EQS ranked by use case and limits.
Best ESG Reporting Software for UK SMEs in 2026
Position Green leads our 2026 ranking of ESG reporting software for UK SMEs, compared against Greenly, Coolset, Normative, Sweep and Diligent ESG.
International Data Transfer Agreements UK GDPR (2026)
IDTA or UK Addendum? Learn how to set up international data transfer agreements under UK GDPR in 2026, including TRAs and adequacy decisions.
IT Asset Management for ISO 27001 Inventories (2026)
IT asset management for ISO 27001 explained: build, classify, and automate your asset inventory before your 2026 audit. Steps, tools, and common mistakes.
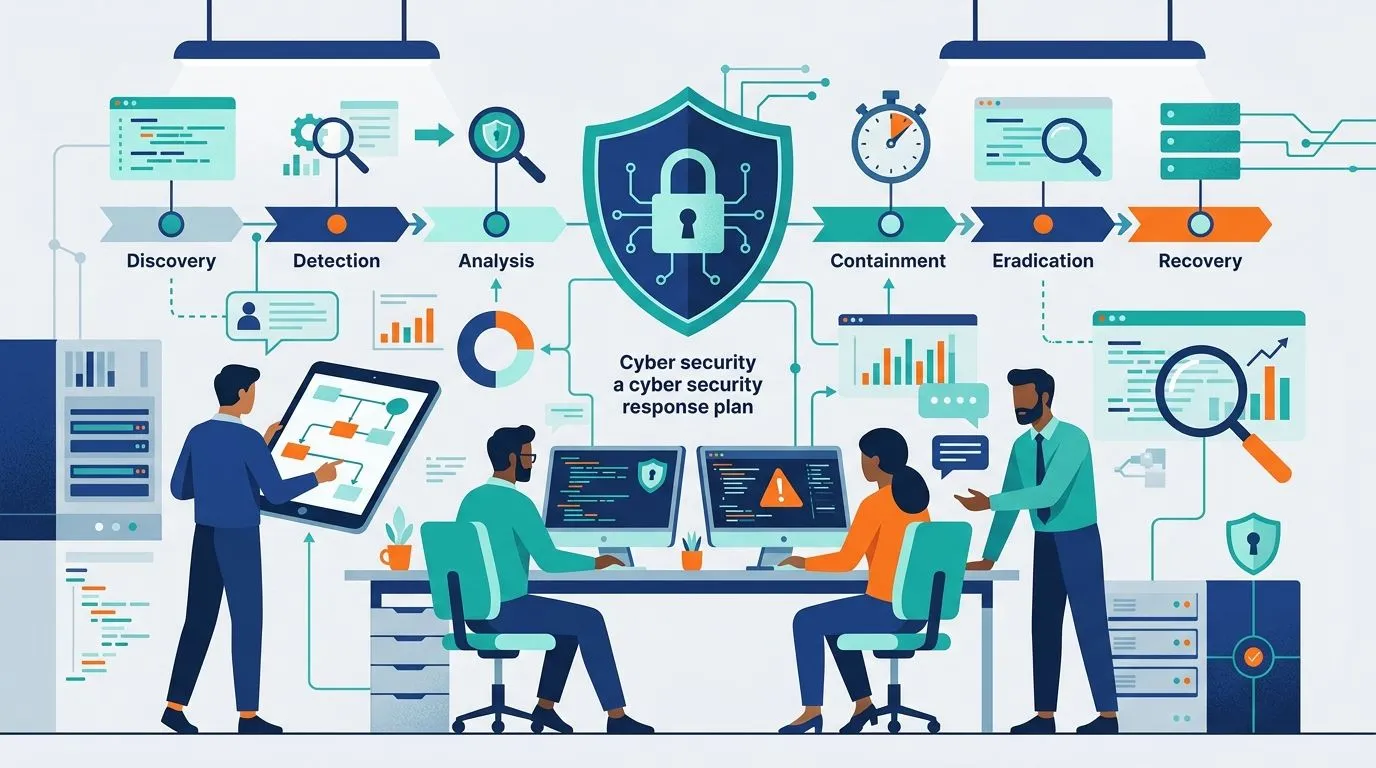
Cyber Security Incident Response Plan: Build One in 2026
How to build a cyber security incident response plan in 2026: the four phases, named team roles, GDPR's 72-hour ICO deadline, and how often to test it.
Best Phishing Simulation Platform UK SMEs Pick (2026)
See which phishing simulation platform UK SMEs should buy in 2026 — usecure, KnowBe4, Hoxhunt and more ranked on setup, templates and reporting.
Best Business Continuity Management Software UK 2026
OneClickComply leads our 2026 ranking of business continuity management software for UK SMEs, compared against Noggin, Fusion Risk, Veoci, and Onspring.
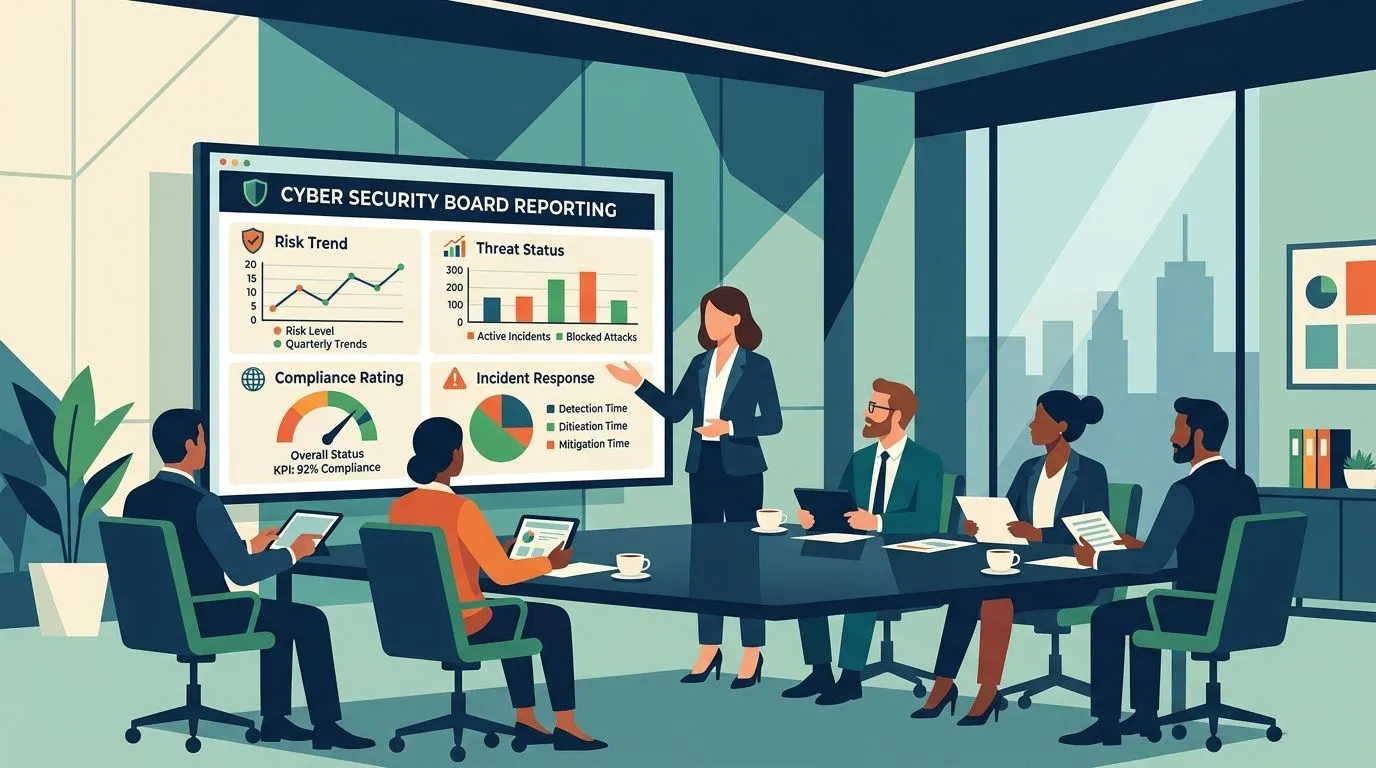
Cyber Security KPIs Board Reporting: 2026 Verdict & Metrics
Cyber security KPIs board reporting works with 5-8 metrics, quarterly cadence. See which KPIs matter in 2026 and how OneClickComply keeps them current.
Cyber Security Due Diligence for M&A Deals (2026 Guide)
How to run cyber security due diligence for M&A deals in 2026: pre-LOI screen, vendor risk checks, and what a failed review means for valuation.
Threat Intelligence Services for UK Financial Firms 2026
Threat intelligence services for financial services firms in 2026: DORA-linked feeds, red team testing, and the evidence trail auditors actually accept.
Cyber Essentials Scheme Changes 2026: What to Prepare For
The 2026 Cyber Essentials scheme changes keep the same 5 control themes but tighten MFA and patch enforcement — here's exactly how to prepare before renewal.
Cyber Security Audit for Small Business: 2026 Guide
A cyber security audit for a small business runs in six steps, from scope to remediation. See what Cyber Essentials and ISO 27001 audits check in 2026.
Managed SIEM for MSPs in 2026: What Actually Scales
Managed SIEM for MSPs in 2026 compared: open source, commercial multi-tenant, and outsourced SOC options, plus how to automate the compliance evidence.
IASME Governance Certification for Charities: 2026 Guide
IASME Governance certification for charities and non-profits: what it covers, the step-by-step process, and how to avoid failed self-assessments in 2026.
Outsourced Compliance Manager Services UK: 2026 Picks
Compare outsourced compliance manager services for UK SMEs in 2026 — vCISOs, GRC consultants, fractional managers, and automation software — with real verdicts.
SOC 2 Cost UK 2026: £10k-£60k Price Breakdown
SOC 2 compliance cost UK SaaS companies £10,000-£60,000 in 2026. See the full audit, readiness, software and staff-time breakdown before you set a budget.
Virtual CISO Cost in 2026: What Drives the Price
Virtual CISO cost in 2026 depends on engagement model, scope and cert targets like ISO 27001 or SOC 2 — compare day rate, retainer and project pricing.
GDPR Compliance Checklist for UK Startups (2026 Guide)
Build a GDPR compliance checklist for UK startups in 2026: lawful basis, RoPA, DPIA, breach response, DSAR process, and how to keep it current past month one.
ISO 27001 Internal Audit: How to Run One in 2026
Learn how to run an ISO 27001 internal audit in 2026: steps, evidence, timing, and why OneClickComply automates the hardest part end-to-end.
Cyber Security Maturity Assessment: How to Run One (2026)
A cyber security maturity assessment scores your controls from ad hoc to optimised in 2026 — see which framework to use and where to fix gaps first today.
Best Consent Management Platform UK Picks 2026
OneTrust, Cookiebot, Usercentrics and more ranked for UK businesses in 2026 — compare features, limitations and which consent management platform fits.
Business Impact Analysis for ISO 22301: 2026 Steps
Conduct a business impact analysis for ISO 22301 in 2026: define scope, set RTO and RPO, then map findings straight into your BCMS audit trail.
Best Data Mapping Software for GDPR Compliance 2026
Compare the best data mapping software for GDPR compliance in 2026 — OneClickComply, OneTrust, BigID, Securiti, Osano and Collibra ranked by use case.
Policy Management Software for Compliance Teams (2026)
Policy management software compliance tools cut manual tracking for growing teams. See how OneClickComply automates sign-off and audits in 2026.
Best CREST Accredited Penetration Testing UK (2026)
Six CREST accredited penetration testing providers in the UK for 2026, ranked by use case with honest pros, cons and a clear verdict for each.
Best Automated Penetration Testing Tools for UK Firms 2026
The best automated penetration testing tool in 2026 depends on use case: Intruder wins overall, Astra Security for compliance evidence, Pentera for enterprise.
Risk Register Software for ISO 27001: 2026 Guide
Risk register software for ISO 27001 in 2026: score risks, map them to Annex A, and automate evidence. Compare spreadsheets, GRC tools and OneClickComply.
Ransomware Readiness Assessment: How to Run One in 2026
Run a ransomware readiness assessment in 2026: test backup restoration, tabletop your incident response and close control gaps before attackers find them.
Managed Detection and Response for UK SMEs (2026)
Managed detection and response for UK SMEs compared: what Cyber Essentials Plus and ISO 27001 require, and how to automate the audit evidence in 2026.
Best Outsourced DPO Services UK 2026: Ranked Guide
Outsourced DPO services UK compared for 2026 — consultancies, law firm retainers, freelance DPOs and software-supported models, ranked with clear verdicts.
Best Incident Response Retainer Services UK 2026
NCC Group, Bridewell, and S-RM lead the best incident response retainer services in the UK for 2026 — compare coverage, sector fit, and response models here.
PCI DSS v4.0 Compliance: How to Prepare in 2026
PCI DSS v4.0 compliance is mandatory in 2026 — the exact 6-step prep checklist, merchant levels, and the control most programmes still fail.
CIS Controls v8 Implementation Guide for UK Firms 2026
CIS Controls v8 implementation starts with IG1's 56 safeguards. Compare all 3 Implementation Groups and follow the 2026 step-by-step UK rollout plan.
ISO 27001 Statement of Applicability: How to Complete It (2026)
Complete an ISO 27001 statement of applicability across all 93 Annex A controls with justifications, evidence links, and a 2026 audit-ready template.
Security Awareness Training for Retail Teams 2026
Security awareness training for retail teams in 2026: role-specific modules, phishing simulations, and audit-ready evidence with OneClickComply.
GDPR Privacy Notice: How to Write One in 2026
A GDPR privacy notice needs clear disclosures on data use, legal basis and retention. Steps to write, publish and update one correctly in 2026.
NIS2 Directive Compliance UK: How Suppliers Prepare in 2026
NIS2 doesn't bind UK firms directly, but EU customers will demand proof of controls in 2026. Steps UK suppliers need to prepare, ranked by fine tier.
GDPR Data Processing Agreement Checklist 2026
See the 7 mandatory clauses a GDPR data processing agreement checklist needs in 2026, plus the sub-processor gap most contracts miss.
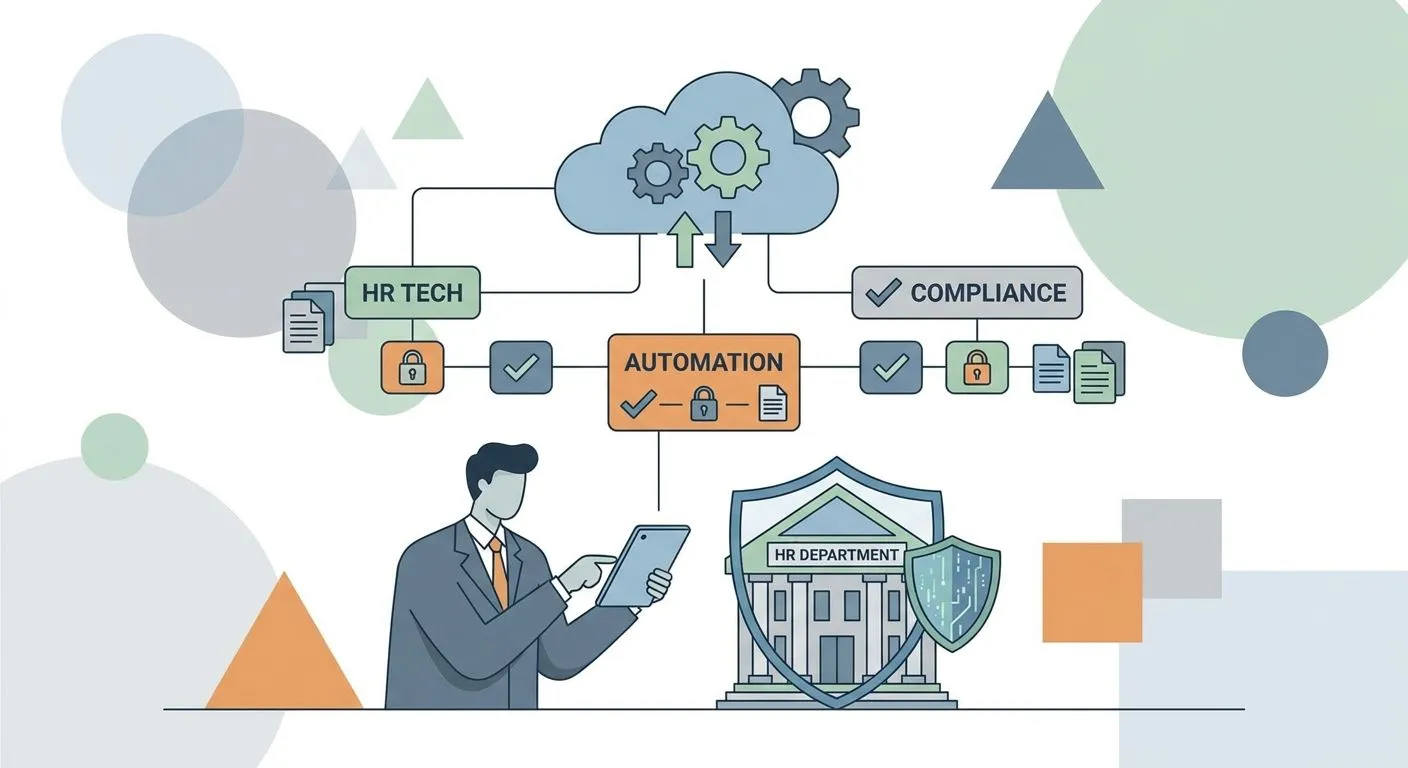
Compliance Automation for HR Tech Platforms in 2026
Compliance automation for HR tech platforms in 2026: automate SOC 2 and ISO 27001 evidence collection with OneClickComply and skip the spreadsheet grind.
Cyber Essentials for Automotive Dealerships: 2026 Guide
Cyber Essentials for automotive dealerships in 2026: the 5 controls, DMS and service bay scoping, renewal timing, and how multi-site dealer groups certify fast.
Best GDPR Compliance Software for Law Firms 2026
OneClickComply leads our 2026 ranking of GDPR compliance software for law firms, compared against OneTrust, Vanta, Drata, and PrivacyEngine on real criteria.
Cyber Essentials for Security Firms: 2026 Guide
Cyber Essentials for security firms explained: scope, the five controls, Plus vs base, and how to renew for 2026 guarding and government contracts.
Trust Centre Software for API Platforms: 2026 Picks
Trust centre software for API and developer platforms in 2026: what to publish, which controls matter, and how OneClickComply keeps evidence current.
Security Questionnaire Automation for Healthcare (2026)
Security questionnaire automation for healthcare vendors: cut response time with evidence libraries, templates, and AI. OneClickComply keeps certificates current in 2026.
Vendor Risk Management Software for SaaS (2026 Guide)
Vendor risk management software saas teams trust in 2026: automate vendor scoring, evidence collection and audits with OneClickComply. See how it works.
Vendor Risk Management Software for Logistics: 2026 Verdict
Vendor risk management software for logistics in 2026: tiering, due diligence, and renewal automation compared, with OneClickComply's verdict for fleets past 12 vendors.
Compliance Automation for Fintech Lenders (2026 Guide)
Compliance automation for fintech lenders: how ISO 27001, SOC 2, and DORA evidence gets automated in 2026, plus the steps and tools that cut audit prep time.
Vendor Risk Management Software for Professional Services 2026
Vendor risk management software for professional services firms in 2026: OneClickComply automates vendor tracking, questionnaires and certification evidence.
Virtual CISO Retail: Which Model Wins in 2026
Virtual CISO retail guide for 2026: which vCISO model fits card payments, multi-site chains and e-commerce brands, with clear Buy or Consider verdicts.
Virtual CISO Professional Services: 2026 Buying Guide
Virtual CISO professional services compared for 2026: fractional retainer wins for law firms and accountancies. See the models, verdicts, and what to skip.
Virtual CISO for Financial Services: 2026 Buyer's Guide
Virtual CISO for financial services firms compared for 2026 — regulatory fit, cost models, and DORA readiness, with a clear Buy, Consider, or Skip verdict.
Compliance Automation Wealth Management Firms 2026
Compliance automation wealth management guide for 2026: what to look for, top picks, DORA and FCA fit, and verdicts on vendor risk and audit tools.
Compliance Automation for Logistics Companies 2026
Compliance automation for logistics and supply chain companies in 2026: Cyber Essentials, vendor risk management, and ISO 27001 compared with clear verdicts.
Best Penetration Testing Services UK (Enterprise 2026)
Penetration testing services UK enterprise teams can trust in 2026: CREST and CHECK providers ranked with verdicts for ISO 27001 and PCI DSS compliance.
Red Team Testing for UK Financial Services (2026)
Red team testing for UK financial services firms: what to look for, which approach to buy, and how DORA's 3-year TLPT cycle affects your 2026 testing plan.
Penetration Testing Microsoft 365: What to Buy in 2026
Penetration testing microsoft 365 guide for UK SMEs: what to test, what to skip, and which engagement type to buy in 2026. Compare the options now.
Wireless Network Penetration Testing: What to Buy in 2026
Wireless network penetration testing in 2026: what to scope, which tests to buy, and what to skip before your next Cyber Essentials Plus or ISO 27001 audit.
Social Engineering Penetration Testing: 2026 Buyer Guide
Social engineering penetration testing for UK SMEs in 2026: which tests to run, which to skip, and how results map to ISO 27001, SOC 2 and Cyber Essentials.
GDPR Subject Access Request: Response Steps for 2026
Answer a GDPR subject access request within the UK's one-month deadline in 2026. Follow the step-by-step process, ICO rules, and tools to locate data fast.
GDPR Data Protection Officer: How to Appoint One in 2026
Learn when a GDPR data protection officer is mandatory, how to appoint one correctly, and how to avoid the conflicts of interest that fail ICO checks in 2026.
GDPR Data Breach Notification: 72-Hour Rule (2026)
GDPR data breach notification in 2026: the 72-hour ICO deadline, when to notify individuals, and the exact steps to avoid a £17.5m fine.
GDPR Data Retention Policy: Build One in 2026
Build a GDPR data retention policy in 2026: inventory your data, set periods per category, automate deletion, and hold up under ICO scrutiny. Step by step.
GDPR Record of Processing Activities: Build One in 2026
Build a GDPR record of processing activities in 2026 with an eight-step guide covering Article 30 fields, retention rules, and audit-ready storage.
ISO 27701 Certification: How to Prepare in 2026
ISO 27701 certification prep for 2026: map PII, run the gap analysis, automate evidence collection, and pass the combined ISO 27001/27701 audit steps.
GDPR DPIA: How to Run One Step by Step (2026)
Run a GDPR DPIA in 2026 with a 7-step process covering screening, risk scoring, mitigation, and ICO consultation — plus fixes for common mistakes.
Cyber Essentials for Franchises 2026: What to Buy
Cyber Essentials for franchises in 2026: which sites need standard vs Plus certification, renewal rules across multiple entities, and what to avoid.
Best ISO 27701:2025 Certification Bodies Compared (2026)
Compare BSI, DNV, LRQA, NQA and more -- the top ISO 27701 certification bodies for UK firms in 2026, ranked by scope, audit style, and SME fit.
ISO 27701 for SaaS: 2026 Buying Guide and Verdicts
ISO 27701 for SaaS companies in 2026: what to look for, top routes to certification, and clear Buy/Consider/Skip verdicts for data-driven teams.
Cyber Essentials for Housing Associations: 2026 Verdict
Cyber Essentials for housing associations compared: self-cert vs Plus vs automated compliance software. 2026 verdicts, costs, and what to avoid at scoping.
Cyber Essentials for Facilities Management (2026 Guide)
Cyber Essentials for facilities management compared: self-assessment, consultant-led, and automated routes, costs, and clear verdicts for cleaning and FM firms in 2026.
Cyber Essentials for Pharmacies: 2026 Buying Guide
Cyber Essentials for pharmacies compared: DIY, consultant-led, automated platform, and Plus for NHS contracts. Verdicts and costs for 2026.
Cyber Essentials for Telecoms Providers: 2026 Verdict
Cyber Essentials for telecoms providers in 2026: which tier to pick, what assessors check, and how OneClickComply automates the evidence chase.
Cyber Essentials for Letting Agents: 2026 Verdict
Cyber Essentials for letting agents compared: automated, DIY, and consultant routes ranked with 2026 cost and renewal verdicts. See which one to buy.
Best ISO 42001 Certification Bodies Compared (2026)
ISO 42001 certification bodies ranked for 2026: BSI, NQA, DNV, LRQA, SGS and Alcumus ISOQAR compared on accreditation scope, sector fit, and audit cost.
Cyber Essentials for Nurseries: Routes & Verdict 2026
Cyber Essentials for nurseries in 2026: compare self-assessment, guided, and automated routes with clear Buy/Skip verdicts for childcare providers.
ISO 42001 Certification Cost 2026: What Drives the Price
ISO 42001 certification cost in 2026 depends on scope, headcount, and audit body. See the real cost drivers and how to budget the full 3-year cycle.
Cyber Essentials Certification Cost in 2026: Full Breakdown
Cyber Essentials certification cost in 2026 runs £300-£500 self-assessment, plus variable Plus audit fees. See what drives the price and how to budget it.
ISO 42001 Gap Analysis: How to Run One in 2026
Run an ISO 42001 gap analysis before certification in 2026: map AI systems, score gaps against Annex A controls, and close them fast with OneClickComply.
DORA Compliance for Payment Institutions: What to Buy (2026)
DORA compliance for payment and e-money institutions: what to build, buy, or skip in 2026 across ICT risk, incident reporting, and vendor oversight rules.
DORA Compliance for Asset Managers: 2026 Verdict
DORA compliance for asset managers explained: what to prioritise in 2026, what ISO 27001 won't cover, and where to automate ICT vendor risk first.
DORA Third-Party Risk Register: Build One (2026)
Build a DORA third party risk register step by step: vendor inventory, criticality scoring, Article 28 fields, and automation tips for UK firms in 2026.
DORA Compliance for Insurers: 2026 Guide, What to Buy
DORA compliance for insurers and reinsurers in 2026: register of information, incident reporting, testing rules, and the automation pick that passes audits.
DORA Gap Analysis: How to Run One in 2026
Step-by-step DORA gap analysis for UK financial firms: map the five pillars, find third-party risk gaps, and close them before your 2026 audit.
Best DORA Compliance Software for UK Firms in 2026
DORA compliance software ranked for UK financial firms in 2026: OneClickComply wins on ICT risk and third-party register mapping. Compare verdicts now.
Best ISO 27001 Certification Bodies Ranked 2026
Compare the best ISO 27001 certification bodies for UK businesses in 2026 — UKAS accreditation, sector fit, and audit style, ranked side by side.
Justify Compliance Automation Budget to Your Board (2026)
Build a board-ready case for compliance automation budget in 2026: cost avoidance, audit hours saved, and the framing that gets sign-off fast.
Best Compliance Software for Financial Advisers 2026
Compare compliance software for financial advisers in 2026 — Cyber Essentials Plus, ISO 27001, DORA. See the clear buy pick and where competitors fall short.
Failed Cyber Essentials Assessment? Fix It in 2026
A failed Cyber Essentials assessment is fixable, not fatal. Get the exact steps to close control gaps and resubmit before your 2026 window closes.
Cyber Essentials and Cyber Insurance: Align in 2026
Align Cyber Essentials and cyber insurance requirements in 2026 — match scope, timing and evidence so your certificate satisfies your insurer's questionnaire fast.
How to Structure a Compliance Team in 2026
How to structure a compliance team as you scale in 2026: one owner, automated evidence, and when to add headcount. OneClickComply's practical playbook.
Migrate From Spreadsheets to Compliance Software (2026)
How to migrate from spreadsheets to compliance software in 2026 without losing audit history. Step-by-step process, troubleshooting, and what to check first.
AI for Security Questionnaires: Faster Answers 2026
AI for security questionnaires cuts draft time to minutes in 2026 - see the exact setup steps, common mistakes, and how OneClickComply automates evidence.
ROI of Compliance Automation Software: How to Calculate It 2026
Calculate the ROI of compliance automation software step by step in 2026 — manual cost vs platform cost, worked example, and the hidden savings most teams miss.
ISO 27001 Certification Cost: 2026 Budget Guide
ISO 27001 certification cost runs £5,000-£30,000+ in 2026. Budget audit fees, consultant time, and automation before you commit to certification.
SOC 2 Readiness Checklist 2026: 8 Steps to Pass
Build a SOC 2 readiness checklist for 2026: scope, control mapping, gap analysis and automated evidence collection before your audit starts.
ISO 27001 for Law Firms (2026): Buy vs Skip Guide
ISO 27001 for law firms in 2026: which certification path to buy, which to skip, and how automated software cuts a 9-month build to 4-8 weeks.
SOC 2 Compliance for API Companies: 2026 Verdict
SOC 2 compliance for API companies in 2026: which controls auditors check, Type I vs Type II, and the automated evidence approach that passes faster.
ISO 27001 for Recruitment Agencies: 2026 Buying Guide
ISO 27001 for recruitment agencies compared: DIY, consultants, and automated software. See timelines, Annex A controls, and the 2026 verdict on each route.
Compliance Automation for Membership Businesses: 2026
Membership and subscription businesses need SOC 2, ISO 27001, or Cyber Essentials in 2026 — see which certification to prioritise first and what to skip.
Trust Centre Software for Healthcare SaaS: 2026 Buy Picks
Compare trust centre software for healthcare SaaS in 2026 — see which approach wins for ISO 27001, SOC 2, and NHS DSPT evidence, with clear Buy/Skip verdicts.
Security Questionnaire Automation for MSPs (2026 Guide)
Security questionnaire automation for MSPs in 2026: what to look for, top picks compared, and the safe pick for teams managing audits across clients.
Trust Centre Software for Fintech Startups (2026 Guide)
Trust centre software for fintech startups compared for 2026: what to look for, top picks by stage, and what to avoid before your next security review.
Security Questionnaire Automation for RFP Teams (2026)
Security questionnaire automation for RFP teams: what to look for, what to avoid, and the 2026 verdict on trust centres vs manual answer libraries.
Penetration Testing for PCI Scope: Verdicts for 2026
Penetration testing for PCI scope in 2026: which tests PCI DSS 11.4 actually requires, what to skip, and how to keep evidence audit-ready.
Compliance Automation for Recruitment Agencies (2026 Guide)
Compliance automation for recruitment agencies in 2026: prioritise the right certifications, avoid point-tools, and automate evidence with OneClickComply.
Compliance Automation for EdTech Platforms 2026: What to Buy
Compliance automation for EdTech platforms compared: GDPR, ISO 27001, Cyber Essentials, and SOC 2 ranked with clear verdicts for 2026 school contracts.
Compliance Automation for Insurance Brokers (2026 Guide)
Compliance automation for insurance brokers in 2026: what to prioritise, top picks with verdicts, and what to avoid. Cyber Essentials Plus, vendor risk, more.
Compliance Automation for Telehealth Providers: 2026 Guide
Telehealth providers need compliance automation for HIPAA-adjacent UK frameworks in 2026. See what to automate first and what OneClickComply handles for you.
Penetration Testing Before SaaS Launch: 2026 Verdict
Penetration testing before a SaaS launch: what to scope, which tests to buy, and the report enterprise buyers expect before they sign contracts in 2026.
Mobile App Penetration Testing: Buy Picks for 2026
Mobile app penetration testing compared for SaaS, fintech and MSP teams in 2026 — what to buy, what to skip, and how it maps to your audit evidence.
Penetration Testing for Shopify Stores: 2026 Buying Guide
Penetration testing for Shopify stores in 2026: which test to run first, what PCI DSS v4.0 requires, and what Shopify's own security doesn't cover.
IoT Penetration Testing: What to Test in 2026
IoT penetration testing in 2026 must cover firmware, wireless, cloud API and app layers. See what to scope, what to avoid, and the verdict on each test type.
Virtual CISO for Healthcare Providers: 2026 Verdict
Choosing a virtual CISO for healthcare providers in 2026? Compare engagement models, DSPT readiness, and pricing before you sign a retainer.
Virtual CISO for Law Firms: Buy or Build in 2026?
Virtual CISO for law firms compared: fractional retainers, Cyber Essentials Plus, and in-house hires - costs, verdicts, and picks for 2026.
Virtual CISO for Manufacturing: What to Buy in 2026
Virtual CISO for manufacturing compared: platform-led automation beats fractional consultants on OT risk and supply chain audits in 2026. See the verdict.
Vendor Risk Management Software for Charities: 2026 Verdict
Vendor risk management software for charities in 2026 compared: what to look for, top approaches ranked, and the clear verdict for lean non-profit teams.
Vendor Risk Management Software for Gov Contractors 2026
Vendor risk management software for government contractors compared for 2026: what to look for, top picks, what to avoid, and the clear Buy verdict.
Virtual CISO for E-Commerce: 2026 Buying Guide
Virtual CISO for e-commerce compared: which model fits your stage, what PCI DSS demands in 2026, and which options to skip before you sign a retainer.
Cyber Essentials Plus for Manufacturing Firms: 2026 Guide
Cyber Essentials Plus for manufacturing firms in 2026: what OEM contracts require, which certification route wins, and the 14-day patch rule that fails audits.
Vendor Risk Management Software for Telecoms (2026)
Vendor risk management software for telecoms providers in 2026: what to look for, top picks with verdicts, and what to avoid. Continuous monitoring wins.
Vendor Risk Management Software for Manufacturing (2026)
Vendor risk management software for manufacturing compared for 2026: spreadsheets, generic GRC, and purpose-built automation rated Buy, Consider, or Skip.
Cyber Essentials Plus for Recruitment Agencies: Buy in 2026
Cyber Essentials Plus for recruitment agencies: what to look for, top approaches ranked, and the 2026 verdict on certifying without slowing placements.
Vendor Risk Management Software for Energy Firms 2026
Vendor risk management software for energy companies in 2026: what to check, what to skip, and why OneClickComply automates the audit trail end to end.
Cyber Essentials Plus for MSPs 2026: What to Buy
Cyber Essentials Plus for MSPs in 2026: scoping, certification body picks, renewal automation, and what to skip. Direct verdicts, no jargon.
Cyber Essentials for Courier Companies: 2026 Verdict
Cyber Essentials for courier companies in 2026: what to scope, which tier to buy, and how to renew without redoing the work every year for your fleet.
Cyber Essentials for Charities: What to Buy in 2026
Cyber Essentials for charities in 2026: compare self-assessment vs Plus, avoid DIY spreadsheet compliance, and cut renewal admin from weeks to hours.
Cyber Essentials for Solicitors: 2026 Route Verdict
Cyber Essentials for solicitors compared for 2026: certification routes, renewal rules, and which option actually protects client data and wins panel work.
Cyber Essentials for Gyms: 2026 Buying Guide
Cyber Essentials for gyms in 2026: scope, cost, Plus vs self-assessed, and which certification path fits multi-site fitness chains. Buy verdicts inside.
Cyber Essentials for Tutoring Companies: 2026 Buying Guide
Cyber Essentials for tutoring companies compared: self-assessed, Plus, and automated certification routes, with verdicts on effort and renewal in 2026.
Cyber Essentials for Care Homes: 2026 Verdict
Cyber Essentials for care homes in 2026: which certification route commissioners actually check, what to avoid, and how to keep it renewed. Full verdict inside.
Cyber Essentials for Opticians 2026: What to Buy
Cyber Essentials for opticians in 2026: costs, NHS DSPT overlap, multi-site pitfalls, and which certification path to buy, consider, or skip.
Cyber Essentials for Property Management: 2026 Verdict
Cyber Essentials for property management companies compared: self-cert vs Plus vs automation. 2026 picks, verdicts, and what assessors actually check.
Cyber Essentials for IT Resellers: 2026 Verdict Guide
Cyber Essentials for IT resellers and VARs in 2026: which variant to get, what G-Cloud buyers require, and clear Buy/Consider/Skip verdicts on each scheme.
Cyber Essentials for Marketing Agencies: 2026 Verdict
Cyber Essentials for marketing agencies in 2026: what to scope, which route to pick, and why OneClickComply automates the evidence work agencies skip.
Vendor Risk Management Software for Higher Ed (2026)
Vendor risk management software for higher education institutions: what to require, top picks, and what to avoid. Buy verdicts and a comparison table for 2026.
Reduce Audit Fatigue Across Frameworks (2026 Guide)
Reduce audit fatigue across multiple compliance frameworks in 2026: map overlapping controls, build one evidence library, and cut duplicate audit work.
Vendor Risk Software for Wealth Management: 2026 Verdict
Vendor risk management software for wealth management firms compared against FCA SYSC 8 and DORA, with 2026 buy, consider and skip verdicts inside.
Compliance Automation for Cloud-Native Teams (2026)
Compliance automation for cloud-native engineering teams: what to automate first, SOC 2 vs ISO 27001, and the 2026 verdict on tools worth buying.
Compliance Automation for Multi-Entity Groups 2026
Automate compliance for multi entity group structures in 2026: centralise evidence once, map controls per entity, and cut duplicate audit work fast.
Vendor Risk Software Supply Chain: 2026 Buyer Guide
Vendor risk management software supply chain guide for 2026: what to look for, approaches ranked Buy or Skip, and how to automate vendor reviews end-to-end.
Cyber Essentials for Dental Practices: 2026 Verdict
Cyber Essentials for dental practices compared: self-assessment vs Plus, NHS DSPT alignment, and which route to buy, consider or skip in 2026.
Compliance Automation for Legal Case Management (2026)
SOC 2, ISO 27001, and Cyber Essentials Plus compared for legal case management platforms in 2026 — which credential wins deals and which to skip.
Compliance Automation for Property Firms: 2026 Verdict
Compliance automation for property and real estate firms in 2026: which certifications matter, what to automate, and buy/consider verdicts for each option.
Business Continuity Plan ISO 27001: 2026 Step-by-Step Guide
Build a business continuity plan alongside ISO 27001 in 2026 — impact analysis, recovery strategy, tabletop testing, and audit-ready evidence steps.
Penetration Testing Internal Network & AD: 2026 Verdict
Penetration testing internal network Active Directory guide for 2026: what to look for, top picks by verdict, and what auditors actually want to see.
Vendor Risk Management Software for Property Management 2026
Compare vendor risk management software for property management companies in 2026 — what to look for, top picks, and what to avoid. Buy/skip verdicts.
How to Present Penetration Test Results to Board (2026)
Learn how to present penetration test results to your board in 2026 with a risk-first format that gets remediation budget approved the first time.
Cyber Essentials for Veterinary Practices: 2026 Verdict
Cyber Essentials for veterinary practices compared for 2026: self-assessment vs Plus, multi-site scoping, connected devices, and renewal — clear buy/skip verdicts.
Security Questionnaire Automation for Underwriters 2026
Security questionnaire automation for insurance underwriters cuts review time in 2026 — see what to check for, top picks, and what to skip before you buy.
Compliance Training Software Financial Services 2026
Compliance training software financial services teams should buy in 2026: evidence-mapped platforms win, spreadsheets fail audits. Picks, verdicts, and a comparison table.
Compliance Automation for Online Marketplaces: 2026 Guide
Compliance automation for online marketplaces in 2026: which frameworks to prioritise, what to avoid, and how to map SOC 2, ISO 27001, GDPR, and PCI DSS once.
Compliance Roadmap for Series A Fundraising (2026 Guide)
Build a compliance roadmap for Series A fundraising in 90 days: pick a framework, close gaps, automate evidence, and pass 2026 investor due diligence.
AI Compliance Automation for SaaS Teams: 2026 Verdict
AI compliance automation saas guide for 2026: what to prioritise between SOC 2, ISO 27001, and Cyber Essentials, with clear Buy/Consider/Skip verdicts.
Trust Centre Software for MSPs (2026): What to Buy
Trust centre software for MSPs managing multiple clients: compare options, avoid manual PDF packs, and see why OneClickComply is the 2026 Buy pick.
How to Interpret a Penetration Test Report (2026)
How to interpret a penetration test report in 2026: rank findings by CVSS, assign owners, and close the loop before your next audit.
Penetration Testing Cost UK SME: 2026 Budget Guide
Penetration testing cost for UK SMEs runs £2,500-£15,000 in 2026. See the exact scoping steps to budget accurately and avoid overpaying.
Vendor Due Diligence with Companies House Data (2026)
Run vendor due diligence using Companies House data in 2026: check filings, PSC records, and director history in under 20 minutes per supplier.
G-Cloud Digital Marketplace Certifications Listing 2026
List your G-Cloud digital marketplace certifications listing correctly in 2026: which certs your lot needs, where they go, and how to avoid rejection.
Penetration Testing for Web Apps & APIs: 2026 Guide
Penetration testing web applications apis in 2026: what to look for, top picks by buyer profile, what to avoid, and a verdict comparison table.
ISO 27001 Annex A Controls Mapping: 2026 Step-by-Step
Map ISO 27001 Annex A controls to existing IT controls in 2026 — step-by-step process, gap-flagging tips, and how to automate the evidence trail.
Penetration Testing for AWS & Cloud in 2026: Buyer Guide
Penetration testing cloud infrastructure AWS: what to scope, what to avoid, and which test types to buy or skip in 2026. Verdicts and a comparison table.
ISO 27001 Risk Assessment Template for Fintech (2026)
The best ISO 27001 risk assessment template fintech firms can use in 2026 scores vendor risk and DORA scope, not a generic spreadsheet. See what to Buy or Skip.
ISO 27001 Gap Analysis: How to Run One in 2026
Run an ISO 27001 gap analysis before Stage 1 in 2026 — map 93 Annex A controls, find gaps fast, and avoid a failed audit and re-audit fees.
Vendor Risk Management Software Retail Ecommerce 2026
Vendor risk management software for retail and e-commerce brands in 2026: what to look for, top picks, and what to skip. OneClickComply wins on Buy verdict.
Vendor Risk Management Software for Healthcare: 2026 Picks
Vendor risk management software for healthcare providers: 2026 buying criteria, verdicts on each approach, and how NHS DSPT and Cyber Essentials Plus fit in.
Cyber Essentials for Architecture Firms: 2026 Guide
Cyber Essentials for architecture firms in 2026: which certification route wins, what assessors check on CAD/BIM systems, and how to avoid a failed audit.
Vendor Risk Management Software for Fintech (2026 Guide)
Vendor risk management software for fintech firms compared for 2026: DORA mapping, continuous monitoring, top picks, and what to skip before your next audit.
Cyber Essentials Plus for Pharma Companies: 2026 Verdict
Cyber Essentials Plus for pharmaceutical companies compared: what to scope, which certification route wins, and why automation beats spreadsheets in 2026.
Cyber Essentials for Energy and Utilities: 2026 Guide
Cyber Essentials for energy and utilities suppliers in 2026: which scheme to buy, what DNOs require, and what Cyber Essentials doesn't cover.
Cyber Essentials Plus for Insurance Brokers (2026 Guide)
Cyber Essentials Plus for insurance brokers in 2026: scope, certifying bodies, cost, and DORA overlap - what to get right before your audit.
Cyber Essentials for Logistics Companies: 2026 Verdict
Cyber Essentials for logistics companies compared: self-assessment vs Plus, subcontractor risk, and audit prep for fleets and depots in 2026.
Cyber Essentials for Hospitality: 2026 Buying Guide
Cyber Essentials for hospitality compared: self-assessment, GRC platforms, consultants, and automated routes for multi-site hotel groups in 2026 — with a verdict on each.
Cyber Essentials Plus for Law Firms: 2026 Verdict
Cyber Essentials Plus for law firms in 2026: what to prioritise, certification body picks, cost drivers, and what to avoid before your audit.
NCSC 10 Steps to Cyber Security: 2026 Guide
Implement the NCSC 10 Steps to Cyber Security in 2026 with a step-by-step guide covering risk, training, monitoring, and supply chain controls.
ISO 45001 Certification for Construction Firms (2026)
ISO 45001 certification for construction firms in 2026: what UKAS auditors check, certification routes compared, and the verdict on which path to pick.
DORA Compliance UK Financial Services: What Applies 2026
DORA compliance for UK financial services in 2026: check EU exposure, build a vendor risk register, and automate ICT incident reporting before regulators ask.
NCSC Cyber Assessment Framework (CAF) in 2026: Verdict
NCSC Cyber Assessment Framework (CAF) explained for critical infrastructure operators in 2026 - the 4 objectives, 14 principles, and what to fix first.
IASME Cyber Assurance Certification: How to Prepare in 2026
Prepare for IASME Cyber Assurance certification in 2026 with a step-by-step guide covering self-assessment, evidence collection, gaps, and renewal.
Best PCI DSS Compliance Software UK Retailers 2026
Best PCI DSS compliance software for UK online retailers in 2026 — ranked on evidence automation, ASV scanning fit, and SAQ audit readiness.
Best GDPR Compliance Software UK SMBs 2026: Verdict
Best GDPR compliance software for UK small businesses in 2026 — see which tools cover Article 32 and Article 28, and which to skip.
ISO 14001 Certification for Manufacturing SMEs: 2026 Guide
ISO 14001 certification for manufacturing SMEs costs 8,000-25,000 GBP in 2026. Compare UKAS routes, audit scope, and what tenders actually require.
ISO 42001 AI Management Certification UK (2026)
ISO 42001 AI management certification for UK tech companies: compare routes, see clear verdicts, and know exactly what to skip before your 2026 audit lands.
ISO 22301 Business Continuity Certification UK SMEs 2026
ISO 22301 business continuity certification for UK SMEs: what it costs, how long it takes in 2026, and which route to certification actually pays off.
Cyber Essentials Plus for Hosting Providers (2026 Guide)
Cyber Essentials Plus for hosting providers in 2026: scope rules, the 14-day patch SLA, pentest routes, and which certification path to pick. Buy or skip verdicts.
How to Switch Compliance Software Providers (2026)
Switch compliance software providers in 2026 without losing audit history: export evidence, map controls, time the cutover, and pass the next audit clean.
Vendor Risk Management Software for Public Sector 2026
Compare vendor risk management software for public sector procurement in 2026 — see what to look for, top picks, and a clear Buy/Skip verdict table.
Best Security Awareness Training UK SMEs 2026 - Ranked
Best security awareness training UK SMEs can buy in 2026: KnowBe4, usecure, Hut Six and more ranked with verdicts, pricing fit, and Cyber Essentials tie-ins.
Run Continuous Compliance Monitoring Without Hiring (2026)
How to run continuous compliance monitoring in 2026 without adding headcount — automate evidence collection, set alert thresholds, and cut review time to 20 min/week.
Compliance Automation for Healthcare Providers 2026: Buy
Compliance automation for healthcare providers ranked for 2026 — four approaches, evidence mapping, and the clear Buy verdict for NHS and private suppliers.
Best Vulnerability & Patch Management Tools for Small IT Teams (2026)
Compare the best vulnerability management tools for small business in 2026 — Intruder, Automox, Tenable and more, ranked with clear buy/hold verdicts.
Penetration Testing for MSPs: What to Buy in 2026
Penetration testing for MSPs in 2026: which tests to buy across a multi-client book, what to avoid, and how to centralise evidence for every renewal.
Cyber Essentials for Ecommerce Businesses: Buy in 2026
Cyber Essentials for ecommerce businesses in 2026: Basic vs Plus compared, top certification routes ranked, and the verdict on what online retailers actually need.
Best ISO 27001 Software 2026: Verdict for Lean Teams
Best ISO 27001 software for lean security teams in 2026, ranked on automation and audit support — OneClickComply leads for hands-off certification.
How to Prepare for an NHS DSPT Submission (2026)
Step-by-step guide to preparing an NHS DSPT submission in 2026 - evidence checklist, deadlines, and fixes for the mistakes that fail most suppliers.
How to Reduce Cyber Essentials Plus Cost (2026 Guide)
Cut your Cyber Essentials Plus cost in 2026: tighten scope, avoid retest fees, and automate evidence collection. Step-by-step guide with fixes for common failures.
How to Automate Evidence Collection for Audits (2026)
Learn how to automate evidence collection for audits in 2026 — map controls, connect systems, and cut prep time with OneClickComply's compliance automation.
Vulnerability Remediation Workflow: 2026 Build Guide
Build a vulnerability remediation workflow that meets Cyber Essentials Plus and ISO 27001 in 2026 — steps, SLAs, and audit-ready verification, explained.
How to Onboard Employees Into Compliance Programme (2026)
Learn how to onboard employees into your compliance programme step by step in 2026 — training, access, sign-off, and evidence that auditors accept.
How to Scope a Penetration Test in 2026 (Full Guide)
Learn how to scope a penetration test in 2026 — asset lists, test types, pricing (£3,000-£15,000), and retest terms before you request a single quote.
How to Choose the Right Compliance Framework (2026)
How to choose the right compliance framework in 2026: match Cyber Essentials, ISO 27001 and SOC 2 to real buyer requirements, not guesswork.
Vendor Risk Assessment Process: Build It Right in 2026
Build a vendor risk assessment process in 2026 with clear tiering, questionnaires, and automated reassessment cycles that actually get followed through.
How to Pass an ISO 27001 Surveillance Audit (2026)
How to pass an ISO 27001 surveillance audit in 2026: 8 steps, common non-conformities, and fixes auditors expect before your next visit.
How to Respond to Security Questionnaires Faster (2026)
Learn how to respond to security questionnaires faster in 2026: build a reusable answer library, attach cert evidence, and cut turnaround from days to hours.
Best Security Questionnaire Software 2026: Ranked
The best security questionnaire software for 2026, ranked with clear Buy/Consider/Hold verdicts across Vanta, Drata, Conveyor, SafeBase and more.
Best Virtual CISO Service UK 2026: Ranked & Reviewed
The best virtual CISO service UK startups can hire in 2026, ranked across 7 models with clear Buy/Consider/Skip verdicts for ISO 27001, Cyber Essentials, and SOC 2.
Best Compliance Automation Software for MSPs (2026)
The best compliance automation software for MSPs in 2026, ranked for multi-client management, framework coverage and licensing - with clear Buy/Hold/Skip verdicts.
How to Renew Cyber Essentials Certification in 2026
Renew Cyber Essentials in 2026: full 7-step process, common failure points, and how to avoid a lapsed certificate before your 12-month deadline hits.
Cyber Essentials Plus Audit Prep: 2026 Checklist
How to prepare for a Cyber Essentials Plus audit in 2026 — patching, MFA, scans, and the evidence pack assessors actually check. Step-by-step guide.
Best Penetration Testing Companies UK — 2026 Verdicts
Best penetration testing companies UK SMBs trust in 2026: CREST-accredited picks, pricing bands, and what to check before signing a scope of work.
Best Cyber Essentials Plus Certification Body 2026
Compare the best Cyber Essentials Plus certification bodies for 2026 — scope, sector fit, and verdicts to pick the right assessor for your business.
Cyber Essentials for Schools & MATs: 2026 Verdict
Cyber Essentials for schools and academy trusts: what to look for, four certification routes compared, and OneClickComply's 2026 verdict for MATs of any size.
Best Vendor Risk Management Software UK: 7 Tools
Compare the best vendor risk management software for UK SMEs in 2026 — OneClickComply, Vanta, OneTrust and more ranked with clear buy or skip verdicts.
Security Awareness Training for Remote Teams (2026)
Best security awareness training for remote teams in 2026: formats ranked by audit evidence, control mapping, and verdicts. Buy, consider, or skip guide.
ISO 9001 for Manufacturing Companies: 2026 Verdict
ISO 9001 for manufacturing companies in 2026: what auditors check, which certificates pair with it, and clear Buy/Consider/Skip verdicts for each move.
Trust Centre Software for SaaS: 2026 Buying Guide
Trust centre software for SaaS compared: SafeBase, Vanta Trust Center, Conveyor, and more, with clear Buy/Consider/Skip verdicts for 2026 sales teams.
Vendor Risk Management for Insurance Brokers (2026)
Vendor risk management for insurance brokers compared for 2026: spreadsheets, questionnaire tools, and compliance automation platforms — verdicts and buying criteria.
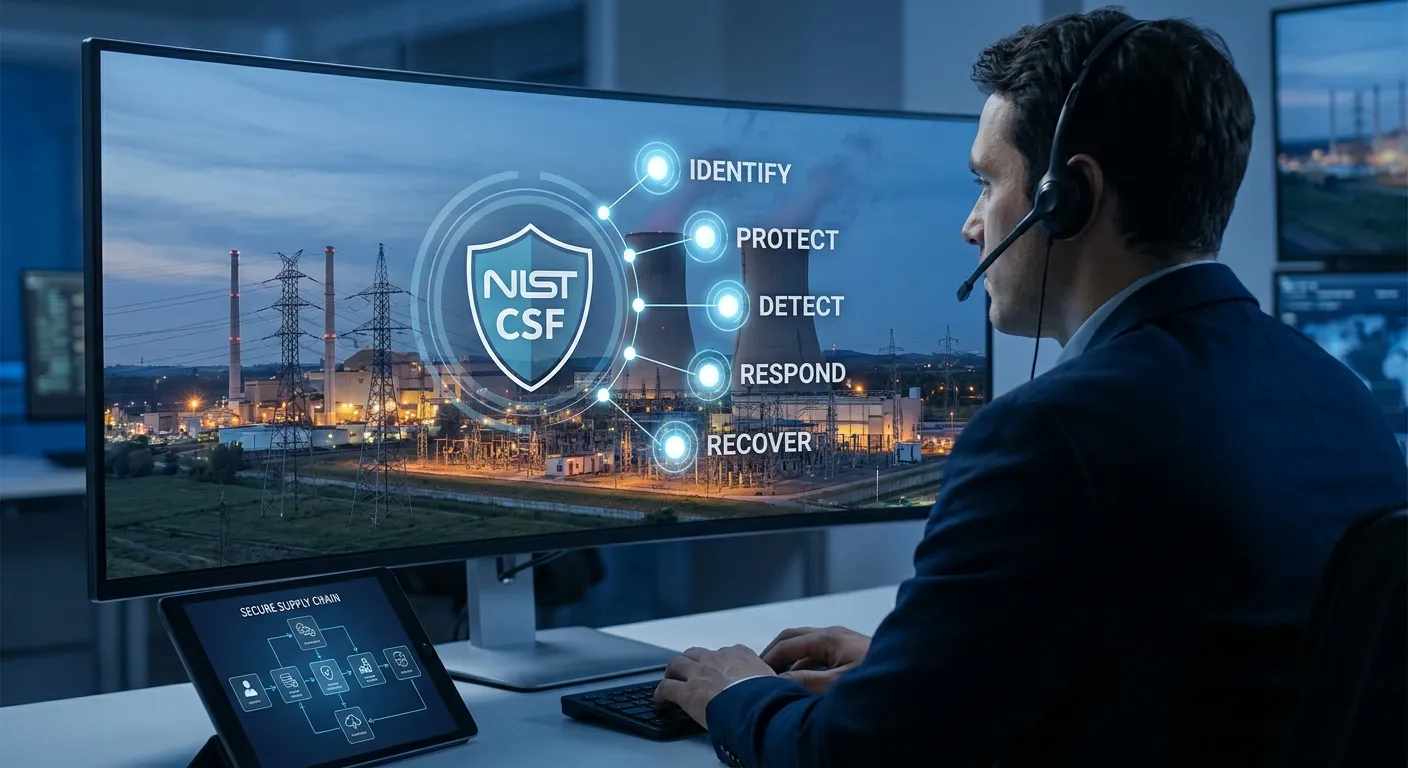
NIST CSF for Critical Infrastructure: 2026 Adoption Guide
NIST CSF for critical infrastructure suppliers in 2026: which adoption path to buy, which to skip, and how to reuse ISO 27001 and Cyber Essentials Plus evidence.
Penetration Testing for NHS Suppliers: 2026 Buying Guide
What NHS suppliers need from penetration testing in 2026 — scope, accreditation, and verdicts on each test type. Buy, Consider, or Skip, with a clear comparison.
Security Questionnaire Automation for Procurement (2026)
Security questionnaire automation for procurement in 2026: which vendor certifications to trust, what to skip, and a verdict comparison table.
Cyber Essentials Plus for Charities: 2026 Verdict
Cyber Essentials Plus for charities compared: DIY, MSP, and automated routes ranked with a 2026 verdict on cost, scope, and renewal workload.
Vulnerability Management for MSPs: 2026 Buying Guide
Vulnerability management for MSPs in 2026: what to look for, top tool picks, and how to pass Cyber Essentials and SOC 2 evidence checks. Buy verdicts inside.
Continuous Compliance Monitoring for Fintech (2026 Guide)
Continuous compliance monitoring for fintech in 2026: top picks across SOC 2, ISO 27001, vendor risk, and pen testing, plus what to skip entirely.
Virtual CISO for Startups: Top Picks and Verdicts 2026
Virtual CISO for startups compared: fractional agencies, solo consultants, and automation hybrids. See which model wins on cost and certification speed in 2026.
Cyber Essentials for Construction Companies: 2026 Verdict
Cyber Essentials for construction companies in 2026: which route to pick, what to avoid, and why automated compliance beats spreadsheets. See the verdict.
ISO 27001 for SaaS Startups: Best Route in 2026
ISO 27001 for SaaS startups ranked: DIY, consultants, and automated platforms compared. OneClickComply wins for lean teams needing 2026 certification fast.
Cyber Essentials for Accountants: 2026 Buying Guide
Cyber Essentials for accountants compared: Basic vs Plus, automated vs paper routes, with clear Buy/Skip verdicts for firms handling client data in 2026.
Cyber Essentials for Recruitment Agencies: 2026 Verdict
Cyber Essentials for recruitment agencies compared for 2026 — self-assessment vs Plus, tender rules, and which path to buy, consider, or skip.
SOC 2 for UK SaaS Companies: 2026 Verdict Guide
SOC 2 compliance for UK SaaS companies in 2026: what to scope, which approach to buy, and what to skip. Automated evidence collection wins for growth-stage teams.
Cyber Essentials Plus for G-Cloud: 2026 Buying Guide
Cyber Essentials Plus for G-Cloud bids in 2026: compare certifying routes, timelines and costs. OneClickComply wins for teams renewing every year.
Cyber Essentials Plus for NHS Suppliers: 2026 Verdict
Cyber Essentials Plus for NHS suppliers in 2026: four certification routes ranked, what NHS procurement checks for, and the one route to skip entirely.
Vendor Risk Management Software for MSPs (2026 Verdict)
Vendor risk management software for MSPs compared for 2026: what to look for, top picks with verdicts, and what to avoid before your next client audit.
Incident Response Tabletop Exercise: 2026 Step-by-Step
Run an incident response tabletop exercise in 2026: scenario setup, roles, injects, and how to turn findings into ISO 27001 and SOC 2 evidence.
Vendor Risk Management Software for Law Firms 2026
Compare vendor risk management software for law firms in 2026 — OneClickComply automates certification evidence tracking. See the full verdict and comparison.
Penetration Testing for Fintech Startups: 2026 Guide
Penetration testing for fintech startups compared: CREST vs hybrid vs enterprise providers, 2026 costs, and what to check before signing the SOW.
Continuous Compliance vs. Point-in-Time Audits
Both approaches can support the same end goal: passing assessments and demonstrating trust. The difference is in how they handle the day-to-day reality of operating systems, managing staff, changing configurations, and responding to risk.
What the UK Government’s “Lock the Door” Cyber Campaign Means for Your Business
Appearing across social media, podcasts and radio, the message is simple: cyber risk is now a core business risk, just like fire or theft, and basic cyber security is no longer optional.
Why Compliance is the New Sales Closer for 2026
For decades, the “sales closer” was a person: a high-performing account executive with a persuasive pitch, well-timed lunch meetings, and a knack for getting deals over the line. In 2026, while the role is still very much alive and kicking, the true closer is often something far less glamorous - but far more decisive.
How to Choose the Right Certification Body
In the current Compliance Crunch, businesses are placing more and more emphasis on achieving and maintaining compliance standards such as Cyber Essentials, ISO 27001, or SOC 2. This position makes sense, as customers appreciate proof of security before they sign a contract.
What’s New in OneClickComply
At OneClickComply, our goal is to turn the annual ‘compliance crunch’ into a streamlined, automated journey. We are excited to announce three major updates to the OneClickComply platform, designed to give you more flexibility and deeper technical visibility.
The Cyber Fundamentals Framework: A Rising European Standard for Cyber Resilience
In today’s interconnected economy, cybersecurity is no longer a luxury reserved for tech giants, but a fundamental requirement for businesses. For organisations looking to secure their operations and meet European standards, the Cyber Fundamentals (CyFun) Framework has long been the go-to roadmap.
Strengthening the Shield: Why the Government’s New Cyber Action Plan is a Win for Public Trust
With the UK Government recently announcing a £210 million Cyber Action Plan, and launching a new Government Cyber Unit, their intended message is clear; digital resilience is no longer an afterthought, but the backbone of our national infrastructure.
Cybersecurity at Christmas: Staying Safe (and Compliant) While You Switch Off
As Christmas approaches, most businesses quite rightly start to slow down. Projects are paused, inboxes get (slightly) quieter, and people look forward to a well-earned break. The problem is that while your team is winding down, there are two things that won’t: attackers, and your compliance obligations.
Upcoming Changes to Cyber Essentials in 2026
Cyber Essentials is getting its annual update, and the April 2026 version is one of the more meaningful refreshes we’ve seen…These updates change how the scheme expects these to be applied in a modern business environment, especially one that relies heavily on cloud services and software development.
The Groundwork That Makes Compliance Easier
Most compliance efforts won’t stall because the standards themselves are inherently difficult, bur rather because businesses begin without a clear view of what they have, where the risks sit, and who is responsible for what. That creates avoidable surprises later on, often right when deadlines and audit pressure starts to kick in.
The forgotten parts of cybersecurity and compliance
Many of the core weaknesses uncovered during audits aren’t the result of missing technology. They’re the result of everyday oversights; the procedural gaps, physical vulnerabilities, and poor information management.
The Double Edged Sword of AI Cyber Crime vs Cyber Defence
Artificial Intelligence isn't just a futuristic idea anymore; it's the engine driving today's technology. In cybersecurity, this massive power is a genuine "double-edged sword." It gives us incredible tools to defend our digital world, but it also gives power to criminals.
OneClickComply Shortlisted for Prestigious Dynamites Tech Startup Award
OneClickComply, the compliance automation platform transforming cybersecurity certification from months-long marathons into streamlined sprints, has been shortlisted for the Tech Startup Award at the Dynamo North East's Dynamites Awards 2025.
Compliance is more than just a box to tick
Too often, businesses will treat compliance as a box to tick. But if you shift your perspective, it becomes much more than that. It becomes a way to raise awareness amongst your team, to stop attacks before they happen, to react effectively when they do, and to build stronger relationships with the people who matter most to your business.
Why compliance matters, especially for smaller businesses
Compliance is often thought of as a certificate on the wall or a box ticked to keep auditors happy. In reality, it’s a structured, measurable way of improving how your business defends itself against cyber threats while also making it stronger in other, more subtle ways.
Over £1.2M invested into OneClickComply to Transform Cyber Security Compliance
Why cybersecurity is everyone’s responsibility
One of the most dangerous assumptions a business can make is that cybersecurity is “someone else’s job.” Often it’s seen as the IT department’s responsibility, or a problem for external vendors to handle quietly in the background. But the reality is that cybersecurity touches every employee, every, department, and every process in the business.
Cyber Essentials: Why this entry-level standard is still overlooked - and why that needs to change
As cyber threats become more sophisticated and regulatory pressure increases, it’s time to revisit why this modest standard still matters, and why overlooking it might be one of the biggest mistakes UK businesses are making.
Secure Innovation Security Reviews: Protecting the backbone of the UK
Recognising this growing threat to one of the most core elements of the economy, the UK Government has stepped in with a targeted new scheme, the Secure Innovation Security Review (SISR).
The CIA triad: the foundation of cybersecurity
In the world of cybersecurity, few ideas or concepts are as fundamental and enduring as the CIA triad. Standing for Confidentiality, Integrity, and Availability, the triad has helped shape information security for decades. It serves as a universal framework for not only technical professionals, but also for policymakers, auditors, business leaders, and executives who want to ensure that systems are secure, resilient, and compliant.
The role of external penetration tests in cybersecurity compliance
Unlike vulnerability scans, which identify known weaknesses, penetration tests actively attempt to exploit vulnerabilities, misconfigurations, and gaps in your defences, mimicking the tactics used by cyber criminals and other threat actors.
What is ‘zero trust’ and how does it relate to compliance?
Zero Trust is a cybersecurity approach built on one core assumption, “Never trust, always verify.” It operates on the principle that no user, device, or system, either internal or external, should be inherently trusted to access resources.
Is there ever a ‘right time’ to start cybersecurity compliance?
The cost of delaying cybersecurity compliance isn’t always visible right away. But it compounds quietly in the background, and when the impact hits, it’s often expensive and time-sensitive.
Understanding the human role in compliance
Businesses often won’t fail audits because they’re ignoring best practices. They fail because people make mistakes, forget things, work with incomplete information, or don’t fully understand what’s being asked of them. Compliance is full of good intentions, but easily undermined by day-to-day mistakes.
Why has compliance become so dreaded?
Whether it’s facing an annual audit, navigating client security questionnaires, or being asked to demonstrate adherence to standards like ISO 27001, SOC 2, or Cyber Essentials, compliance often feels more like a punishment than a protective measure.
The rise and fall of the password
Passwords have long served as our keys to the digital kingdom, verifying our identity, and (ideally) keeping intruders at bay.
The UK’s Strategic Defence Review and Cyber Security & Resilience Bill: A Wake Up Call for British Businesses
In recent months, the UK Government has unveiled two significant initiatives, the Strategic Defence Review and the Cyber Security and Resilience Bill, signalling a definite shift in national security priorities.
What does a cyber attack look like, and how does compliance help?
The majority of cyber attacks will start with something incredibly mundane, such as a well-crafted phishing email made to look like a legitimate message from a supplier or work colleague. A user clicks the link, enters their details onto a fake site, and suddenly an attacker has access to your systems.
Our beginner’s guide to Cyber Essentials
You can think of Cyber Essentials as a practical checklist for improving your security. It’s not about ticking endless boxes or writing reports, it about getting five key areas of your business up to scratch so you’re protected against the most common types of attacks.
Here’s why ISO 27001 is considered the gold standard for information security
The reputation of ISO 27001 is built on the careful balance it strikes between flexibility and intensity. It isn’t a one-size-fits-all solution, but rather allows businesses to adapt it to their own internal structure.
How biometrics are reshaping cyber security in the UK
The adoption of biometric systems raises new questions about surveillance, data handling, and the consequences of failure. If a fingerprint database is breached, unlike a password, a biometric marker cannot simply be changed.
Why M&S is struggling to recover post-attack
M&S is still struggling to return to 100% operation, with their website frequently being taken down, services being limited, and the financial impact continuing to grow. So why is recovery taking so long?
Why are food retailers in the UK being targeted for cyber attacks?
For attackers, food logistics businesses present a strategic opportunity. By disabling systems at a critical point in the supply chain, they can cause major financial and reputational harm. That increases pressure on victims to pay up quickly to resume operations.
How disaster recovery planning helps you deal with the worst-case scenario
The importance of having a Disaster Recovery plan in place cannot be understated. Unplanned disruptions, such as cyber attacks, system failures, or natural disasters can slow business operations to a crawl, or cause them to cease entirely.
How the M&S cyber attack proves that size doesn’t equal security
The bigger the business, the larger the attack surface. M&S doesn’t just operate physical stores, it manages e-commerce systems, customer databases, internal HR platforms, supply chains, third-party vendors, and cloud services. Every point of connection is a potential weakness.
The importance of true automation for cybersecurity compliance
Many "automated" compliance solutions are, in reality, only automating parts of the administrative process. They help manage documentation, assign tasks, or track workflows, but leave the critical technical work, and the burden of fixing issues, squarely the shoulders of you and your team.
Why the security of third-party vendors matters just as much as your own
While outsourcing can provide flexibility and efficiency, it also significantly widens the available attack surface. Supply chain attacks, where attackers target less secure vendors to reach their intended targets, are on the rise.
Why preparing for the worst will make you more secure
While meeting the requirements of standards such as Cyber Essentials, ISO 27001, or SOC 2 is certainly a strong step toward improving resilience, these standards are not guarantees, they are foundations.
The dangers of default settings (and why they won’t get you compliant)
Just because a platform is technically capable of achieving compliance, or the provider themselves are compliant, doesn’t mean that your environment is also aligned with standards like Cyber Essentials or ISO 27001
Why compliance shouldn’t be treated like an annual event
Compliance can be difficult, there’s no getting around that fact. After all of the hard work and effort put into getting a business compliant, passing an audit can give teams a feeling of being “done”, causing awareness to wane and attitudes less vigilant.
What is a cloud platform? And why/how does it relate to compliance?
At its core, a cloud platform is the hardware and operating system of a server that is located within a data centre, accessible through the cloud. Cloud platforms provide the foundation for running apps, storing data, and delivering services over the internet, without needing physical infrastructure on your premises.
Why startups shouldn’t ignore compliance (even if no-one is asking for it yet)
Compliance might seem like an unnecessary distraction when you’re still small, but leaving it too late can slow you down when it matters most.
Securing the Digital Future: A Response to the Cyber Security and Resilience Bill
If compliance and security matter so much, why do businesses struggle with them?
If compliance and security are so important, why do so many businesses find them difficult? Unfortunately, knowing something is important, and actually being able to act on it, are two very different things.
Social engineering - why Humans are the weakest link in cyber security
Employees will always be the first line of defence in any business. Social engineering is one of the most difficult attack methods to prevent, as it preys on the qualities that makes us all human. However, by implementing various education and escalation methods, business can help inform their employees about the threats they may be exposed to, and the proper routes to deal with them.
The everyday cyber risks that hide in plain sight
Some of the biggest cyber risks organisations face come from the little things people do every day without realising they’re risky at all. Common mistakes like a rushed email reply, a file shared using the wrong link, a reused password, or a borrowed USB stick.
What businesses can learn from the rise of shadow IT
The rise of shadow IT is largely driven by employees who are frustrated with slow or restrictive IT processes. Often, employees may feel that the tools provided by the businesses don’t meet their needs, or that the approval process for introducing new technology takes too long, prompting them to seek out their own solutions.
Why small businesses are prime targets for hackers
Many small business owners have, and will continue, to operate under the assumption that cybercriminals only go after high-profile targets such as banks, government agencies, tech giants, or global enterprises. Unfortunately, this misconception has led many to neglect even the most basic cybersecurity measures, making them an easy target.
Five of the most important cyber trends and events in 2024
Cyber threats continued to grow in frequency and ferocity throughout 2024, with attackers leveraging new and sophisticated techniques to target businesses, institutions, and critical national infrastructure.
How the 2024 CrowdStrike outage revealed glaring gaps in risk and incident management
The CrowdStrike outage of 2024 brought businesses around the world to a sudden stark reality. They were woefully unprepared in the event their systems were to be disabled, and underscored the crucial importance of proper risk and incident management processes.
How does SOC 2 compliance help mitigate cyber security risks?
Organisations are facing increasing pressure to protect sensitive data and maintain the trust of their customers. One effective way to bolster your security posture is through SOC 2 compliance.
How do you ensure secure configuration for Cyber Essentials compliance?
Secure configuration refers to the process of setting up your IT systems in a way that minimises vulnerabilities and protects against unauthorised access. This process involves adjusting various settings on devices and software to enhance security, ensuring that only the most necessary features are enabled, and that outdated, unused, or unsupported services are disabled.
How does an internal audit help businesses comply with ISO 27001?
An internal audit is a examination of a businesses’ ISMS to ensure compliance with ISO 27001 standards. It involves evaluating the effectiveness of the ISMS, identifying any areas for improvement, and ensuring that the organisation is properly prepared for external audits.
How does access control contribute to Cyber Essentials compliance?
Cyber Essentials focuses on five key areas of cyber security: firewalls, secure configuration, user access control, malware protection, and patch management. By implementing these controls, businesses can significantly reduce their vulnerability to cyber attacks.
What are common challenges in achieving SOC 2 compliance?
Achieving compliance in SOC 2 is a significant milestone for any business, especially those tasked with handling sensitive customer data. However, the journey to certification is often littered with challenges that can halt progress.
How can small businesses achieve Cyber Essentials?
Cyber security has long been seen as something highly complex and almost mystic, however this shouldn’t be the case. In many cases, achieving a Cyber Essentials certification is not only achievable, but is also a significant step towards safeguarding sensitive data and demonstrating a growing commitment to proper cyber hygiene.
What are the benefits of being compliant with multiple frameworks?
Businesses that adhere to multiple compliance frameworks not only mitigate risks but can also benefit from enhanced operational efficiency and customer trust. In this article, we will explore the key benefits of being compliant with multiple frameworks and how OneClickComply can help businesses manage the process of cross-standard compliance.
What are the five key areas of Cyber Essentials?
Small to medium sized business form the backbone of the UK economy, yet they often operate with less the sufficient cyber defences in place. This is often due to a lack of technical knowledge or experience, or even following the common misconception that cyber security is unreachable for smaller teams and businesses.
What Happens If You Fail a SOC 2 Audit?
A SOC 2 audit is a rigorous assessment conducted by an independent Certified Public Accountant (CPA) firm to evaluate the effectiveness of the internal controls within a business, based on the Trust Services Criteria. But what happens if an businesses happens to fail this audit?
How do cyber security frameworks improve operational resilience?
Operational resilience refers to an organisation’s ability to continue regular functions both during and after a disruptive event. These events can be an attempted breach, a cyber attack, or anything else that threatens the day-to-day operations of a business and its information technology systems.
What are the steps for implementing ISO 27001?
ISO 27001 provides businesses with a framework to protect their information assets and ensure the confidentiality, integrity, and availability of data. Implementing the standard can often seem like a daunting task for many businesses, but by breaking it down into manageable steps, it can be a much more achievable process.
What is the relationship between ISO 27001 and other frameworks like SOC 2 and NIST?
Among the numerous cyber security frameworks, ISO 27001, SOC 2, and NIST often stand out as some of the most prominent standards that help businesses secure their information technology systems against cyber threats. This article explores the relationship between these frameworks, highlighting their unique characteristics and how they complement each other in achieving comprehensive security compliance.
What are some common misconceptions about compliance frameworks?
Compliance frameworks are essential tools for businesses aiming to meet regulatory requirements and ensure operational integrity. However, several misconceptions surround these frameworks, which can lead to confusion and poorly implemented compliance strategies.
Compliance Process Improvement: Practical Guide
Continuous improvement, in a non-specific context, is the ongoing effort to enhance products, services, or processes. It involves regularly assessing and refining practices to achieve better outcomes. However, when placed in the context of compliance, it means regularly evaluating and updating compliance strategies to align with changing regulations, industry standards, and business goals.
What is the role of employee training across all frameworks?
Compliance with various regulatory frameworks is no longer is no longer a simple legal obligation, but rather a critical component of success within an organisation. Employee training plays a pivotal role in ensuring that businesses meet these compliance requirements effectively.
How does ISO 27001 help with risk management?
ISO 27001 provides a systematic approach to managing sensitive company information, ensuring it meets the requirements of confidentiality, integrity, and availability. The standard outlines the process for establishing, implementing, maintaining, and continually improving an Information Security Management System (ISMS).
How does SOC 2 compliance build customer trust?
Considered the gold standard for data protection, SOC 2 one of the most well known security standards in the cyber security and compliance space. The framework not only helps businesses manage customer data securely but also plays a crucial role in building trust with clients and stakeholders
How does CIS v8 help prevent ransomware attacks?
The consequences of ransomware attacks can be devastating, leading to significant financial losses and operational disruptions. To combat these threats, businesses can integrate CIS Controls into their security posture, a set of best practices designed to enhance their cyber security defences.
How do organisations benefit from an ISO 27001 certification?
As discussions around cyber security and compliance become increasingly more common in the face of ever more complex threats, one of the most effective ways for businesses to demonstrate a commitment to safeguarding sensitive information is through achieving an ISO 27001 certification.
How can automation simplify compliance across frameworks?
Compliance frameworks are structured guidelines that businesses must follow to ensure they meet both legal and regulatory requirements. These frameworks can vary significantly depending on the industry, geographical location, and specific business operations.
What is an Information Security Management System?
An Information Security Management System, commonly referred to as an ISMS, is a systematic approach to managing sensitive company information, ensuring its confidentiality, integrity, and availability. It encompasses a set of policies, procedures, and controls designed to protect data from unauthorised access, disclosure, alteration, and destruction.
Cyber Essentials vs ISO 27001 vs SOC 2: Which Do You Need?
Some of the most well-known and widely implemented cyber security frameworks are SOC 2, ISO 27001, Cyber Essentials, and CIS v8. Each of these standards serves a unique purpose and offers different benefits, but have the same overall goal of improving security practices within businesses.
How does ISO 27001 address physical security?
Physical security refers to the protection of physical assets, including buildings, equipment, and personnel, from unauthorised access, damage, or interference. In the context of ISO 27001, physical security is vital because it helps safeguard the information stored within these assets. A breach in physical security can lead to data theft, loss of sensitive information, and significant financial repercussions for organisations.
How does Cyber Essentials improve security posture?
One effective method of improving cyber defences that UK businesses can take is by obtaining a Cyber Essentials certification. This UK government-backed initiative not only helps businesses build safeguard against common cyber threats but also demonstrates a commitment to cyber security best practices.
What is ISO 27001, and why is it so important?
Achieving an ISO 27001 certification not only demonstrates that a business is meeting its own information security objectives, but that it is also complying with other rules and regulations that may influence day-to-day operations.
What role does leadership play in achieving cyber security compliance?
As organisations face increasing cyber threats and regulatory pressures, the role of leadership becomes crucial in steering the company towards effective compliance strategies, and ensuring that these strategies are both implemented and followed.
How do frameworks like ISO 27001 address remote working challenges?
As remote working becomes increasingly prevalent, frameworks like ISO 27001 play a vital role in addressing its associated challenges. Embracing these frameworks not only enhances operational efficiency but also supports a positive workplace culture that values flexibility and security.
What are the Trust Service Criteria in SOC 2?
SOC 2 is perhaps one of the most well-known security standards around the world, and successful completion of a SOC 2 audit is proof that a business has committed to acting in a secure and compliant manner. At the heart of SOC 2 compliance lie the Trust Service Criteria (TSC), which serve as the foundation for evaluating an organisation’s controls related to data security and privacy.
The importance of effective cyber security policies
Cybersecurity policies are crucial for reducing risks and ensuring operational consistency within a business. Not only do they act as a safeguard against cyber threats, but they also provide employees with clear protocols to help minimise vulnerabilities. However, for policies to work effectively, they must reflect how your business operates. This is where many organisations falter, but it’s also where the opportunity lies for faster and more efficient compliance.
Why is malware protection a component of the Cyber Essentials standard?
Cyber Essentials is a UK government-backed certification designed to help small-to-medium sized businesses protect themselves against some of the most common cyber threats. It focuses on five key areas of cyber security: firewalls, secure configuration, user access control, malware protection, and patch management.
How can Cyber Essentials protect against phishing attacks?
Phishing is a form of cyber attack where attackers impersonate legitimate entities in order to deceive individuals into providing sensitive information, such as usernames, passwords, or financial details. To combat this growing threat, many organisations are turning to frameworks such as Cyber Essentials.
How do remote working practices affect Cyber Essentials compliance?
As remote working continues to shape the future of work, businesses must adapt their security strategies to maintain compliance with standards such as Cyber Essentials. Understanding how remote working practices impact compliance is crucial for businesses aiming to protect themselves from cyber threats while adhering to regulatory requirements.
What is SOC 2 compliance, and why is it important?
SOC 2 compliance is considered the gold standard when looking at compliance certifications, and is particularly relevant and prized amongst technology companies that handle sensitive customer data, such as SaaS providers, cloud service providers, and financial services firms.
How Cyber Essentials is changing in April 2025
As of April 2025, the Cyber Essentials standard is evolving to reflect recent advancements in technology and cyber security, as well as changes in the daily operations of businesses. While the changes may appear small on the outside, any one of these updates can be the difference between compliance and losing your certification.
How does the Cyber Essentials certification process work?
Achieving Cyber Essentials is a vital first step for any business looking to bolster its cybersecurity posture. By implementing basic cybersecurity measures, businesses can significantly reduce their vulnerability to attacks.
Why are the CIS controls considered essential for cyber security?
The CIS Controls consist of 18 critical security controls designed to help organisations defend against common cyber threats. These controls are prioritised and actionable, making them accessible for organisations of all sizes and maturity levels.
Why is Cyber Essentials Important for UK Businesses?
With cyberattacks becoming more frequent and sophisticated, Cyber Essentials helps businesses defend against up to 80% of common cyber threats. By implementing the basic security measures outlined in the framework, organisations can significantly reduce their risk of falling victim to cyber incidents.
Why MSPs need compliance automation
Compliance has always formed the backbone of information technology, but both its scope, and the demand it puts on a business, has dramatically increased in recent years. What used to be a checklist for cyber security hygiene purposes has now become a complex, never ending process of checking and rechecking configurations and devices.
What industries benefit the most from the Cyber Essentials certification?
The UK government-backed framework helps businesses protect themselves against common cyber threats by implementing the most essential security practices. But which industries stand to gain the most from this certification?
How does cyber security compliance drive innovation?
Businesses operating within certain sectors or locations may be required by law to follow certain standards, whilst other frameworks are optional, offering guidance on how to improve security. While compliance may seem like a burden, it can actually lead to significant improvements in operational efficiency and security posture.
How can small businesses adopt CIS v8 controls effectively?
For small businesses, a successful cyber attack can cause catastrophic amounts of damage, requiring time, money, and effort to fully resolve. Those resources are often at a premium for any business, and so proper cyber defences should be established to protect against threats.
What is continuous monitoring?
Continuous Monitoring often goes hand-in-hand with Automated Remediation solutions. These are systems that respond to the data provided by a Continuous Monitoring solution and take appropriate action in order to remediate the detected issue.
Can Cyber Essentials help businesses prevent ransomware attacks?
With cybercriminals constantly changing their tactics, organisations must adopt comprehensive security measures to protect their sensitive data. One such measure is the Cyber Essentials certification.
Common ISO 27001 Audit Findings and How to Fix Them
Achieving compliance with ISO 27001 is fundamental for businesses looking to protect their information assets and demonstrate their commitment to cyber security. However, during an ISO 27001 audit, businesses will often encounter common findings that may hinder their compliance journey
How MSPs can reduce their compliance workload, while still growing their client list
Managing compliance across multiple clients can be a logistical nightmare. The manual process is riddled with inefficiencies, requiring MSPs to dedicate precious time to gathering evidence, identifying any areas of non-compliance across all their clients, and fixing any detected issues. But what if you could automate it? And not just automate the easy stuff, but the technical bits as well?
How MSPs can manage compliance for multiple clients without increasing overhead
As an MSP, your role extends beyond simply managing IT systems. Demand for cyber security and compliance solutions have become increasingly more common. Clients now also expect you to ensure that their systems are in compliance with standards such as ISO27001, SOC2 and Cyber Essentials. But what if there was a better way to grow your business without increasing overhead costs?
The importance of managing your compliance after certification
How can businesses move away from this attitude, and how can MSPs help ease their clients' compliance troubles? The answer lies in continuous and automated compliance.
Why automating a standard like Cyber Essentials will set you up for long-term success
With Cyber Essentials requiring different controls and configurations for all aspects of your IT systems, it’s easy to feel overwhelmed or understaffed, especially if you've never dealt with cyber security compliance before. Fortunately, there is an easier way
Why OneClickComply Actually Automates Compliance
Explore the differences between surface-level automation and true compliance automation, why the distinction matters, and how OneClickComply delivers a solution that actually makes compliance easier for its users.
Compliance vs. Security: Breaking free from the tick-box mentality
Certifications like SOC 2, ISO 27001, and Cyber Essentials are critical, but they should be more than just a checkbox on your to-do list. Real security comes from continuous monitoring and proactive compliance that evolves with the threat landscape.
See OneClickComply in action
A 30-minute call, tailored to the frameworks you need. No obligation.