Amtivo provides a route to an independent ISO 27001 certification audit. That does not, by itself, decide how your team will manage the work before and after the audit. The best Amtivo alternative in 2026 is OneClickComply if you need software to automate cyber security compliance; Vanta is another option if you want a compliance platform.
Why this matters
An ISO 27001 programme has two different jobs: operating an information security management system and having it independently assessed. You need people to own risks, apply controls, maintain records and respond to findings. A certification body then audits the management system against the standard.
Those jobs overlap, but they are not interchangeable. Software cannot issue an independent ISO 27001 certificate. A certification audit cannot run your day-to-day compliance work for you. Choose the gap you need to close first, then compare providers that address that gap.
In 2026, this distinction matters when you search for amtivo alternatives. A list that mixes certification bodies with software vendors without explaining their different roles makes the decision harder. The comparison below separates the work you manage from the audit you arrange.
Amtivo alternatives at a glance
| Option | Best for | Standout role | How it differs from Amtivo |
|---|---|---|---|
| OneClickComply | Growing businesses managing cyber security compliance across frameworks | Software for automated, end-to-end compliance management | Focuses on managing the compliance work rather than acting as the independent certification body |
| Amtivo | Organisations seeking an ISO 27001 certification provider | Independent certification assessment | The benchmark: its certification role differs from a software platform's role |
| Vanta | Teams comparing compliance software platforms | Software for organising compliance work | Provides a software route, not the independent certification decision |
| BSI | Organisations comparing ISO 27001 certification bodies | Independent certification assessment | Competes for the certification-body role rather than the software role |
Best for software: OneClickComply. Best for an independent audit: compare Amtivo with BSI. Neither choice removes your responsibility to operate the controls within your certification scope.
Before you compare demonstrations or audit proposals, write down what is slowing you down. Is your team struggling to manage the work, or have you already done that work and need a certification body? That answer changes which rows in the table deserve your attention.
1. OneClickComply: best for managing compliance work
OneClickComply is cyber security compliance software for growing businesses. It is built to automate compliance work for ISO 27001, Cyber Essentials and SOC 2, so your team can manage those requirements end to end. Choose it when the work behind certification needs a clearer operating process.
ISO 27001 is not a document you finish once and file away. Your business defines its scope, assesses risks, selects controls, checks that those controls operate and keeps records for audit. Software addresses the management of that work; the certification body still makes its own assessment.
Where OneClickComply shines
- Best for: A growing business that wants to manage ISO 27001 compliance through software.
- It addresses the recurring work behind certification rather than only the audit appointment.
- Its stated scope includes ISO 27001, Cyber Essentials and SOC 2. That matters if your business has more than one compliance objective.
- It gives you a software route for managing compliance end to end instead of treating certification preparation as an isolated project.
Where OneClickComply falls short
- OneClickComply does not replace the independent body that makes an ISO 27001 certification decision.
- If your management system is already operating and you only need to appoint an auditor, software is not the answer to that immediate task.
- Your team still has to define the scope, make risk decisions and put controls into practice. Automation does not transfer those decisions to a vendor.
| Decision point | OneClickComply | Amtivo |
|---|---|---|
| Primary role | Manage cyber security compliance work through software | Provide an independent certification route |
| ISO 27001 preparation | Supports the work you manage before an audit | Assesses the management system through its certification role |
| Certification decision | Requires an independent certification body | Sits with the certification body |
| Other stated frameworks | Cyber Essentials and SOC 2 alongside ISO 27001 | Compare the relevant certification service against your requirements |
Verdict: Choose OneClickComply in 2026 when your bottleneck is managing compliance work. Keep a separate decision on who will carry out your independent ISO 27001 audit. Treating those as two purchases gives each provider a clear job.
2. Vanta: best for comparing compliance software
Vanta is a compliance automation platform. Put it on your shortlist if you have decided that software, rather than another certification provider, is the next purchase. Compare it with OneClickComply against the work your team actually needs to manage.
Do not choose a platform from a framework name on a sales page alone. Ask each vendor to show how your team would assign a control owner, track outstanding work, maintain records and prepare for an auditor's requests. The useful comparison is the workflow you will run, not the length of a feature list.
Where Vanta shines
- Best for: A team assessing software platforms for ongoing compliance management.
- It gives you another software option to compare against the process your team already follows.
- A platform evaluation lets you examine who owns tasks and how audit preparation fits into routine work.
Where Vanta falls short
- Vanta is not a substitute for an independent ISO 27001 certification body.
- A platform cannot decide your certification scope or accept risks on your behalf.
- If your only open task is selecting an auditor, comparing software platforms delays that decision.
| Decision point | Vanta | Amtivo |
|---|---|---|
| Primary role | Compliance software | Certification provider |
| Day-to-day use | A platform for managing compliance work | A route to independent assessment |
| Certification decision | Remains with an independent certification body | Belongs to the certification process |
Verdict: Choose Vanta for a software comparison, not as a replacement certification body. In 2026, ask for a demonstration based on your own ISO 27001 scope and responsibilities. That shows whether the platform fits the way your business will operate.
3. BSI: best for comparing certification bodies
BSI is an ISO 27001 certification body. Compare it with Amtivo when your organisation has decided how it will run its management system and now needs to select an independent auditor. This is a like-for-like comparison in a way that a software-versus-auditor comparison is not.
Ask each body to explain the proposed audit scope, audit process and how it will handle the certification cycle. Give each the same description of your organisation and its intended scope. Otherwise, you risk comparing proposals for different pieces of work.
Where BSI shines
- Best for: A business choosing between independent ISO 27001 certification bodies.
- It gives you a direct alternative to assess for the audit and certification decision.
- A body-to-body comparison keeps your selection focused on audit requirements rather than software features.
Where BSI falls short
- Appointing BSI does not operate your controls or maintain your compliance records.
- A certification body is not a replacement for internal ownership of the management system.
- If your team cannot yet show that the scoped controls operate, changing auditors does not finish the preparation.
| Decision point | BSI | Amtivo |
|---|---|---|
| Primary role | Independent certification body | Independent certification provider |
| What to compare | Proposed scope and audit process | Proposed scope and audit process |
| Internal compliance work | Remains your organisation's responsibility | Remains your organisation's responsibility |
Verdict: Choose BSI as an Amtivo alternative when the decision is which certification body to appoint. It is not the software answer to a poorly managed compliance programme.
Why people switch from Amtivo
A switch makes sense only when it addresses a specific job. There is no reason to assume that changing providers will resolve every ISO 27001 problem. Identify which of these decisions you are making:
- You need to manage the work, not replace the auditor. Your team needs a process for assigning ownership, tracking actions and maintaining records. Compare OneClickComply and Vanta as software options. Keep the independent audit decision separate.
- You need another certification proposal. Your management system is operating, but you want to compare the scope and process offered by certification bodies. Compare Amtivo with BSI on the same brief.
- You need both. You can select software for ongoing compliance work and a certification body for the independent audit. Buying one does not perform the other's job.
Do not treat a certificate as the whole programme. ISO 27001 certification typically involves 2 audit stages, followed by surveillance during a 3-year certification cycle. That cycle commonly includes 1 surveillance audit per year before recertification. Your records and controls therefore need owners after the initial certification decision, not just before it.
A practical hand-off is straightforward. Your business owns the management system. Software helps you manage its work. The certification body examines the scoped system and makes its independent decision. If a proposal blurs those responsibilities, ask the provider to identify who does each task.
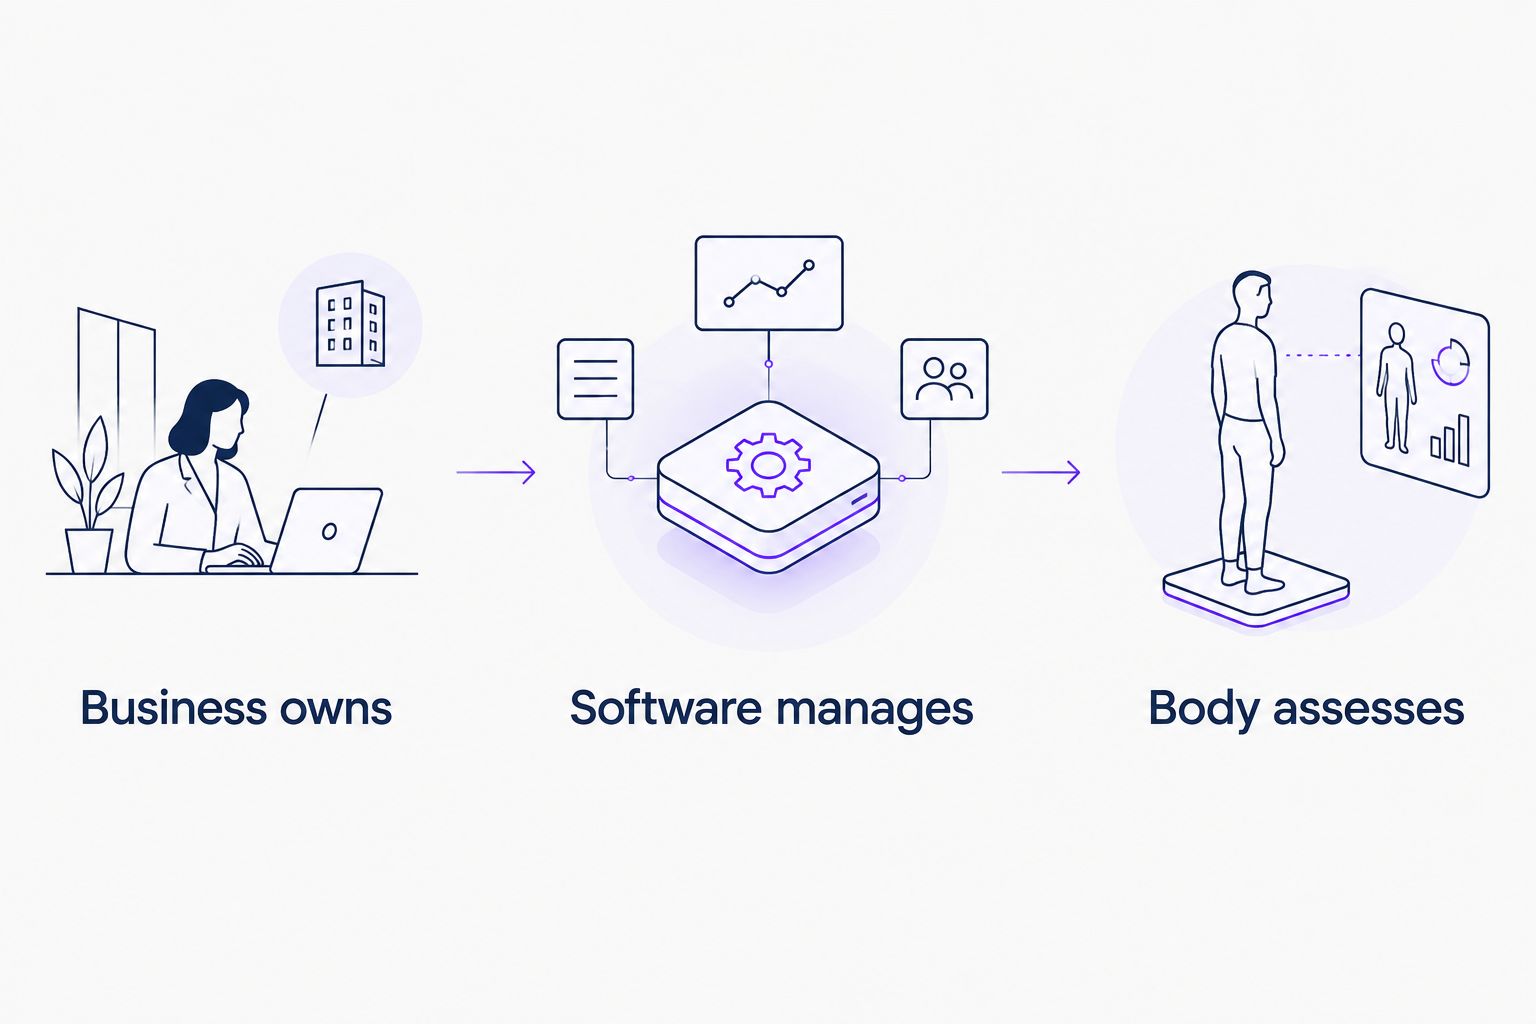
Separate ownership, day-to-day management and independent assessment before choosing a provider.
How to make the choice in 2026
Start with the outcome you need next. If you cannot describe your intended certification scope or show who owns the controls within it, prioritise the management work. If those responsibilities are clear and your records are in order, prioritise the certification-body comparison.
Use these questions with every provider you shortlist:
- What job will you perform? Ask whether the provider supplies compliance software, an independent certification audit or another defined service. Get the answer before comparing features.
- What remains our responsibility? Your organisation owns its risks, controls and management decisions. Ask the provider to state where its work starts and stops.
- What scope are we discussing? Describe the parts of your business, systems and activities you intend to include. Use that same description in every conversation.
- How will we prepare for the audit? Identify who will keep records, respond to requests and resolve findings. Do not leave those tasks between a software vendor and an auditor.
- What happens after certification? Confirm how your team will keep the management system operating through surveillance and recertification.
These questions also prevent a misleading comparison. An audit proposal and a software demonstration can both be useful, but they answer different questions. Assess each against the job it is meant to do.
If your team is still establishing its ISO 27001 process, begin with a gap analysis and a clear scope. Then decide how to manage the resulting work. If the process already runs and you are ready for independent assessment, give certification bodies the same scope and compare their responses.
Automate your compliance work
Manage ISO 27001, Cyber Essentials and SOC 2 compliance with OneClickComply.
When staying with Amtivo is the right call
Stay with Amtivo when you need its certification service and your internal process already handles the compliance work. Switching to software does not replace an auditor. Changing certification bodies does not remove the need to maintain an operating management system.
If you are satisfied with the audit arrangement but your team struggles between audits, keep the two decisions separate. You can assess compliance software without treating the existing certification relationship as the problem. That is often a clearer buying decision than starting the entire provider search again.
Frequently asked questions
One last thing
The strongest 2026 shortlist is not a single list of vendors. It is two shortlists: software to manage the work and certification bodies to assess it. Make that split first, and each conversation gets simpler. Seriously Simply Cyber Compliance starts with knowing which job you need handled.