Best overall: OneClickComply. Best for startups running SOC 2 alongside ISO 27001: Vanta. Best for engineering-heavy teams: Drata. Best for broad framework coverage: Secureframe. Best for lean teams with no dedicated compliance hire: Sprinto. Best for startups managing several frameworks at once: Scrut.
Why this matters
Enterprise buyers now ask for ISO 27001 before they'll sign a contract, and in 2026 procurement teams treat it as a checkbox rather than a negotiation point. Startups that try to run the certification off spreadsheets burn weeks chasing screenshots and policy sign-offs instead of shipping product.
Software built for this cuts that overhead. OneClickComply automates evidence collection and policy management so a two-person security function can carry ISO 27001 the same way a ten-person compliance team would.
The six platforms below get judged on what actually slows startups down in 2026: setup time, evidence automation, audit support, and how much manual chasing survives after go-live.
What makes the best ISO 27001 software for startups
Startups don't need every feature a 200-person compliance team wants. They need the handful that remove manual work fast, and they need it to still hold up when the company doubles headcount.
- Automated evidence collection — pulls proof from cloud, HR and device tools instead of manual screenshots
- Annex A control mapping — maps existing policies and tech controls to ISO 27001:2022's 93 controls without a spreadsheet
- Continuous monitoring — flags control drift between audits, not just at renewal time
- Auditor collaboration — gives your certification body direct, read-only access to evidence instead of email threads
- Time to audit-ready state — how fast a founder-led team reaches a certification-ready position
- Framework reuse — lets the same evidence back SOC 2, Cyber Essentials or ISO 42001 later without starting over
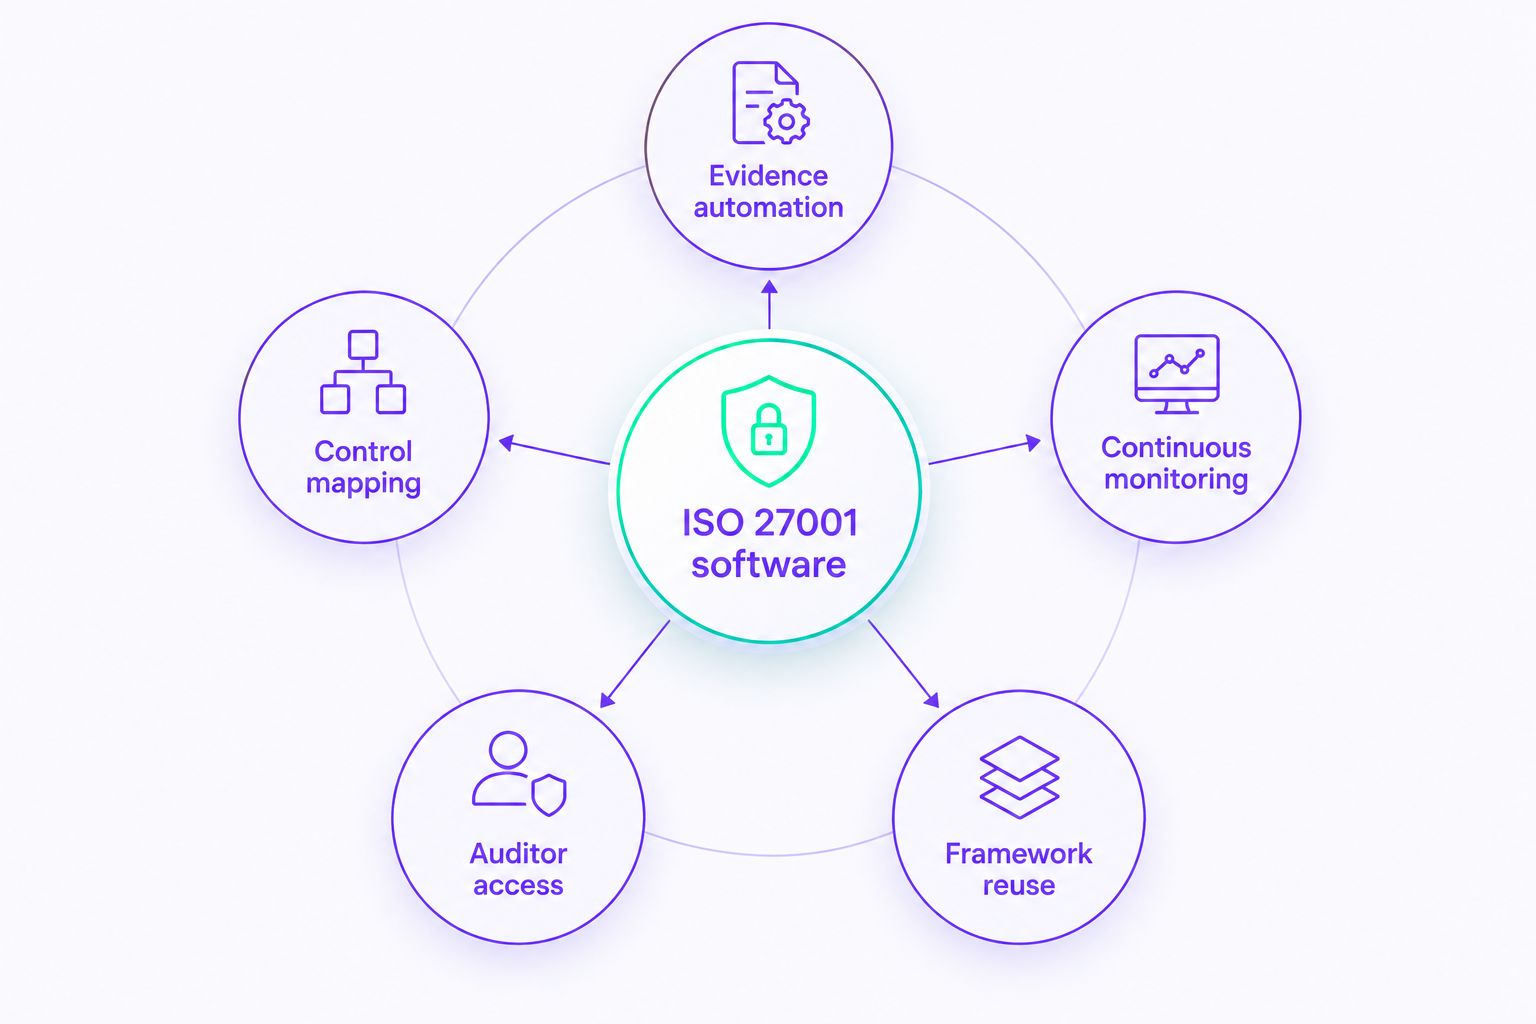
Evidence automation is the criterion that saves the most founder hours.
ISO 27001 software for startups: at a glance
| Software | Best for | Standout feature | Key limitation |
|---|---|---|---|
| OneClickComply | Startups automating evidence end-to-end | Continuous evidence collection tied to policy management | Smaller third-party integration marketplace than legacy GRC players |
| Vanta | Startups running SOC 2 in parallel | Combined SOC 2 + ISO 27001 control library | Framework depth beyond the two headline certifications is thinner |
| Drata | Engineering-heavy startups | Deep API and cloud infrastructure integrations | Steeper setup for teams without an engineer driving configuration |
| Secureframe | Startups needing broad framework coverage | Wide library covering ISO, SOC 2, HIPAA, PCI DSS | Breadth trades off against ISO 27001-specific depth |
| Sprinto | Lean teams with no compliance hire | Guided implementation with built-in checks | Less flexible for startups with custom or unusual control sets |
| Scrut | Startups managing multi-framework risk | Centralised risk register across every framework | Risk register depth adds complexity smaller teams may not need |
1. OneClickComply: best ISO 27001 software for startups automating evidence end-to-end
OneClickComply automates evidence collection, policy management and Annex A control mapping for ISO 27001, Cyber Essentials and SOC 2 in one workspace. It connects to the cloud and HR tools you already run and keeps evidence current instead of collecting it once a year right before the audit.
OneClickComply pros:
- Handles evidence collection, policy drafting and control mapping in one place
- Built for lean teams — no dedicated compliance hire required to run it day-to-day
- Framework reuse means ISO 27001 evidence carries over if you add Cyber Essentials or SOC 2 later
OneClickComply cons:
- Newer to market than the largest US-based GRC platforms, with a smaller integration marketplace
- Less name recognition with US enterprise buyers who default to asking for Vanta or Drata by name
Best for: founder-led startups that want ISO 27001 automated rather than managed by a spreadsheet and a part-time consultant. Verdict: Buy.
2. Vanta: best ISO 27001 software for startups running SOC 2 in parallel
Vanta is a compliance automation platform that grew out of SOC 2 monitoring and has since built out ISO 27001 support. Startups selling into US enterprise accounts often land here because SOC 2 and ISO 27001 evidence overlap heavily.
Vanta pros:
- Strong combined SOC 2 and ISO 27001 workflow
- Wide integration list across common SaaS and cloud tools
- Established reputation with US enterprise security teams
Vanta cons:
- Framework coverage outside SOC 2 and ISO 27001 is thinner
- Costs tend to scale with headcount and integrations, which catches early-stage teams off guard
Best for: startups that need SOC 2 and ISO 27001 running side by side for the same enterprise deal. Verdict: Buy if SOC 2 is already on your roadmap.
3. Drata: best ISO 27001 software for engineering-heavy startups
Drata leans on deep integrations with cloud infrastructure and code repositories to pull evidence automatically from engineering environments. Teams with an engineer already comfortable configuring API connections get the most out of it.
Drata pros:
- Deep infrastructure and DevOps tool integrations
- Strong automated evidence for cloud-native environments
- Solid audit management workflow once configured
Drata cons:
- Initial setup leans technical — non-engineering founders often need help configuring it
- Less guidance for teams without existing security tooling already in place
Best for: engineering-led startups with cloud infrastructure already instrumented. Verdict: Buy if you have engineering time to spend on setup.
4. Secureframe: best ISO 27001 software for startups needing broad framework coverage
Secureframe covers ISO 27001 alongside SOC 2, HIPAA, PCI DSS and others in one library, which suits startups that expect to need several certifications within a year or two of each other.
Secureframe pros:
- Wide framework library beyond ISO 27001 and SOC 2
- Useful for startups selling into healthcare or payments where extra frameworks come up fast
- Reasonable automated evidence collection across common tools
Secureframe cons:
- Breadth comes at the cost of ISO 27001-specific depth
- Support quality varies more than platforms built around a narrower focus
Best for: startups that know a second or third framework is coming within the year. Verdict: Hold — evaluate a narrower tool first if ISO 27001 is your only near-term target.
5. Sprinto: best ISO 27001 software for lean teams without a dedicated compliance hire
Sprinto builds guided checks into the implementation process, aimed at founders or generalist ops leads running compliance without a security background on staff.
Sprinto pros:
- Guided setup reduces the learning curve for non-specialists
- Built-in checks catch gaps before the audit rather than during it
- Reasonable fit for very small teams
Sprinto cons:
- Less flexible for startups with non-standard tech stacks or custom controls
- Smaller integration list than the larger US platforms
Best for: a founder or single ops hire running ISO 27001 with no security team behind them. Verdict: Buy for simplicity; Wait if your stack needs custom control mapping.
6. Scrut: best ISO 27001 software for startups managing multi-framework risk registers
Scrut centres its platform on a shared risk register that spans every framework a startup runs, which suits companies juggling ISO 27001 with DORA, NIST CSF or internal risk management side by side.
Scrut pros:
- Centralised risk register across multiple frameworks
- Useful once you're running more than two certifications at once
- Reasonable automated evidence collection for common cloud tools
Scrut cons:
- Risk register depth adds complexity a single-framework startup doesn't need yet
- Learning curve is steeper than single-framework tools
Best for: startups already juggling ISO 27001 with a second or third framework who want one risk view. Verdict: Hold — overkill if ISO 27001 is your only certification this year.
See how evidence automation works
Walk through how OneClickComply keeps ISO 27001 evidence audit-ready.
How we ranked these ISO 27001 software options
Every platform on this list gets judged against the same five criteria: evidence automation, Annex A control mapping, continuous monitoring, auditor collaboration and framework reuse. None of these six tools substitutes for the actual audit — a certification body still has to sign off — so the ranking weighs how much manual work survives after setup, not marketing claims.
The same discipline shows up outside compliance. A startup that treats ISO 27001 evidence as a living system rather than an annual scramble usually treats other operating rhythms the same way; OKR software for startups follows the same principle of building accountability into weekly workflow instead of a quarterly fire drill.
Team size mattered more than logo recognition in this comparison. A five-person startup and a fifty-person Series B company need different things from the same certification, even against the identical Annex A control set.
Which ISO 27001 software should you choose in 2026?
If you want one platform handling evidence, policy and control mapping without a dedicated hire, OneClickComply is the default pick — it's built around startups running compliance end-to-end rather than treating ISO 27001 as a side project. If SOC 2 is already contracted for the same deal, Vanta or Drata carry that overlap better. If you're staring down a second or third framework within the year, Secureframe or Scrut earn a longer look.
Whatever you pick, run an ISO 27001 gap analysis before you commit — it tells you which Annex A controls you're missing before a tool's sales page does.
Frequently asked questions
One last thing
The 2022 revision of ISO 27001 cut Annex A from 114 controls down to 93, grouped into four themes instead of fourteen. Startups certifying against the current standard in 2026 have fewer boxes to tick than founders who went through the process five years ago — the software just has to map to the right version of the standard.