Drata alternatives at a glance
| Platform | Best for | Key frameworks | Pricing | Watch out for |
|---|---|---|---|---|
| OneClickComply | UK teams that want failed tests fixed and policies kept consistent | Cyber Essentials, Cyber Essentials Plus, ISO 27001, SOC 2, NHS DSPT, NCSC CAF | Quote only, no per-framework fees | Focused on UK and international standards, not US-only ones like HIPAA |
| Vanta | A like-for-like swap for Drata | ISO 27001, SOC 2, GDPR, ISO 42001, NIS 2, DORA, HIPAA, PCI DSS | Quote only, priced by framework | Same core gap: it guides the fix, your team makes it |
| Secureframe | Guided onboarding and UK data hosting | ISO 27001, SOC 2, Cyber Essentials, GDPR, ISO 27701, ISO 42001, NIS 2, DORA | From $7,500 a year, one framework included | Each extra framework raises the price |
| Sprinto | Lean budgets and cloud-first startups | ISO 27001, SOC 2, Cyber Essentials, GDPR, ISO 27701, ISO 42001, NIS 2, DORA | Quote only, no per-user fees | Audit fees and extra frameworks on top |
| Scytale | Startups that want consulting in the bundle | SOC 2, ISO 27001, GDPR, ISO 42001, HIPAA, PCI DSS | From $7,500 a year, one framework included | Cyber Essentials isn't listed |
| OneTrust | Large, privacy-led programmes | 50+ standards and regulations, led by GDPR and privacy | Quote only, priced by admin users and assets | Built for enterprise; confirm SOC 2 and ISO 27001 scope |
| ISMS.online | Teams focused on ISO 27001 | ISO 27001, SOC 2, GDPR, ISO 27701, ISO 42001, NIS 2, DORA | Quote only, extra standards cost more | No automated technical monitoring |
Last checked 20 October 2026.
Why companies look for Drata alternatives
Drata is a US compliance automation platform with more than 8,500 customers and a 4.7 rating on G2. Most teams that look elsewhere aren't unhappy with its monitoring. Instead, they hit one of the problems below, usually at renewal or when they're looking to add a second framework. These are the reasons our compliance experts hear most often from teams moving away from Drata.
1. It flags the failure, but fixes need to be done manually
Drata runs automated tests against your systems and flags what fails. Since June 2026 it uses AI to explain why a test failed and list the steps to fix it (although failure guidance only covers some tests). Drata can't apply fixes automatically, so someone on your team still makes every change by hand. That's where most teams spend the most time, especially small teams without a security engineer.
It doesn't have to work that way: some alternatives, including OneClickComply, apply the fixes for you.
2. The policy editor slows everything down
Prospects repeatedly tell us they find Drata's policy editor to be clunky. Reviewers have said similar things since 2021, reporting limited formatting, no tracked changes and tables cut off in PDF exports. If you already have policies, moving them in is a project of its own. Expect to copy, reformat and re-approve each document.
3. Policies drift out of line
Each policy is edited as its own document, so the same rule can end up worded differently in different places. One company we spoke to had three policies giving three different incident reporting timelines. An auditor will spot that and can raise it as a nonconformity, which you then have to correct and show evidence for.
4. Trust centre features change at renewal
Drata bought the trust centre company SafeBase in February 2025 and now sells its trust centre in tiers. Its plans page lists Foundation, Advanced and Enterprise trust centre plans, with features such as NDA signing, SSO and CRM integrations added at each step up. Another customer we spoke to found their trust centre quietly downgraded at renewal, while the price rose about 10%. If your customers rely on your trust centre links, get the tier your renewal includes in writing.
5. Every extra framework costs more
Drata's entry plan includes one framework, and more frameworks are add-ons. On Drata's own AWS Marketplace listing, each framework costs $7,500 a year at list price. So adding ISO 27001 to SOC 2 adds $7,500 a year, and every further framework adds the same again, unless you move up a tier.
How Drata prices
Drata doesn't publish prices on its website, but it does list them on two public marketplaces. Its pricing has three parts, plus a separate route for UK public-sector buyers.
- A platform fee, sized by headcount. On its AWS Marketplace listing, Drata charges $25,000 a year for a company of up to 100 staff. Larger teams get a custom quote.
- A fee for each framework. The same listing prices each framework, including SOC 2, ISO 27001 and GDPR, at $7,500 a year. Drata's plans include one framework at the entry tier.
- Add-on modules. Higher trust centre tiers, risk management and user access reviews are priced on top, depending on your plan.
- UK public-sector pricing. Through a UK reseller on the government's G-Cloud marketplace, Drata starts at £6,300 a year for up to 50 staff, with a two-year minimum contract.
These are list prices. Whatever you're quoted, ask for the tier, the frameworks included and the renewal cap in writing. For a side-by-side on price, see OneClickComply vs Drata.
The 7 best Drata alternatives
1. OneClickComply
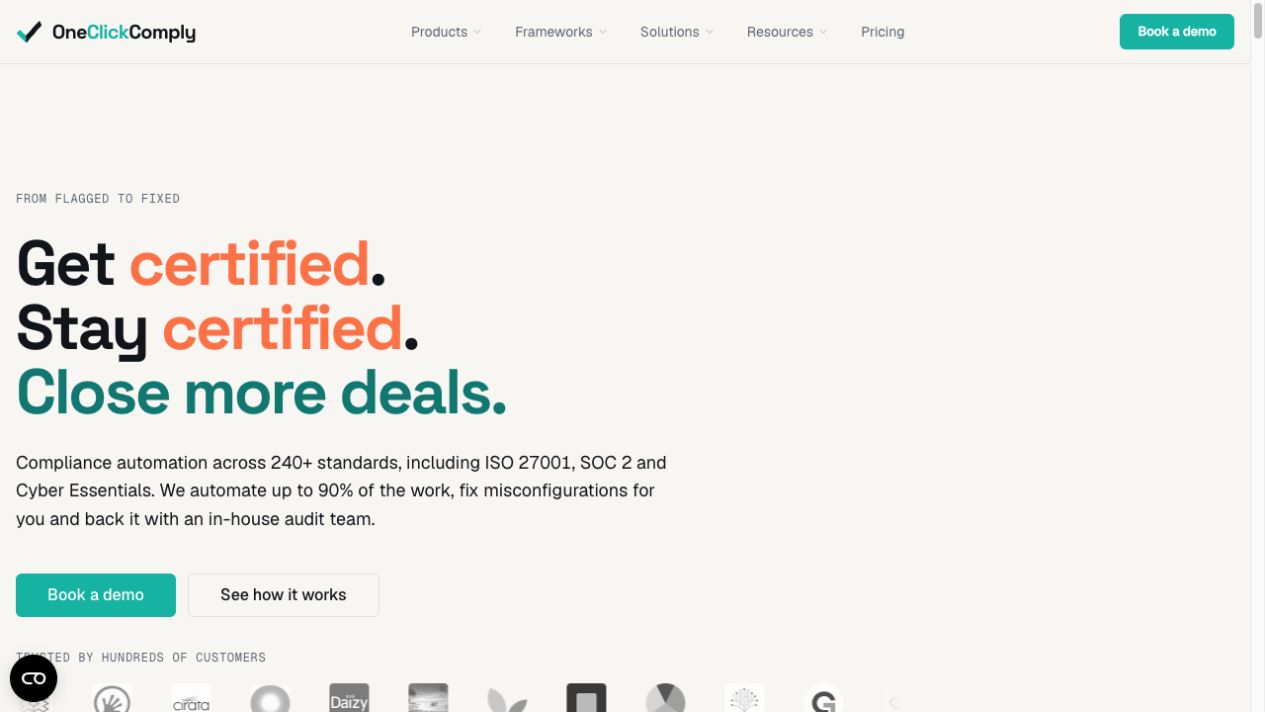
Overview: OneClickComply is a UK compliance automation platform that gets businesses certified and keeps them certified. Where Drata flags a failed test and explains the fix, OneClickComply makes the fix for you. Its policies are written from your live system settings, so the same rule reads the same way in every document.
“The speed at which the OneClickComply platform gave us clear visibility into our technical controls and aligned them seamlessly with best-practice frameworks, was astonishing.”
Dept. Insp. Martin Wilson PhD, Durham Police
Key features:
- OneClickFix applies fixes to 1,000+ technical controls in Microsoft 365, Google Workspace and AWS
- Policies generated from your live system settings, so wording stays consistent across documents
- Automated evidence collection from the tools and cloud accounts you already use
- Accredited auditors on hand in Slack or Teams
- Trust Centre and security questionnaire automation
- Any Auditor Guarantee: fail a SOC 2 Type II, ISO 27001 or Cyber Essentials Plus audit and we refund the audit fee and what you paid us, subject to terms
Frameworks: ISO 27001, SOC 2, Cyber Essentials, Cyber Essentials Plus, NHS DSPT, NCSC CAF, NIST CSF, CIS v8 and ISO 9001.
Limitations: Focused on UK and international standards, so it doesn't cover US-only frameworks such as HIPAA or FedRAMP.
Pricing: Quote only, with no per-framework pricing.
Location: UK.
Best suited to: UK and international businesses that need ISO 27001 and SOC 2 alongside UK frameworks such as Cyber Essentials, NHS DSPT and NCSC CAF.
2. Vanta
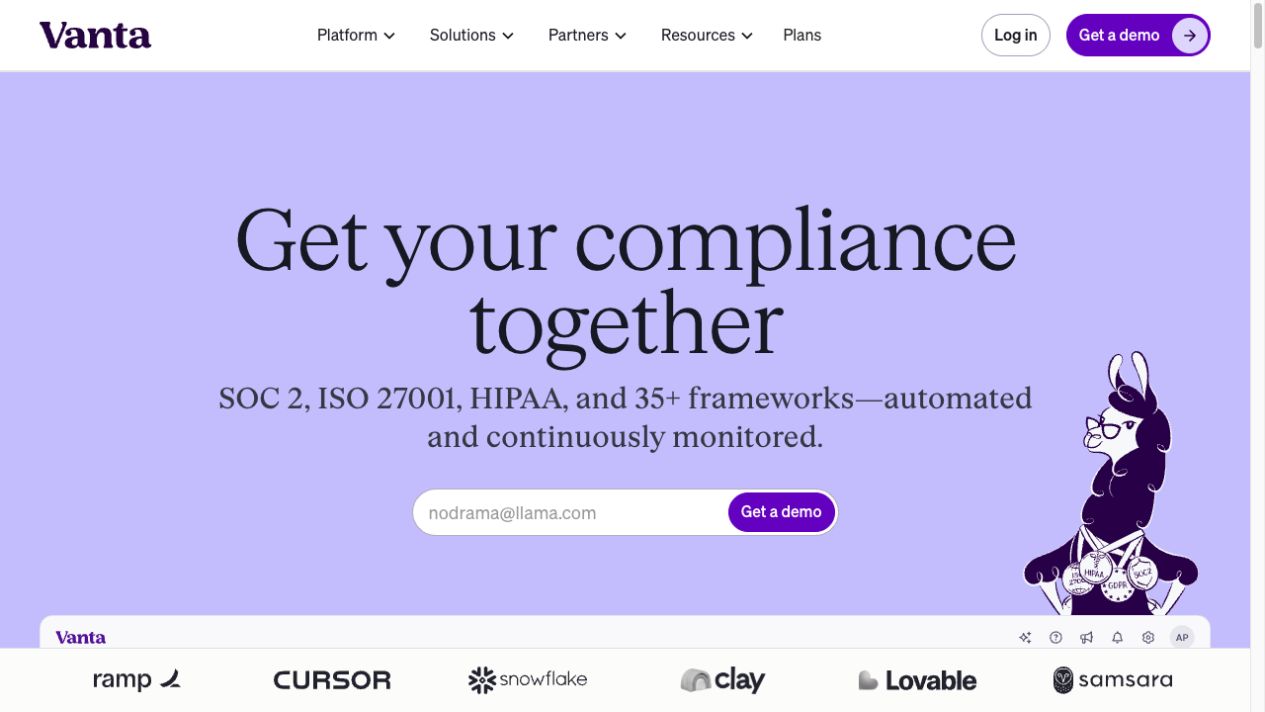
Overview: Vanta is the category leader and Drata's closest competitor, with more than 16,000 customers and an EMEA headquarters in London since 2025. For teams leaving Drata, it's the most like-for-like swap. Read our full guide to Vanta alternatives before you commit.
“We were looking at Drata and Secureframe, but we chose Vanta mainly for it's partnership with auditors in the UK. That's a very big plus, and well done for doing that.”
Key features:
- Continuous monitoring with automated tests
- 400+ integrations
- AI-written fix instructions for failed tests
- Trust Center and questionnaire automation
- Controls mapped across 35+ frameworks
Frameworks: ISO 27001, SOC 2, GDPR, ISO 27701, ISO 42001, NIS 2, DORA, HIPAA and PCI DSS, plus 25+ more.
Limitations: It shares Drata's core gap. Vanta's AI writes the fix instructions, but your team applies them. Pricing is per framework, so adding ISO 27001 or Cyber Essentials to SOC 2 raises the bill.
Pricing: Quote only, priced by framework.
Location: US, with an EMEA headquarters in London.
Best suited to: Teams that want the largest integration library and are happy to apply fixes themselves.
3. Secureframe
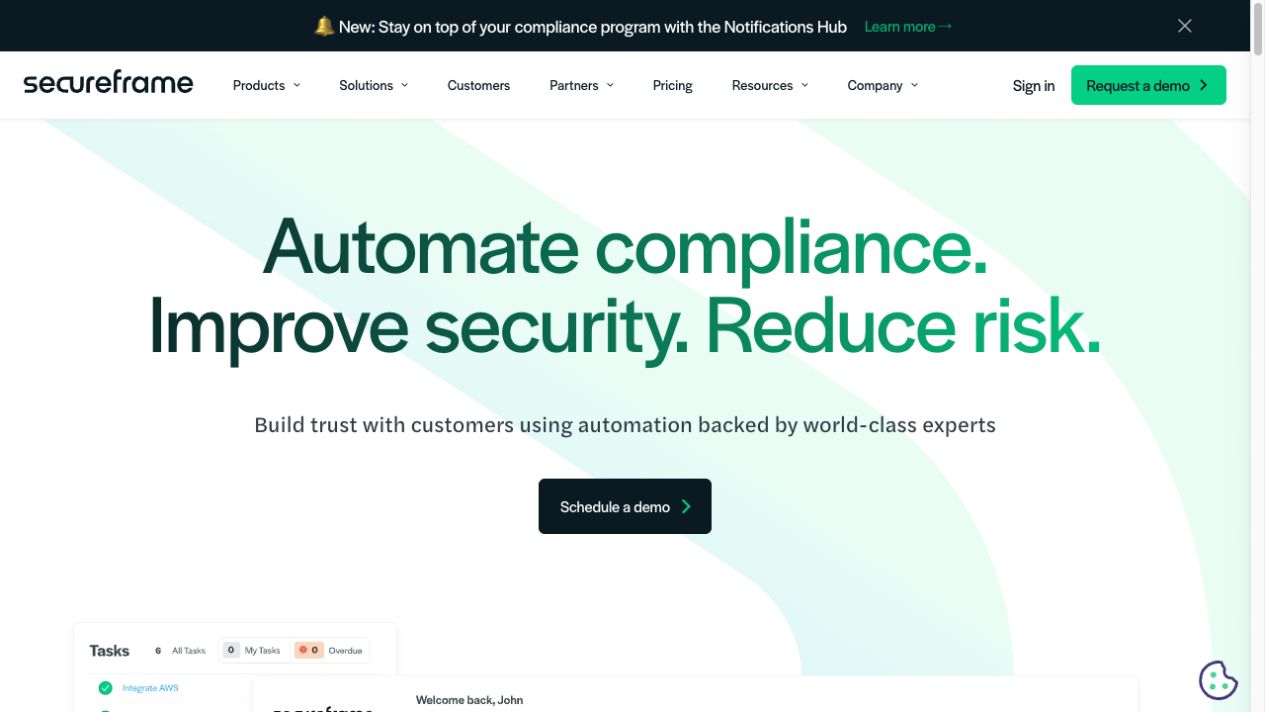
Overview: Secureframe is a US compliance automation platform known for guided onboarding and in-house compliance experts. Its Trust Center comes with the entry plan, which matters if trust centre tiers are why you're leaving Drata. See OneClickComply vs Secureframe.
“I would recommend Secureframe to anyone with a B2B SaaS business that is looking to get SOC 2 compliant fast. This was just the best way to do it. It made the process better, more structured, more streamlined so we could focus on what we do best.”
Key features:
- Automated evidence collection and cloud monitoring
- Comply AI for remediation suggestions, policies and risk
- Trust Center from the entry plan
- Questionnaire automation and advanced vendor risk on the Complete plan
- Hosting in the AWS London region
Frameworks: ISO 27001, SOC 2, Cyber Essentials, GDPR, ISO 27701, ISO 42001, NIS 2, DORA, HIPAA and PCI DSS, plus 30+ more.
Limitations: Frameworks are priced by quantity, so adding ISO 27001 to SOC 2 raises the bill. Remediation suggestions still need someone to apply them.
Pricing: From $7,500 a year for the Fundamentals plan, which includes one framework. Higher plans are quote only.
Location: US, with hosting available in the AWS London region.
Best suited to: SaaS teams that want guided onboarding, including UK teams that want their data held in the UK.
4. Sprinto
Overview: Sprinto is a compliance automation platform built for cloud-first companies on lean budgets, usually starting with SOC 2. It doesn't charge per user, so your whole team and your auditors can work in it. See OneClickComply vs Sprinto.
“Fast SOC 2 Setup, Clear UI, and Evidence Collection That Runs Itself”
Tharageshwaran S., Software Engineer, Information Technology and Services (50 or fewer employees)
Key features:
- Automated monitoring and evidence collection
- Controls built once and reused as you add frameworks
- A partner auditor network, or bring your own auditor
- A dedicated onboarding manager
- No per-user fees
Frameworks: ISO 27001, SOC 2, Cyber Essentials, GDPR, ISO 27701, ISO 42001, NIS 2, DORA, HIPAA and PCI DSS, from 200+ in total.
Limitations: Sprinto isn't an auditor, so audit fees sit on top. Extra frameworks add to the annual fee.
Pricing: Quote only. Price depends on frameworks and company size.
Location: US and India. No UK or EU data region advertised.
Best suited to: Cloud-first startups starting with SOC 2. UK teams should check auditor options for ISO 27001 certificates their customers will recognise.
5. Scytale
Overview: Scytale pairs compliance software with consulting. Its startup plans can include readiness consulting and a web app penetration test, which suits teams that want an expert to tell them what to fix. See OneClickComply vs Scytale.
“Solid Performance, Reliable platform, and a GRC Manager Who Keeps Everything on Track”
Jaeson S., IT Governance, Risk and Compliance (50 or fewer employees)
Key features:
- Startup plans with optional readiness consulting and penetration testing
- AI risk mapping and remediation suggestions on its Scale plan
- Auditor hub for working with your auditor in the platform
- Custom frameworks and on-premise integrations
- Policy and procedure templates
Frameworks: SOC 2, ISO 27001, GDPR, ISO 42001, HIPAA, PCI DSS, SOX ITGC and CMMC.
Limitations: Cyber Essentials isn't listed. Consulting helps you plan the fix, but your team still makes most changes.
Pricing: From $7,500 for 12 months with one framework (AWS Marketplace). Consulting plans are quote only.
Location: US and Israel.
Best suited to: SaaS startups that want a done-with-you first SOC 2, with pen testing in the same contract.
6. OneTrust
Overview: OneTrust is an enterprise trust and privacy platform. It's best known for privacy work such as consent and data subject requests, with a Tech Risk & Compliance module for frameworks. It also owns Tugboat Logic, a compliance automation tool it bought in 2021.
“Easy to use, and quickly creates policies. Creates SOC2 instantly. … Far easier to deal with than any other competitors we researched.”
Ryley M., Mid-Market (51–1,000 employees)
Key features:
- Templates and guidance across 50+ standards, regulations and frameworks
- Policy lifecycle management, with reviews, approvals and attestations
- Automated risk assessments and control management
- Third-party risk management
- Privacy automation for consent and data subject requests
Frameworks: GDPR and UK GDPR-led privacy programmes, plus security frameworks through Tech Risk & Compliance. Its pricing page doesn't name SOC 2 or ISO 27001, so confirm both are in your quote.
Limitations: Built for large organisations rather than scale-ups preparing for their first certification. SOC 2 and ISO 27001 coverage needs confirming in your quote.
Pricing: Quote only. Tech Risk & Compliance is priced by admin users and asset inventory.
Location: US and UK.
Best suited to: Enterprises whose compliance work is led by privacy, or that already use OneTrust for consent and data subject requests.
7. ISMS.online
Overview: ISMS.online is a UK platform, based in Brighton, built around ISO management systems. It's policy-led, so it suits teams leaving Drata because of the policy editor. It gives you a structured workspace for policies, risks and controls.
“It helps with the detailed and complex tasks by keeping everything streamlined and clear, providing a practical and much easier way to follow the process and get things done.”
Yannis P., CEO, Marketing and Advertising (51–1,000 employees)
Key features:
- Ready-made Headstart content and policy packs
- Virtual Coach guidance through each standard
- Risk register and supply chain module
- Integrations with Teams, SharePoint, Jira and Slack
- Onboarding led by ISO-qualified success managers
Frameworks: ISO 27001, SOC 2, GDPR, ISO 27701, ISO 42001, NIS 2, DORA, ISO 22301 and ISO 9001, from 100+ in total.
Limitations: It isn't a technical monitoring tool. It doesn't run automated tests on your cloud or devices, and it doesn't cover Cyber Essentials.
Pricing: Bespoke quote. Extra standards are optional add-ons.
Location: UK (Brighton).
Best suited to: UK and European organisations running one or more ISO management systems.
Drata or Vanta? Why a like-for-like swap may not fix the problem
Vanta is the obvious next stop for teams leaving Drata, and the two are close on automation, framework coverage and price. Before you swap one for the other, check whether Vanta actually solves the reason you're leaving, because often it doesn't.
| Why you're leaving Drata | Does moving to Vanta solve it? | Ask before you sign |
|---|---|---|
| Fixing failed tests by hand | No. Vanta's AI writes the fix steps, and your team still makes the change | When a test fails, who makes the change? |
| The policy editor and moving policies in | Partly. It's a different editor, but you still move, reformat and re-approve every policy | Can I import my policies as they stand? |
| Policies saying different things | Not by design. Policies are still edited one by one | Can one change update the same wording in every policy? |
| Trust centre features changing at renewal | It depends on your plan | Which trust centre features are in my tier at renewal? |
| Fees for each extra framework | No. Vanta also prices by framework | Is pricing per framework or bundled? |
| Price rises at renewal | Not necessarily. Vanta also quotes per deal and doesn't publish its prices | What's the renewal cap, in writing? |
If most of your answers are “no”, compare a platform that works differently, not just a different logo. For the other direction, see our guide to Vanta alternatives.
How to choose the right Drata alternative
Start with the reason you're leaving, then test each shortlisted platform against it. If you're not sure which frameworks you need, see how SOC 2, ISO 27001, Cyber Essentials and CIS v8 compare.
| Your reason for leaving | Look at | Ask every vendor |
|---|---|---|
| Time spent fixing failed tests | OneClickComply | When a test fails, who makes the change? Can I preview and undo it? |
| The policy editor or moving policies in | OneClickComply, ISMS.online | Can I import my existing policies? Who reformats them? |
| Policies saying different things | OneClickComply | Can one change update the same wording in every policy? |
| Trust centre features changing | Secureframe, OneClickComply | Which trust centre features are in my tier, now and at renewal? |
| Fees for each extra framework | OneClickComply, Sprinto | What does a second and third framework cost? |
| Wanting expert help with the first audit | Scytale, Secureframe | Who's my named expert, and how many hours are included? |
| A privacy-led enterprise programme | OneTrust | Which frameworks are in the package I'm quoted for? |
Four checks apply whatever you choose:
- Certification body: For ISO 27001, UK customers usually expect a certificate from a UKAS-accredited body. Ask which bodies the platform works with, and see our comparison of ISO 27001 certification bodies.
- Data location: Ask where your evidence is stored and how UK GDPR is covered. An EU hosting region isn't the same as a UK one.
- Contract term: Drata's G-Cloud listing sets a two-year minimum. Check the term, the notice period and the renewal cap before you sign anything new.
- Your stack: Check for native integrations with your cloud (AWS, Azure or Google Cloud), identity provider and code repository (GitHub, GitLab or Bitbucket). Gaps mean manual evidence.
What to do before you switch from Drata
Switching platforms doesn't reset your certification, but your trust centre and policies need planning.
- Reprice first: If cost is the only issue, a competing quote may be enough to renegotiate. Check your term and notice period, as Drata contracts can run for two years.
- Save your trust centre: Download every document, note the link your customers use, and list who has NDA access. Ask Drata how long the page stays live after your contract ends, and tell key customers where the new one will be.
- Export policies as editable files: PDFs are hard to move into a new platform, and some reviewers report Drata's PDF exports cut off tables. Check every table after export.
- Settle conflicting wording as you go: List the timelines, owners and retention periods each policy states, and pick one value for each. A move is the cheapest time to fix drift.
- Export everything else: Evidence history, risk register, asset and vendor lists, access reviews and auditor correspondence.
- Time it around your audit: Avoid switching mid-way through a SOC 2 Type 2 observation window. For ISO 27001, the gap after a surveillance audit is the easiest time.
- Remap, don't rebuild: Most of your controls carry over. The new platform should map them for you.
- Run both briefly: Keep Drata until the new platform shows the same controls passing.
Where OneClickComply fits
OneClickComply is built for UK teams who want the work done and not just tracked. It's a good fit if:
- You run on Microsoft 365, Google Workspace or AWS and want failed tests fixed for you, not explained to you.
- You want policies written from your live settings, with the same wording wherever a rule appears.
- You need ISO 27001, SOC 2 and Cyber Essentials together and don't want to pay per framework.
- You want answers from accredited auditors without booking a call.
It's not the right fit if:
- You need PCI DSS or HITRUST, which it doesn't cover today.
- You mainly need US-only frameworks such as HIPAA or FedRAMP.
If you're weighing up a move from Drata, book a demo and we'll show you how OneClickComply would handle your frameworks, policies and failed tests. Or see how we compare head to head in OneClickComply vs Drata.
Frequently asked questions
Drata is a trademark of Drata Inc. Other product names are trademarks of their owners. This comparison is based on public information and what prospects have told us. If anything here is out of date, contact us and we'll correct it.