Best starting point for a technology-focused SOC 2 audit: Schellman. Best shortlist alternatives: A-LIGN for combined compliance programmes, BDO for mid-market assurance, and Deloitte for multinational organisations. This 2026 guide helps you compare their fit, check who signs the report, and separate audit work from preparation.
Why this matters
Your auditor must produce the report your customer needs, not simply complete a compliance checklist. An engagement that excludes the service your customer buys does not solve the procurement requirement.
You also need to separate preparation from independent examination. OneClickComply supports SOC 2 compliance preparation through security control remediation, policy generation and risk management; the independent auditor examines your controls and issues the opinion.
SOC 2 is an attestation report, not an ISO-style certificate. For your 2026 selection, start with the required report, then choose the firm and preparation process that support it.
What makes the best SOC 2 audit firm?
Use these criteria before comparing names:
- Signing authority: Identify the licensed CPA firm responsible for the examination and final report.
- Relevant scope: Match the auditor's proposed work to your service, infrastructure, customers and contractual commitments.
- Report fit: Confirm whether you need Type I, Type II, or a staged approach accepted by your customer.
- Evidence process: Ask how auditors request, sample, review and query evidence from your systems.
- Independence: Separate management decisions and remediation from the auditor's examination responsibilities.
- Delivery ownership: Name the engagement lead, signing firm and escalation contact before work begins.
SOC 2 has 5 Trust Services Categories: security, availability, processing integrity, confidentiality and privacy. Security is the foundation; include additional categories when your service commitments and customer requirements justify them.
Do not add categories just to make the report look broader. Each addition needs a clear reason and supporting controls.
SOC 2 audit firms at a glance
These are engagement-fit recommendations, not measured scores for speed or service quality. Confirm the contracting entity and signing arrangements for every UK proposal.
| Firm | Best for | Standout fit | Key limitation to resolve |
|---|---|---|---|
| Schellman | Technology businesses seeking a specialist assurance firm | Technology-focused assurance practice | Confirm UK working arrangements and the exact engagement scope |
| A-LIGN | Businesses coordinating several compliance frameworks | Assurance work across SOC and other compliance programmes | Separate each deliverable, owner and examination requirement |
| BDO | Mid-market businesses aligning SOC reporting with wider assurance | International accountancy and advisory network | Confirm which member firm performs and signs the SOC examination |
| Deloitte | Multinational businesses with complex assurance governance | Global professional services network | Establish cross-border responsibilities and independence requirements |
A UK office is not a substitute for confirming who signs your SOC 2 report. Network names, contracting entities and report issuers are not interchangeable.
1. Schellman: best SOC 2 audit firm for technology specialists
Schellman is an assurance firm with a technology-focused practice that includes SOC examinations. It belongs on your shortlist when you want the discussion centred on the systems and controls behind your service.
Use the scoping call to explain your hosting model, deployment process and customer commitments. Ask the proposed team to describe how those details affect the examination rather than accepting a generic evidence checklist.
Schellman pros:
- Specialist assurance positioning fits a technology-led procurement discussion.
- SOC examination services match the required independent reporting role.
- Its technology focus gives you a relevant starting point for evaluating audit-team experience.
Schellman cons and checks:
- An assurance engagement does not transfer responsibility for controls or remediation away from your business.
- Confirm working hours, evidence handling and UK engagement arrangements rather than assuming local delivery.
Ask who will conduct fieldwork and how the team handles infrastructure changes during the reporting period. Request an explanation of the evidence expected for access reviews, change approvals and incident handling.
Best for: SaaS and technology businesses seeking a specialist assurance shortlist.
Verdict: Buy only after the proposed team demonstrates a clear understanding of your service boundary.
2. A-LIGN: best SOC 2 audit firm for combined compliance programmes
A-LIGN provides assurance services across SOC and other compliance frameworks. Consider it when SOC 2 sits alongside a broader compliance programme rather than operating as a standalone project.
The useful question is not whether evidence can be reused everywhere. Ask which underlying records support several requirements, and which examinations still need separate work and decisions.
A-LIGN pros:
- Its multi-framework practice fits a coordinated compliance discussion.
- SOC examination services address the independent audit requirement.
- Its range of assurance services gives you a basis for discussing related programmes with one provider.
A-LIGN cons and checks:
- Shared evidence does not make different frameworks equivalent or remove their separate requirements.
- A combined programme needs explicit boundaries between preparation, examination and certification activities.
For a 2026 engagement, request a deliverables schedule that separates each report or certification activity. Name the responsible entity and decision-maker for each part.
Do not accept an umbrella description of compliance work in place of a defined SOC 2 examination. Your customer needs the right report, regardless of how the wider programme is packaged.
Best for: Businesses coordinating SOC 2 with other assurance or certification work.
Verdict: Buy when the proposal makes each framework's scope and responsibilities explicit.
3. BDO: best SOC 2 audit firm for mid-market assurance coordination
BDO is an international accountancy and advisory network with SOC reporting services. It belongs on the shortlist when your business wants to discuss SOC 2 alongside wider assurance and governance needs.
Start with the actual service team, not the network name. Ask which member firm contracts with you, which team performs the examination and which entity signs the report.
BDO pros:
- Its wider assurance practice fits discussions involving finance, risk and technology leaders.
- SOC reporting services provide a relevant route to the required examination.
- Its international network gives cross-border businesses a starting point for discussing local coordination.
BDO cons and checks:
- Network membership does not establish which entity is authorised to issue your report.
- Existing relationships require an independence check before you assume the same organisation can accept the engagement.
Bring your customer requirement and system description to the first substantive meeting. Request direct access to the proposed SOC engagement lead so you can assess technical fit before appointment.
Make evidence ownership clear internally. A wider advisory relationship does not remove your responsibility to operate controls and approve the system description.
Best for: Mid-market businesses coordinating SOC reporting with broader assurance requirements.
Verdict: Buy when the named member firm and delivery team meet your reporting needs.
4. Deloitte: best SOC 2 audit firm for multinational governance
Deloitte provides SOC reporting services through its professional services network. Consider it when several entities, jurisdictions or governance teams need to contribute to the examination.
Complex organisations need a clear service boundary. Explain which legal entities deliver the service, where controls operate and which teams own the supporting evidence.
Deloitte pros:
- Its international network fits a cross-border assurance discussion.
- SOC reporting services match the required reporting category.
- Its broader assurance practice is relevant when several governance functions must coordinate.
Deloitte cons and checks:
- A global network does not remove the need for a named signing entity and accountable engagement lead.
- Existing audit or advisory relationships need an independence review before appointment.
Ask the proposed team to distinguish the in-scope service from the rest of your organisation. A large corporate structure does not mean every system or subsidiary belongs in the report.
Your proposal should explain how overseas teams contribute evidence and how unresolved questions reach the person authorised to decide them.
Best for: Multinational organisations with distributed control ownership and formal assurance governance.
Verdict: Buy when the engagement structure matches your organisational complexity without expanding scope unnecessarily.
How to compare proposals in 2026
Request 3 proposals against 1 scope brief. These are practical buying recommendations, not market benchmarks; the purpose is to make the responses comparable.
Define scope
Describe the service your customer uses, its supporting systems and the people responsible for controls. Include important outsourced services and explain how you oversee them.
Write down exclusions. An auditor cannot resolve an unclear business boundary merely by requesting more evidence.
Confirm issuer
Ask for the legal name of the signing CPA firm and the applicable licensing details. Confirm the reporting standards and obtain written clarity on any separate contracting or delivery entities.
A UK-facing sales team is not proof of signing authority. Check the proposed arrangement itself.
Check evidence
Request a sample evidence request list and an explanation of the review process. Ask how the auditor handles incomplete records, exceptions and changes during the examination.
Use the SOC 2 readiness checklist guide to organise preparation before you commit to audit dates.
Agree responsibilities
Name your internal control owners, the auditor's engagement lead and the person approving the system description. Document who resolves scope questions and how changes affect the engagement.
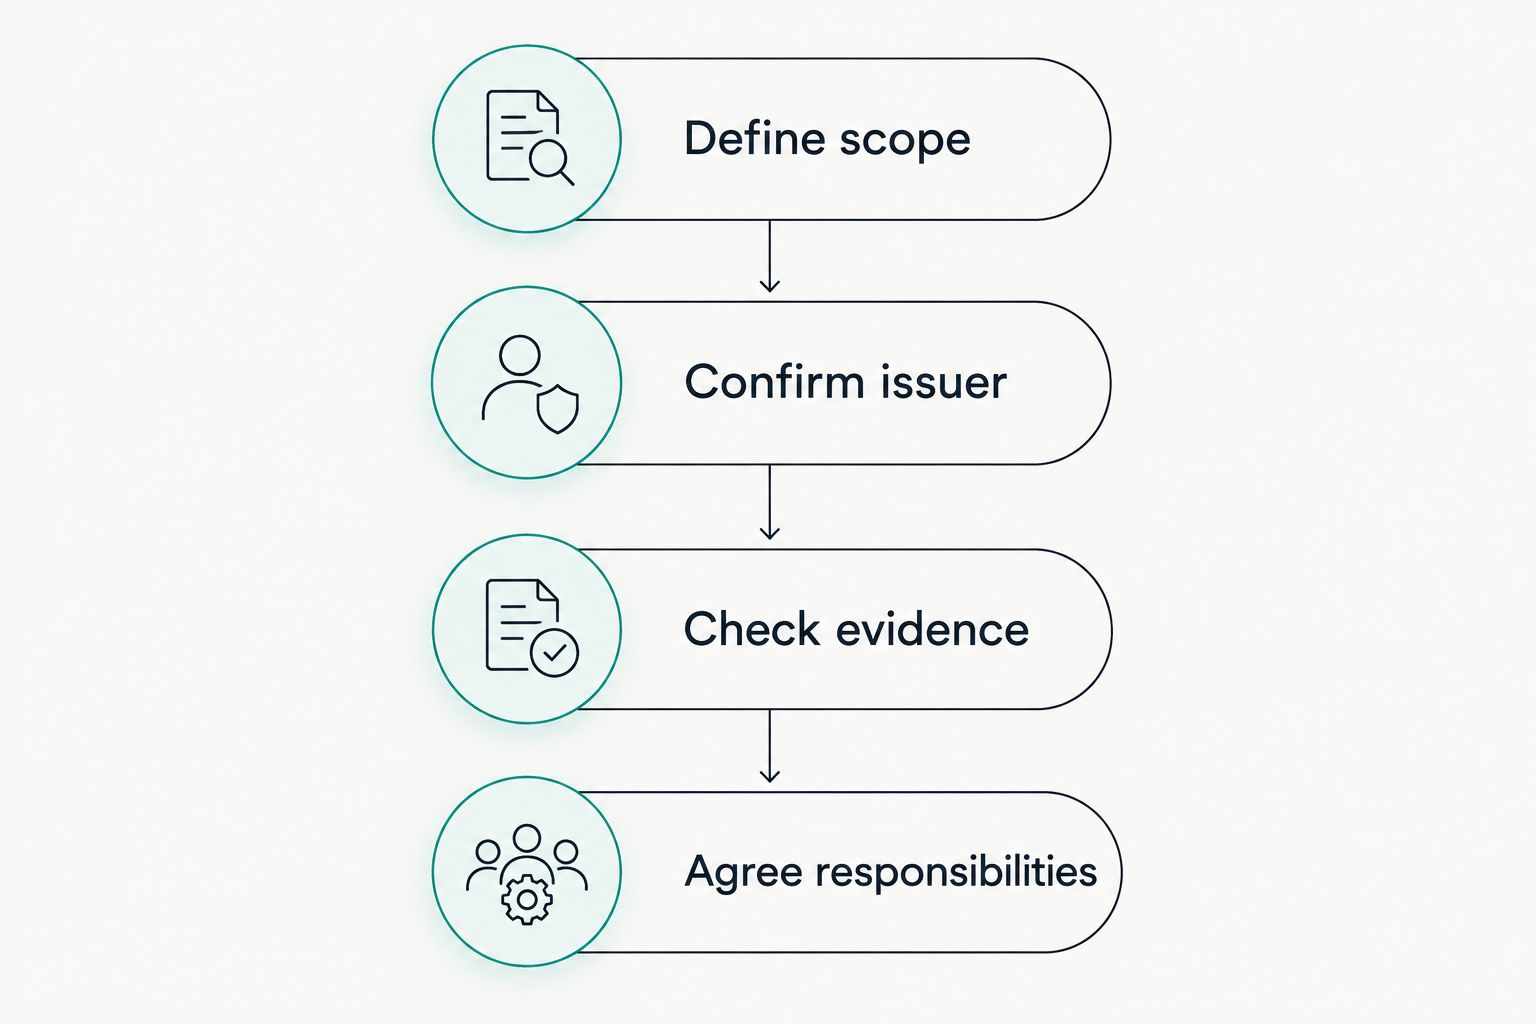
Agree the same scope before comparing audit proposals.
Compare the substance of each response. A proposal that identifies your unresolved scope questions is more useful than one that simply repeats your requested completion date.
Choose the report before choosing the timetable
SOC 2 has 2 report types. They answer different questions, so confirm which one your customer expects before agreeing the engagement.
| Report | What it examines | Best for | Main limitation |
|---|---|---|---|
| Type I | Control design at a specified date | Demonstrating that controls are suitably designed at that date | Does not establish operating effectiveness over a period |
| Type II | Control design and operating effectiveness over a specified period | Demonstrating how controls operated during that period | Requires evidence covering the examination period |
Do not treat a Type I report as an automatic substitute for Type II. Ask the customer whether the proposed report satisfies its procurement requirement.
For your 2026 plan, work backwards from the required report and evidence period. A firm cannot retrospectively create records proving that a control operated when your business did not retain them.
Keep preparation separate from the audit opinion
OneClickComply is best for growing businesses that want to automate SOC 2 preparation, not replace the independent auditor. The platform supports security control remediation, policy generation, risk management and trust centres.
Those functions support your compliance programme. They do not turn generated policies into proof that staff followed them, or remediation activity into an independent opinion.
OneClickComply advantages:
- Automates security control remediation.
- Generates policies for your compliance programme.
- Supports risk and trust centre management.
OneClickComply boundaries:
- Your business still owns its controls, approvals and management decisions.
- An independent auditor determines the examination findings and report opinion.
For 2026, assign accountable owners before automating tasks. Software handles defined work; your team must decide what the service promises and ensure those promises match actual practice.
How the shortlist is ranked
The order prioritises distinct buying situations: technology-specialist assurance, combined compliance programmes, mid-market coordination and multinational governance. It does not claim that one firm delivers better outcomes across every engagement.
Apply the same criteria to every proposal: signing authority, scope, report fit, evidence process, independence and delivery ownership. The proposed team and written engagement terms decide the appointment.
Which SOC 2 audit firm should you choose?
Start with Schellman if you are a technology business without a more specialised requirement. Add A-LIGN when several compliance programmes need coordination, BDO for broader mid-market assurance discussions, or Deloitte for multinational governance.
Then test the shortlist against your actual service. Do not select a firm solely because a customer recognises its name.
Choose the auditor that defines the right examination clearly and assigns an accountable team to deliver it. Keep preparation software and audit appointment decisions separate.
Frequently asked questions
One last thing
Ask each finalist to explain your proposed scope back to you. If the explanation omits the service your customer buys, resolve that gap before signing anything.
Make the report useful, not just complete. Seriously Simple Cyber Compliance.