Best overall: OneClickComply. Best for enterprise-scale continuous monitoring: Vanta. Best for SOC 2 Type II audit trails: Drata. Best for combined GDPR and security framework mapping: Secureframe. Best for early-stage startups chasing one certification fast: Sprinto. Best budget entry point for lean teams: Scrut Automation.
Why this matters
Compliance software vendors rarely publish real numbers on their pricing pages in 2026 — most gate cost behind a sales call. That's not laziness. It's because the cost driver isn't the platform fee, it's what you're certifying.
ISO 27001:2022 runs 93 Annex A controls. Cyber Essentials needs re-certifying every 12 months. SOC 2 Type II reports cover an observation window, not a point-in-time snapshot. Every one of those variables changes what a platform actually charges you, regardless of the number on the homepage.
That's why ranking by pricing model beats ranking by a number that goes stale the day a vendor changes its plans. OneClickComply automates ISO 27001, Cyber Essentials, and SOC 2 evidence collection end-to-end, and this guide ranks it against the tools UK buyers compare it to most.
What makes the best compliance automation software
- Framework coverage — does one subscription cover ISO 27001, SOC 2, Cyber Essentials, and GDPR, or do you pay per add-on?
- Evidence automation depth — does it pull evidence from your stack automatically, or does someone still screenshot settings pages?
- Audit and certification body support — can it hand an auditor a ready packet, or does it just store documents?
- Pricing transparency — is the cost driver framework count, employee headcount, or a flat platform fee?
- UK-specific scheme fit — does it map cleanly to Cyber Essentials and NCSC guidance, not just US-centric SOC 2 workflows?
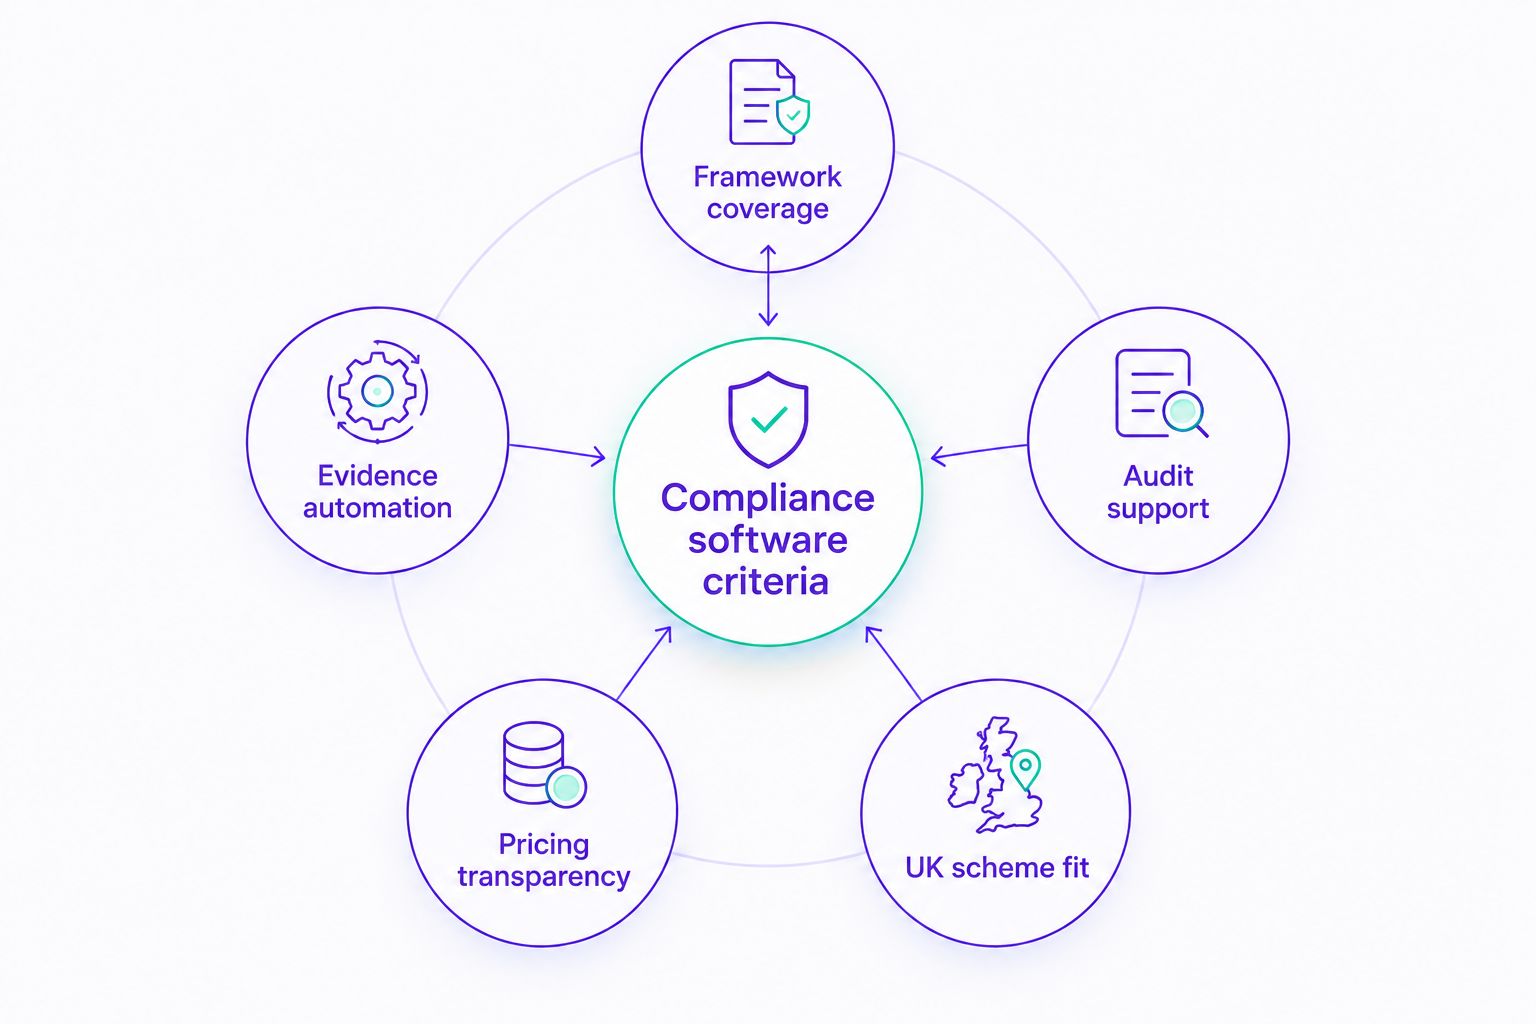
Pricing transparency only means something once the other four boxes are ticked.
Best compliance automation software ranked by price, at a glance
| Tool | Best for | Standout feature | Pricing model | Key limitation |
|---|---|---|---|---|
| OneClickComply | Growing UK businesses running multiple certifications | Automated evidence collection across ISO 27001, Cyber Essentials, SOC 2 | Framework-based pricing | Newer platform than the US incumbents |
| Vanta | Enterprise-scale continuous monitoring | Broad integration library for automated checks | Per-employee plus framework add-ons | Cost climbs fast as headcount grows |
| Drata | SOC 2 Type II audit trails | Continuous control monitoring tied to auditor workflows | Per-framework, per-integration | Heavier setup for teams without a dedicated admin |
| Secureframe | Combined GDPR and security framework mapping | Single control library mapped across frameworks | Per-framework tiering | GDPR tooling is less deep than dedicated privacy platforms |
| Sprinto | Early-stage startups chasing one certification fast | Fast single-framework onboarding | Entry-level flat tier, scales with frameworks | Thinner multi-framework depth than platform-first tools |
| Scrut Automation | Lean teams on a tight compliance budget | Low-friction setup for a first certification | Accessible entry tier | Fewer enterprise-grade integrations |
1. OneClickComply: best compliance automation software for growing UK businesses
OneClickComply automates ISO 27001, Cyber Essentials, and SOC 2 evidence collection so a small team can run certification without hiring a compliance manager. It handles the framework-mapping and audit-prep work that eats weeks when done manually, and it's built for businesses managing more than one certification at once.
OneClickComply pros:
- Covers ISO 27001, Cyber Essentials, and SOC 2 without separate tools for each
- Automates evidence collection instead of relying on manual uploads
- Built around UK schemes like Cyber Essentials, not bolted on as an afterthought
OneClickComply cons:
- Smaller market footprint than the US-founded platforms on this list
- Best value shows up once you're pursuing more than one framework
OneClickComply pricing: cost tracks the frameworks you're certifying, not your headcount, so a five-person team and a fifty-person team pay for what they actually pursue. See the ISO 27001 software built for lean security teams for a deeper breakdown of what that looks like in practice.
Best for: UK businesses running two or more certifications at once. Verdict: Buy.
2. Vanta: best compliance automation software for enterprise-scale continuous monitoring
Vanta connects to your cloud stack and flags control drift continuously, which suits larger organisations juggling many frameworks and vendors at once. It's one of the most integration-heavy platforms in the category.
Vanta pros:
- Deep integration library for automated control checks
- Strong fit for enterprises managing several frameworks simultaneously
- Established vendor risk and trust-centre features
Vanta cons:
- Pricing scales with employee count, which punishes headcount growth
- Framework add-ons stack cost quickly for multi-framework programmes
Vanta pricing: built around per-employee tiers plus paid framework add-ons, so cost rises with company size regardless of how much of the platform you actually use.
Best for: enterprises with dedicated security teams managing continuous monitoring at scale. Verdict: Hold unless headcount and integration depth justify the scaling cost.
3. Drata: best compliance automation software for SOC 2 Type II audit trails
Drata ties continuous control monitoring directly to auditor-facing workflows, which makes it a strong fit for companies already deep into a SOC 2 Type II observation period. It leans heavily on integrations to keep evidence current between audits.
Drata pros:
- Tight alignment between monitoring and audit readiness
- Strong SOC 2 Type II workflow support
- Frequent integration updates for cloud-native stacks
Drata cons:
- Per-framework and per-integration pricing adds up for multi-framework teams
- Setup takes longer without an internal admin dedicated to the rollout
Drata pricing: cost is driven by the number of frameworks and integrations connected, so a single-framework SOC 2 programme costs less than a multi-framework one. If SOC 2 is your starting point, the SOC 2 compliance software guide for startups walks through what to budget for first.
Best for: companies already running a SOC 2 Type II audit cycle. Verdict: Buy for SOC 2-first teams.
4. Secureframe: best compliance automation software for combined GDPR and security mapping
Secureframe maps a single control library across multiple frameworks, which cuts duplicate work when GDPR and a security certification overlap. It's positioned as a one-stop shop for teams that need both privacy and security coverage.
Secureframe pros:
- One control library mapped across several frameworks
- Reduces duplicate evidence work between GDPR and ISO 27001
- Reasonable fit for mid-market compliance teams
Secureframe cons:
- GDPR-specific tooling is thinner than dedicated privacy platforms
- Per-framework tiering still adds cost as you expand scope
Secureframe pricing: tiered by the number of frameworks mapped, so the more overlap you need managed in one place, the more it costs to unlock.
Best for: mid-market teams needing GDPR and a security framework mapped together. Verdict: Hold — solid, but not a specialist in either domain.
5. Sprinto: best compliance automation software for early-stage startups
Sprinto is built for speed on a first certification, with fast onboarding aimed at startups that need to close a deal gated on compliance. It trades some multi-framework depth for a lighter setup process.
Sprinto pros:
- Fast time-to-certification for a first framework
- Lighter onboarding than platform-first competitors
- Accessible entry tier for early-stage teams
Sprinto cons:
- Multi-framework depth thins out compared to platform-wide tools
- Less suited to teams already juggling three or more certifications
Sprinto pricing: entry-level flat tier that scales as you add frameworks, which keeps early costs low but climbs once you're managing more than one certification. The compliance automation software guide for startups covers this trade-off in more detail.
Best for: pre-Series-A startups closing their first enterprise deal. Verdict: Buy for a single-framework sprint.
6. Scrut Automation: best budget-friendly compliance automation software
Scrut Automation targets lean teams that need a first certification without a heavy setup lift. It's the most accessible entry point on this list for a team with no dedicated compliance hire.
Scrut Automation pros:
- Low-friction setup for a first-time certification
- Accessible entry tier for budget-constrained teams
- Straightforward for teams new to compliance software entirely
Scrut Automation cons:
- Fewer enterprise-grade integrations than Vanta or Drata
- Less depth for teams running multiple frameworks in parallel
Scrut Automation pricing: positioned at the accessible end of the category, built for teams prioritising cost over integration breadth.
Best for: lean teams starting their first certification on a tight budget. Verdict: Buy for a first framework; revisit once you add a second.
See your framework-based cost
Check how OneClickComply prices ISO 27001, Cyber Essentials, and SOC 2 together.
How pricing models actually differ
Most of the cost difference between these platforms doesn't come from the platform itself — it comes from what triggers the bill. Per-employee models punish headcount growth. Per-framework models punish scope growth. Flat platform pricing punishes neither, but tends to sit at the higher end for very small teams.
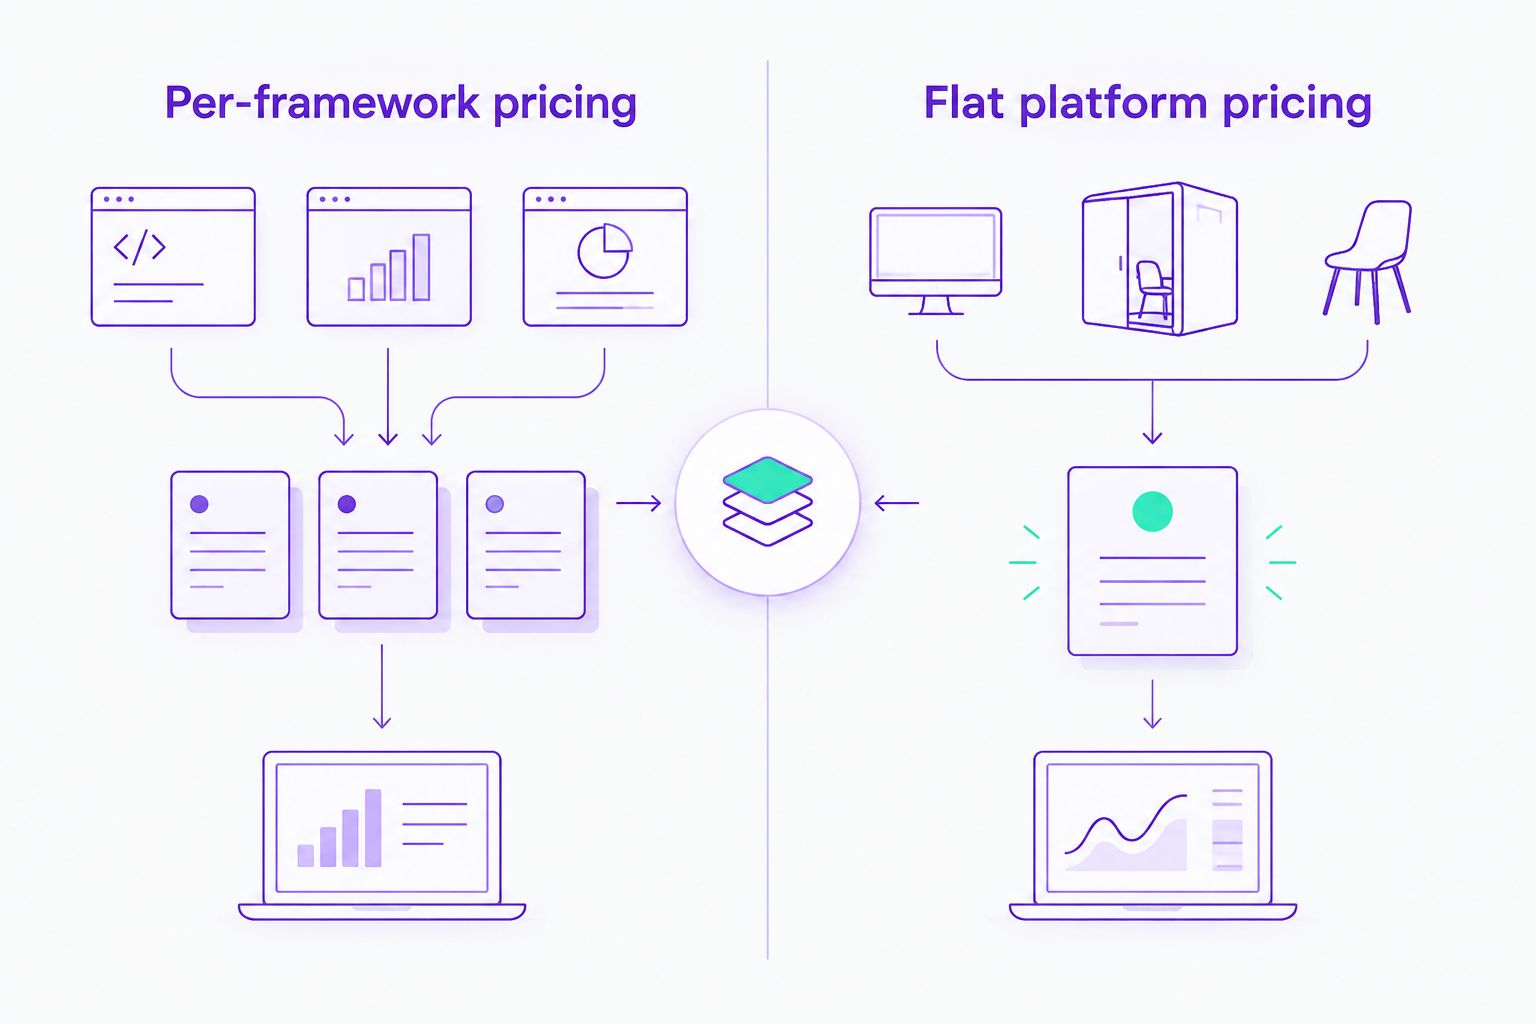
Per-framework pricing rewards a narrow scope; flat pricing rewards running everything through one platform.
How we ranked
Each platform was compared against the five criteria above: framework coverage, evidence automation depth, audit support, pricing transparency, and UK scheme fit. Pricing model — not a published dollar figure, which changes without notice — decided where a tool landed on cost. Frameworks supported and integration depth decided fit.
Which compliance automation software should you choose?
If you're a UK business running ISO 27001, Cyber Essentials, or SOC 2 — or heading toward more than one of them — OneClickComply is the default pick in 2026: it automates evidence collection across all three without stacking separate subscriptions.
If you're an enterprise already committed to heavy integration coverage, Vanta earns its per-employee cost. If you're mid-SOC-2-audit right now, Drata's audit-tied monitoring is worth the setup time. Startups chasing a single certification fast should look at Sprinto or Scrut Automation before anything platform-wide. Before committing to any of them, run the numbers through the compliance automation ROI calculator — the pricing model matters more than the sticker on the homepage.
Frequently asked questions
One last thing
The number on a vendor's pricing page tells you less than the mechanism behind it. A platform that charges by framework rewards a business that certifies once and stops; one that charges by employee count rewards a business that never grows past its current headcount. Neither describes most companies pursuing ISO 27001, Cyber Essentials, or SOC 2 in 2026 — so pick the pricing model that matches where the business is headed, not where it sits today.