Best overall: OneClickComply. Best for SOC 2-first client bases: Vanta. Best budget option: Scrut Automation. Here's how the best GRC software for MSPs stacks up in 2026 when you're running ISO 27001, Cyber Essentials and SOC 2 across a growing client book instead of a single company.
Why this matters
Most GRC platforms were built for one company managing its own certification. MSPs run compliance for ten, thirty, or a hundred client accounts at once, each with its own auditor, deadline, and evidence trail.
Buying the wrong platform means paying per-seat pricing that punishes growth, or juggling separate logins for every client because the tool has no multi-tenant view. The ISO 27001 for managed service providers guide covers the certification side of this in more depth — this list is about the software that runs it.
The six platforms below get judged on the same six criteria, not on brand recognition.
What makes the best GRC software for MSPs
- Multi-client architecture — one login, separate client workspaces, no data bleed between accounts
- Framework coverage — ISO 27001, Cyber Essentials, SOC 2 and GDPR under one roof, not four separate tools
- Evidence automation — pulls control evidence from client systems instead of manual screenshot chasing
- Client-facing reporting — a trust centre or status view clients can check without emailing you
- Audit trail per client — every action logged and exportable when an auditor or client asks for proof
- Per-client pricing — cost scales with accounts managed, not per internal seat
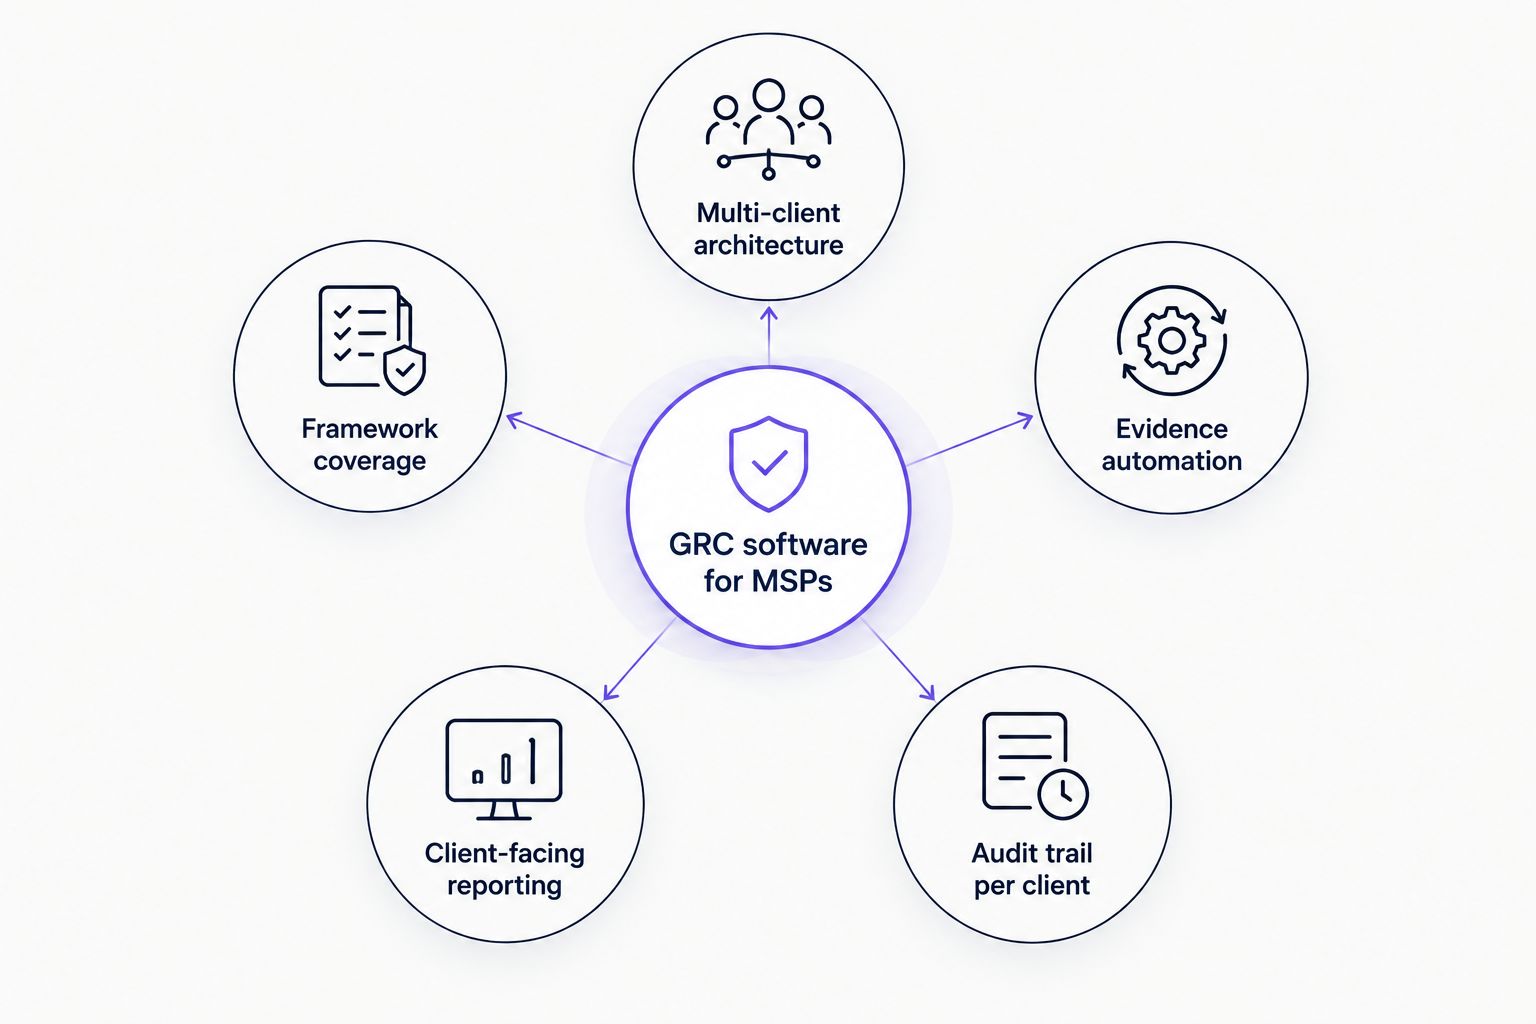
Multi-client architecture is the criterion single-tenant platforms consistently miss.
At a glance
| Platform | Best for | Standout feature | Key limitation |
|---|---|---|---|
| OneClickComply | MSPs certifying multiple clients across ISO 27001, Cyber Essentials, SOC 2 | Automated evidence collection across separate client workspaces | Framework list is still expanding beyond core UK/SaaS certifications |
| Vanta | SOC 2-first client bases | Broad integration library for SaaS control monitoring | Built for single-tenant use; MSP account separation is a workaround |
| Drata | Continuous control monitoring at scale | Automated control testing and alerting | Same single-tenant design as Vanta — not native multi-client |
| Secureframe | MSPs bundling GRC with resold security tooling | Combines compliance automation with vendor security add-ons | Framework depth varies by add-on package |
| Hyperproof | Multi-framework programs across many clients | Strong program and workflow management for complex audits | Steeper setup time before it pays off |
| Scrut Automation | Budget-conscious MSPs starting out | Lower-cost entry point for early client rosters | Thinner ecosystem of integrations than the larger players |
1. OneClickComply: best GRC software for MSPs managing certifications across their client book
OneClickComply automates evidence collection and control tracking for ISO 27001, Cyber Essentials, and SOC 2, built around handling compliance end-to-end rather than one checklist at a time. For an MSP, that means one workspace covering several client certifications instead of stitching together spreadsheets per account.
OneClickComply pros:
- Automates evidence collection instead of manual screenshot gathering
- Covers ISO 27001, Cyber Essentials and SOC 2 without switching tools
- Built around a hands-off model — the platform handles compliance so the team focuses on client delivery
- UK-based support model, useful for MSPs whose clients need Cyber Essentials specifically
OneClickComply cons:
- Framework coverage is UK-and-core-frameworks focused; confirm your niche frameworks are covered before switching
- Newer to the market than legacy risk platforms, so third-party integration count is still growing
Best for: MSPs running ISO 27001, Cyber Essentials, and SOC 2 certifications across a client portfolio. Verdict: Buy.
2. Vanta: best GRC software for MSPs with SOC 2-heavy client bases
Vanta automates control monitoring and evidence gathering primarily for SOC 2 and ISO 27001, with a wide catalogue of cloud and SaaS integrations. It was designed for a single company managing its own compliance program, not an MSP account structure.
Vanta pros:
- Wide integration library for pulling evidence from common SaaS stacks
- Mature SOC 2 workflow, useful when most clients are US-facing SaaS businesses
- Frequent framework updates as standards change
Vanta cons:
- Single-tenant design means MSPs manage separate instances per client rather than one unified view
- Cyber Essentials support is thinner than SOC 2/ISO 27001 coverage
Best for: MSPs whose client book is dominated by SOC 2-seeking SaaS companies. Verdict: Hold if most clients also need Cyber Essentials or UK-specific frameworks.
3. Drata: best GRC software for MSPs needing continuous control monitoring
Drata focuses on continuous control testing rather than point-in-time evidence snapshots, alerting when a control drifts out of compliance between audits.
Drata pros:
- Continuous monitoring catches control drift between formal audits
- Automated alerting reduces manual re-checks
- Solid audit trail for individual client accounts
Drata cons:
- Same single-tenant architecture as Vanta — no native multi-client dashboard
- Setup per client account takes real time before automation kicks in
Best for: MSPs managing a smaller number of clients where continuous monitoring per account matters more than volume. Verdict: Hold for large client rosters, Buy for a handful of high-touch accounts.
4. Secureframe: best GRC software for MSPs bundling compliance with resold security tools
Secureframe pairs compliance automation with vendor security add-ons, useful for MSPs that already resell endpoint or network security products alongside compliance work.
Secureframe pros:
- Bundles compliance tracking with security tooling in one commercial relationship
- Reasonable framework spread across SOC 2, ISO 27001, and others
Secureframe cons:
- Framework depth depends on which add-on package is purchased
- Multi-client management still runs through separate client instances
Best for: MSPs already reselling security products who want compliance bundled into the same vendor relationship. Verdict: Hold — evaluate against a dedicated compliance platform first.
5. Hyperproof: best GRC software for MSPs running complex multi-framework programs
Hyperproof leans into program and workflow management for organisations juggling several frameworks at once, with strong task assignment and audit prep features.
Hyperproof pros:
- Strong workflow and task management across multiple frameworks
- Good fit for complex audits spanning several standards at once
Hyperproof cons:
- Setup time is longer before the automation pays off
- Overkill for MSPs whose clients need one or two core certifications
Best for: MSPs managing clients with layered compliance needs across several frameworks simultaneously. Verdict: Hold unless your client base genuinely needs multi-framework depth.
6. Scrut Automation: best GRC software for MSPs on a tighter budget
Scrut Automation offers a lower-cost entry point into compliance automation, aimed at teams just starting to formalize a client compliance program.
Scrut Automation pros:
- Lower cost of entry for MSPs with a small client roster
- Covers core frameworks without a large integration setup
Scrut Automation cons:
- Thinner integration ecosystem than the larger platforms on this list
- Less mature multi-client tooling as account count grows
Best for: MSPs onboarding their first few compliance clients before scaling up. Verdict: Buy for early-stage rosters, Wait once you pass a handful of active client accounts.
How we ranked these
Each platform was weighed against the six criteria above: multi-client architecture, framework coverage, evidence automation, client-facing reporting, audit trail depth, and per-client pricing shape. Platforms built natively around single-company use lose points on the first and last criteria, regardless of how strong their evidence automation is. The vendor risk management software for MSPs guide runs the same lens over a related but distinct category — vendor risk tracking rather than certification management.
See OneClickComply for your client book
Automate ISO 27001, Cyber Essentials and SOC 2 across every client account.
Which GRC software should you choose?
If clients need ISO 27001, Cyber Essentials, or SOC 2 and you want one workspace covering all three, OneClickComply is the default pick for 2026. If your book is nearly all SOC 2-seeking US SaaS clients, Vanta's integration depth earns its place. If you're managing two or three clients and need to keep costs down while the roster grows, start with Scrut Automation and revisit once volume picks up.
Don't buy on brand recognition alone — buy on whether the platform separates client accounts cleanly, because that's the one thing that breaks first at scale.
Frequently asked questions
One last thing
The platforms on this list that weren't built for MSPs — Vanta, Drata, Hyperproof — still get sold to MSPs constantly, because their brand recognition outpaces their account architecture. Ask any vendor a blunt question before you sign: how does a new client account get created, and does it show up in a separate workspace or bleed into your existing evidence library? The answer tells you more than any feature list.