Law firms shopping for ISO 27001 software in 2026 hit the same wall every time: most platforms are built for engineering teams shipping code, not fee-earners billing client hours and juggling client confidentiality obligations. This guide ranks six ISO 27001 compliance platforms against what a law firm actually needs — fast evidence collection, Annex A control mapping in plain language, and policy templates that respect privileged data.
Best overall for law firms: OneClickComply — automates evidence collection and maps controls to ISO 27001 Annex A without a dedicated compliance hire. Best for enterprise multi-framework programmes: Vanta. Best for continuous control monitoring: Drata. Best for combining SOC 2 and ISO 27001 in one platform: Secureframe. Best for documentation-heavy policy management: ISMS.online. Best budget option for lean two-to-five-partner practices: Sprinto.
Why this matters
Corporate clients, insurers and panel appointments increasingly ask solicitors to prove information security before instructing them — a signed engagement letter isn't enough in 2026. ISO 27001 for law firms and legal services sets out why the certification has moved from nice-to-have to a panel requirement at several UK insurers and corporate clients.
A law firm's data set is different from a typical SaaS business: privileged correspondence, case files, conflicts records, and client money. Generic IT-first compliance software forces you to translate every control into legal-sector terms yourself. That translation gap is where most law firm certification projects stall.
What makes the best ISO 27001 software for law firms
- Annex A control mapping in legal-sector language, not generic IT jargon a fee-earner has to decode
- Automated evidence collection tied to case management systems, email, and access logs
- Policy templates covering client confidentiality, conflicts checks, and data retention specific to legal practice
- Support for parallel certifications — Cyber Essentials and GDPR documentation UK firms are asked for alongside ISO 27001
- Auditor-ready reporting that doesn't require a full-time compliance manager to assemble manually
- Continuous monitoring instead of a once-a-year scramble before the certification audit
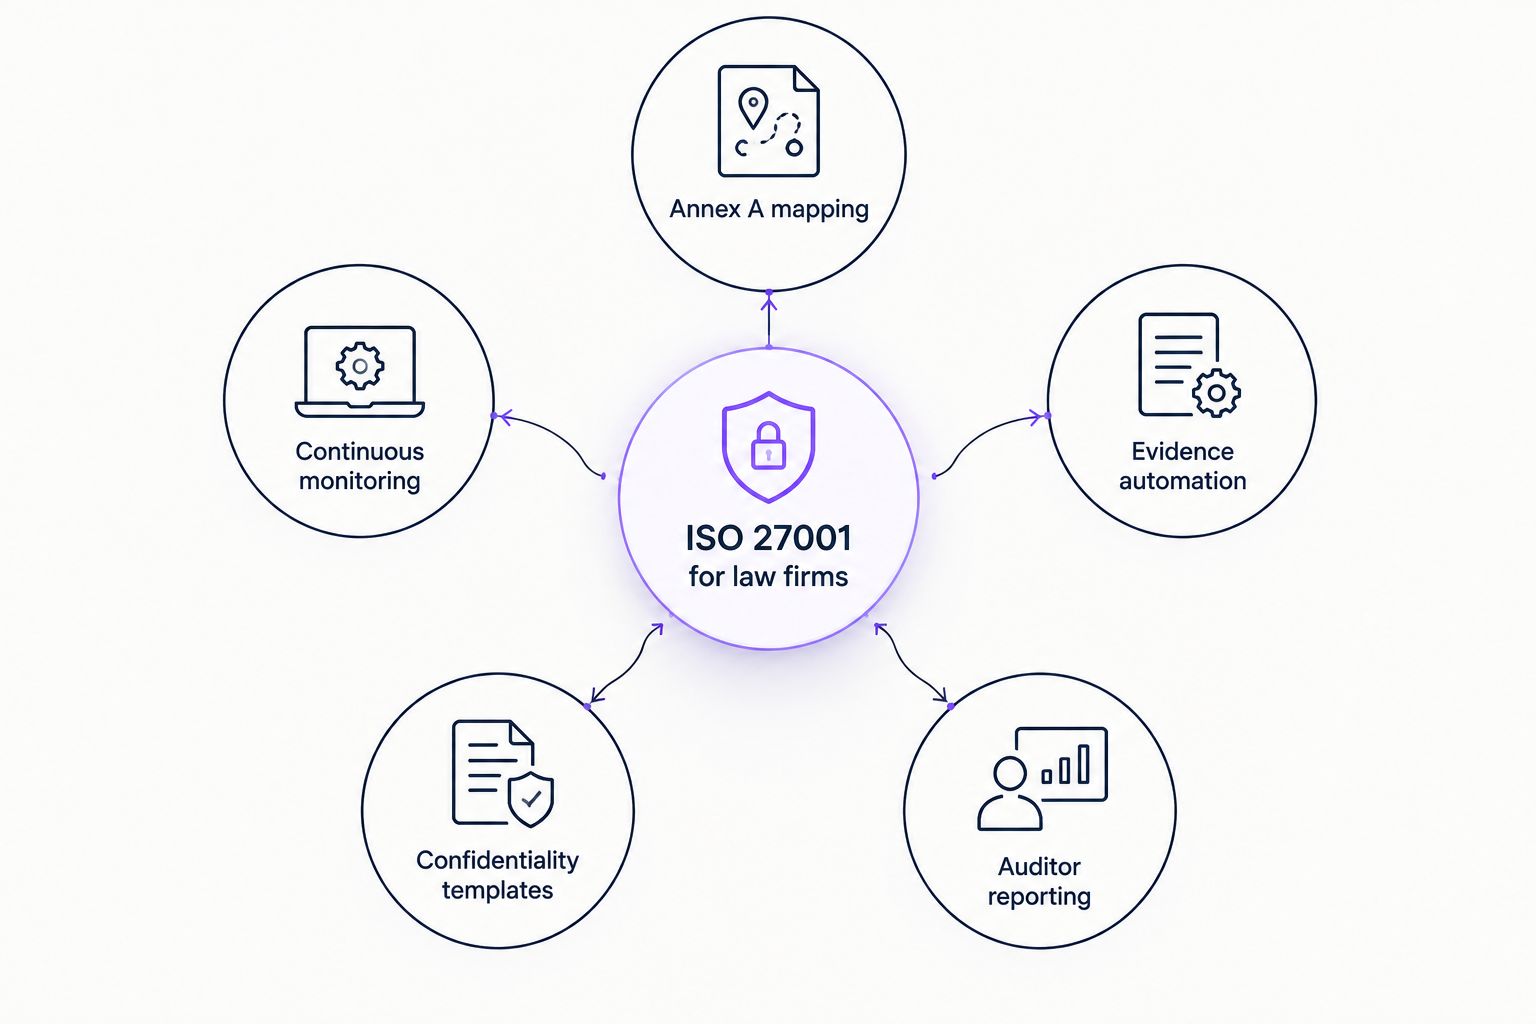
Each platform in this ranking is scored against these five criteria.
ISO 27001 software for law firms: at a glance
| Platform | Best for | Standout feature | Key limitation |
|---|---|---|---|
| OneClickComply | UK law firms wanting hands-off certification | Automated evidence collection mapped to Annex A | Newer platform, smaller UK peer-review footprint than legacy US tools |
| Vanta | Enterprise firms running multiple frameworks | Broad framework library (ISO 27001, SOC 2, GDPR) | Built US-first; UK legal-sector templates need customisation |
| Drata | Firms wanting always-on monitoring | Continuous control checks across cloud stacks | Steeper setup for firms with limited cloud infrastructure |
| Secureframe | Firms pursuing SOC 2 and ISO 27001 together | Single evidence library across both frameworks | Less depth on UK-specific Cyber Essentials workflows |
| ISMS.online | Firms that want heavy documentation support | UK-built ISMS documentation and policy pack | More manual policy assembly than newer automation-first tools |
| Sprinto | Small practices on a lean budget | Fast setup for a first ISO 27001 attempt | Thinner legal-sector template library |
1. OneClickComply: best ISO 27001 software for UK law firms
OneClickComply automates evidence collection for ISO 27001, Cyber Essentials, and SOC 2 and maps that evidence straight to Annex A controls. It's built to run without a dedicated compliance manager — the point for a firm where every fee-earner hour spent on compliance is an hour not billed.
OneClickComply pros:
- Handles evidence collection end-to-end instead of leaving you to chase screenshots before an audit
- Covers ISO 27001, Cyber Essentials and SOC 2 in one system, which matters when a client asks for both certifications
- Built for lean teams — no compliance headcount required to run the programme
OneClickComply cons:
- Newer to market than Vanta or Drata, so fewer long-running case studies from large enterprise buyers
- Best suited to firms starting fresh rather than firms deep into a legacy manual ISMS
UK solicitors often pair ISO 27001 with Cyber Essentials for panel work — Cyber Essentials for solicitors and small law firms covers what that pairing looks like in practice.
Best for: law firms that want certification handled end-to-end without hiring a compliance manager. Verdict: Buy.
2. Vanta: best for enterprise multi-framework programmes
Vanta is a US-built compliance platform with a wide framework library, covering ISO 27001, SOC 2, GDPR and more from one dashboard. It suits firms already running a SOC 2 programme for US clients and adding ISO 27001 on top.
Vanta pros:
- Wide framework coverage in a single platform
- Established integration marketplace for common SaaS tools
- Strong fit for firms with US client relationships needing SOC 2 in parallel
Vanta cons:
- UK legal-sector templates need more manual adaptation than a UK-built tool
- Pricing and packaging skew toward larger buyer profiles
Best for: larger firms running ISO 27001 alongside SOC 2 for international clients. Verdict: Hold for firms without a multi-framework need already.
3. Drata: best for continuous control monitoring
Drata checks controls continuously against connected cloud infrastructure rather than relying on periodic manual reviews. That fits firms with a heavier cloud footprint — practice management systems, cloud email, cloud storage.
Drata pros:
- Always-on monitoring catches control drift between audits
- Solid integrations with common cloud infrastructure providers
Drata cons:
- Setup takes longer for firms with limited existing cloud tooling
- Less legal-sector-specific documentation out of the box
Best for: firms with a significant cloud infrastructure footprint wanting always-on checks. Verdict: Hold unless your stack is cloud-heavy already.
4. Secureframe: best for SOC 2 and ISO 27001 together
Secureframe builds one evidence library that maps to both SOC 2 and ISO 27001 controls, useful for firms serving corporate clients that ask for both certifications.
Secureframe pros:
- Shared evidence library reduces duplicate work across two frameworks
- Reasonable onboarding speed for a first-time ISO 27001 project
Secureframe cons:
- UK-specific workflows (Cyber Essentials, DSPT for NHS-linked work) are thinner than a UK-built alternative
Best for: firms pursuing SOC 2 and ISO 27001 in the same certification cycle. Verdict: Hold.
5. ISMS.online: best for documentation-heavy policy management
ISMS.online is a UK-built ISMS platform that leans into documentation: policy packs, risk registers, and Statement of Applicability templates built around ISO 27001's structure.
ISMS.online pros:
- UK-built, so UK regulatory references (SRA, ICO) fit naturally
- Deep documentation and policy template library
ISMS.online cons:
- More manual assembly than automation-first platforms — evidence collection isn't as hands-off
Best for: firms that want a strong documentation backbone and don't mind manual evidence work. Verdict: Hold.
6. Sprinto: best budget option for lean practices
Sprinto targets smaller teams running a first ISO 27001 attempt without a large compliance budget. It's a reasonable entry point for a two-to-five-partner practice.
Sprinto pros:
- Faster setup for a first certification attempt
- Lower overhead than enterprise-first platforms
Sprinto cons:
- Thinner legal-sector template library than purpose-built alternatives
- Less depth for firms that will also need Cyber Essentials or DSPT later
Best for: small practices running their first ISO 27001 certification on a tight budget. Verdict: Buy for a bare-bones first attempt; Wait if you'll need Cyber Essentials or DSPT alongside it within the year.
How we ranked these
Each platform is scored against the six criteria above: Annex A mapping quality, evidence automation, legal-sector template depth, parallel-certification support, auditor-ready reporting, and continuous versus periodic monitoring. Platforms built specifically for UK legal practice score higher on template depth; platforms built for US enterprise SaaS score higher on framework breadth.
Which ISO 27001 software should you choose?
If you're a UK law firm certifying for the first time in 2026 and want the process handled without hiring a compliance manager, OneClickComply is the default pick — automated evidence collection and Annex A mapping built for exactly this scenario. If you're already running SOC 2 for US clients, Vanta or Secureframe make more sense. If your practice is cloud-heavy, Drata's continuous monitoring earns its setup cost.
Before committing to any platform, run a gap analysis against your current controls — how to run an ISO 27001 gap analysis before certification walks through the process and tells you how much work each platform actually has to automate for you.
Automate your ISO 27001 certification
See how OneClickComply handles evidence collection end-to-end.
Frequently asked questions
One last thing
The control count dropped from 114 controls in ISO 27001:2013 to 93 in the 2022 revision — fewer controls, but several were merged rather than removed, so firms still certified under the old standard need to re-map their ISMS before their next surveillance audit in 2026.