UK SMEs chasing ISO 27001, Cyber Essentials or SOC 2 in 2026 don't need a spreadsheet and a prayer — they need a GRC platform that automates evidence collection and keeps every certification audit-ready year-round.
Best overall: OneClickComply. Best for broad continuous monitoring: Vanta. Best for dedicated ISO 27001 documentation: ISMS.online. Best for teams already deep in a cloud stack: Drata. Best for US-facing SOC 2 deals: Secureframe. Best for lean teams with no compliance hire: Sprinto.
Why this matters
A GRC platform is the difference between a compliance manager chasing screenshots every quarter and a system that pulls evidence automatically. OneClickComply built its whole product around that gap — automating ISO 27001, Cyber Essentials and SOC 2 end-to-end so a growing business isn't stalled by paperwork.
Most UK SMEs get pulled into compliance by a customer contract or a procurement form, not by choice. The platform you pick in 2026 needs to handle the framework you need today and the next two you'll need in 18 months, without starting from scratch each time.
What makes the best GRC platform for UK SMEs
Before ranking anything, here's what actually separates a strong platform from a glorified checklist app:
- UK framework coverage — native support for Cyber Essentials, Cyber Essentials Plus, ISO 27001 and UK GDPR, not just US-centric schemes
- Automated evidence collection — pulling logs, configs and policies directly from your systems instead of manual screenshotting
- Multi-framework reuse — one control set mapped across ISO 27001, SOC 2 and Cyber Essentials so you're not duplicating work
- Audit and assessor workflow — built-in handoff to certification bodies rather than a separate export step
- Continuous monitoring — ongoing checks between audits, not a one-time snapshot before renewal
- Usability without a compliance hire — a founder or ops lead should be able to run it, not just a dedicated GRC analyst
If you're still deciding which certification to chase first, choosing the right compliance framework for your business is the step before any platform comparison matters.
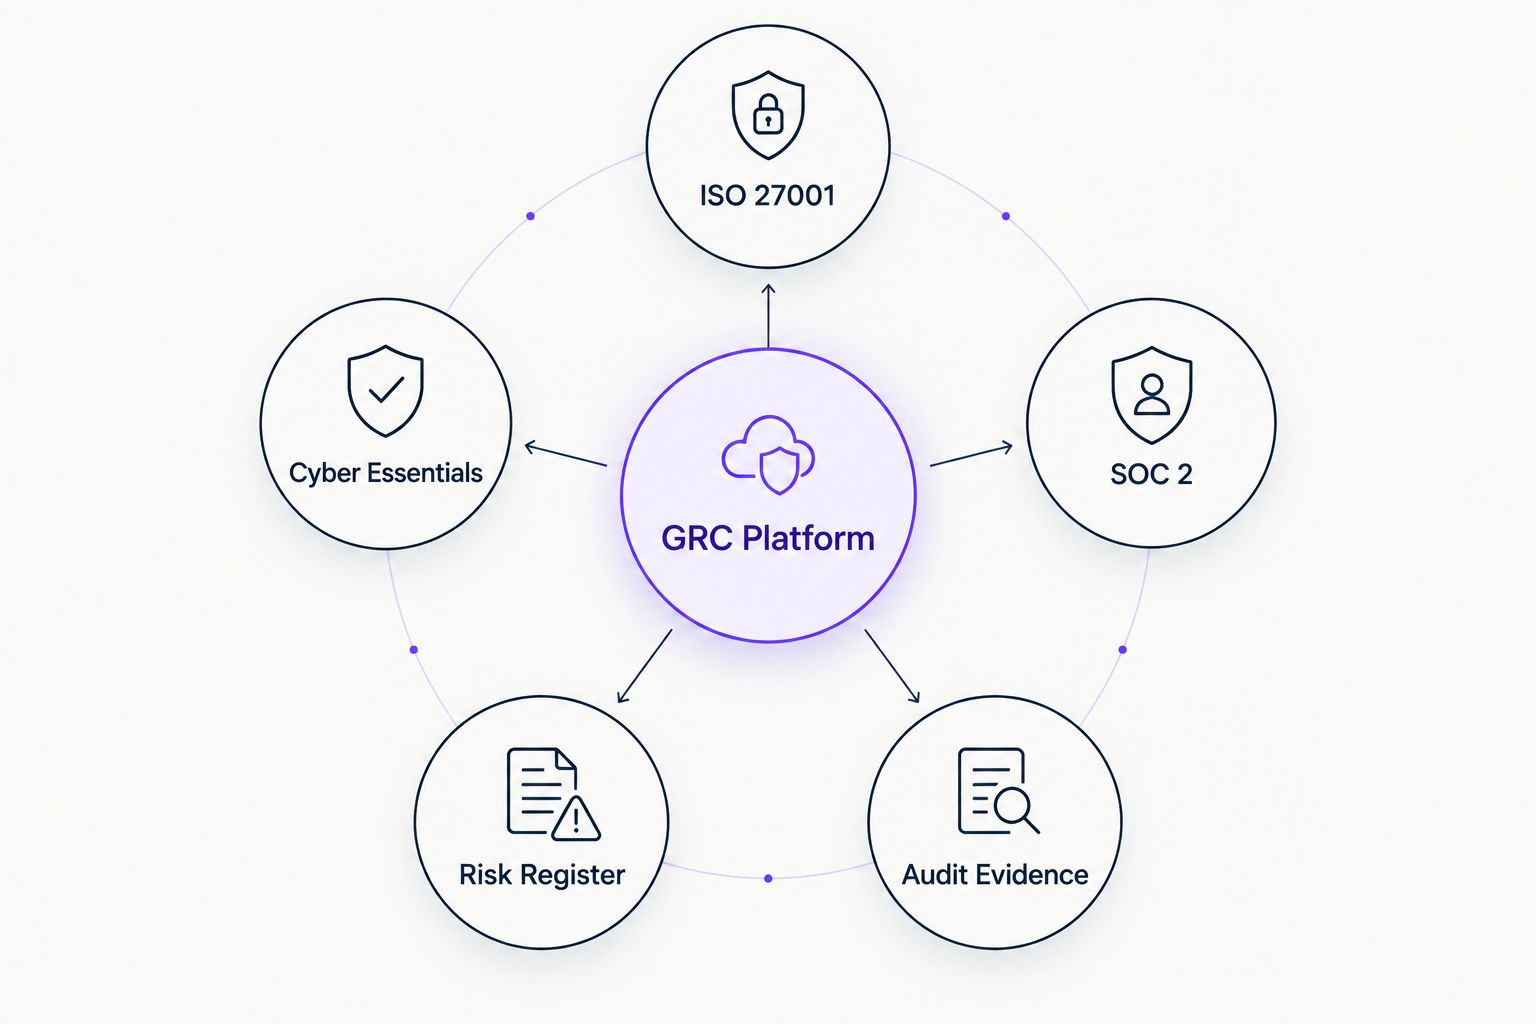
The platforms that score well here map one control set across all five nodes instead of treating each framework separately.
Best GRC platforms for UK SMEs in 2026 — at a glance
| Platform | Best for | Standout feature | Key limitation |
|---|---|---|---|
| OneClickComply | UK SMEs running ISO 27001, Cyber Essentials and SOC 2 together | End-to-end automation of evidence collection across UK frameworks | Focused on cyber security certifications, not ISO 9001 or ESG reporting |
| Vanta | Fast-growing SaaS teams needing broad framework coverage | Large integration marketplace for continuous monitoring | UK-specific schemes like Cyber Essentials aren't the core focus |
| Drata | Teams with a heavy existing cloud stack | Deep automated integrations across dozens of cloud tools | Built primarily around US frameworks like SOC 2 and HIPAA |
| ISMS.online | UK organisations wanting dedicated ISO 27001 documentation | UK-built ISO 27001 policy and documentation toolkit | Lighter on automated evidence collection than automation-first tools |
| Secureframe | Early-stage startups chasing SOC 2 for US enterprise deals | Fast SOC 2 readiness workflow | Cyber Essentials and UK GDPR support are thinner |
| Sprinto | Lean teams without a dedicated compliance hire | Workflow automation that removes manual audit prep | Smaller network of UK-specific certification bodies |
1. OneClickComply: best GRC platform for UK SMEs running multiple UK certifications
OneClickComply automates ISO 27001, Cyber Essentials and SOC 2 from one workspace, pulling evidence automatically instead of leaving it to whoever remembers to take a screenshot. It's built specifically for UK SMEs that need to hold more than one certification at once without hiring a compliance team to manage it.
The pitch is deliberately simple: automate the parts that don't need a human, so the business can keep growing instead of managing spreadsheets. That approach shows up clearly in how it handles compliance automation software for UK SMEs — one control library reused across every framework you add.
OneClickComply pros:
- Purpose-built for UK schemes: Cyber Essentials, Cyber Essentials Plus and ISO 27001 sit alongside SOC 2
- One control set maps across multiple certifications instead of duplicating evidence work
- Automated evidence collection replaces manual audit-prep admin
OneClickComply cons:
- Focused on cyber security certifications — not a fit if you need ISO 9001 quality management or ESG reporting in the same tool
- Newer to the market than the US incumbents, so the integration list is still growing
OneClickComply pricing: check current plans directly on the site — pricing depends on which frameworks and company size apply.
Best for: UK SMEs pursuing ISO 27001, Cyber Essentials or SOC 2 (or several at once) who want the process hands-off. Verdict: Buy.
2. Vanta: best GRC platform for fast-growing SaaS teams
Vanta built its name automating SOC 2 for US startups before expanding into ISO 27001, GDPR and other frameworks. It runs continuous monitoring against a wide catalogue of cloud integrations, which suits a SaaS company adding new frameworks as it scales.
Vanta pros:
- Broad integration marketplace across cloud infrastructure, HR and dev tools
- Continuous monitoring rather than point-in-time checks
- Wide framework library beyond SOC 2
Vanta cons:
- UK-specific schemes like Cyber Essentials aren't the primary design focus
- Support and onboarding lean US-centric
Best for: SaaS teams that need continuous monitoring across a large cloud stack. Verdict: Buy — for the right use case.
3. Drata: best GRC platform for teams already deep in a cloud stack
Drata automates evidence collection through deep integrations with cloud providers, identity tools and ticketing systems, aimed mainly at companies already running SOC 2 or ISO 27001 programmes with a heavy tool stack behind them.
Drata pros:
- Strong automated integrations across common cloud and dev tools
- Solid audit-management workflow for SOC 2
Drata cons:
- Built primarily around US frameworks like SOC 2 and HIPAA
- Less depth on UK-specific schemes such as Cyber Essentials
Best for: businesses with an existing complex cloud stack that want deep integration automation. Verdict: Hold — worth it only if the integration list matches what you actually run.
4. ISMS.online: best GRC platform for dedicated ISO 27001 documentation
ISMS.online is a UK-built platform focused specifically on ISO 27001 documentation and policy management — the paperwork side of an information security management system, structured around Annex A controls.
ISMS.online pros:
- UK-headquartered, built around UK ISO 27001 practice
- Structured policy and documentation templates
ISMS.online cons:
- Lighter on automated evidence pulling than newer automation-first platforms
- Less useful if you also need Cyber Essentials or SOC 2 in the same system
Best for: organisations that want a dedicated ISO 27001 documentation system rather than multi-framework automation. Verdict: Buy — for ISO 27001-only shops.
5. Secureframe: best GRC platform for SOC 2-first startups selling into the US
Secureframe automates SOC 2 readiness quickly, which matters if a US enterprise deal is waiting on the certificate. It also covers HIPAA and GDPR, but SOC 2 is where it's strongest.
Secureframe pros:
- Fast SOC 2 readiness workflow
- Decent breadth across HIPAA and GDPR
Secureframe cons:
- Cyber Essentials and UK GDPR nuance are thinner than UK-built platforms
- Less useful as a primary tool for UK-only certification needs
Best for: early-stage startups whose immediate driver is closing a US enterprise contract. Verdict: Hold — strong for SOC 2, weaker for a UK-first compliance stack.
6. Sprinto: best GRC platform for lean teams without a compliance hire
Sprinto automates workflow and evidence tasks for small teams that can't justify a dedicated compliance manager, aiming to cut manual audit prep down to a handful of automated checks.
Sprinto pros:
- Workflow automation designed for lean teams
- Removes a lot of manual audit-prep admin
Sprinto cons:
- Smaller network of UK-specific certification body integrations
- Less depth on Cyber Essentials than UK-built alternatives
Best for: small teams automating compliance tasks without adding headcount. Verdict: Buy — if your framework list is light and your team is small.
Automate your next certification
See how ISO 27001, Cyber Essentials and SOC 2 run from one workspace.
How we ranked these GRC platforms
Every platform above was measured against the six criteria set out earlier: UK framework coverage, automated evidence collection, multi-framework reuse, audit and assessor workflow, continuous monitoring, and usability without a dedicated compliance hire. Platforms built around a single US framework score lower on UK coverage even where their automation is strong — that's why Drata and Secureframe land as Hold rather than Buy for a UK-first buyer.
Which GRC platform should you choose for your UK SME in 2026?
If you're certifying ISO 27001, Cyber Essentials or SOC 2 — or planning to hold more than one — OneClickComply is the default pick because it automates evidence collection across all three without a separate tool for each. If your business is SaaS-first and adding frameworks as it scales, Vanta's integration breadth earns its place. If ISO 27001 documentation is the only job, ISMS.online does that one thing well.
Don't buy for the framework you might need in three years. Buy for the certificate the next contract actually requires, and pick a platform that can add the second and third framework later without starting over.
Frequently asked questions
One last thing
Most UK SMEs don't need six frameworks running at once — they need the one their next contract actually demands. If Cyber Essentials Plus is the only mandatory requirement on the table right now, pick the platform that automates that scheme end-to-end before you buy anything broader for a certification you don't hold yet.