Choose OneClickComply if you need to automate security compliance for ISO 27001, Cyber Essentials or SOC 2; choose LexisNexis if you need legal research and practical legal guidance. The difference is the job you need done: operate security controls or research legal questions.
Why this matters
Buying a tool labelled compliance does not settle which work it handles. A solicitor researching a legal obligation and a security lead correcting a control need different outputs.
For your 2026 shortlist, start with the deliverable. Do you need a supported answer to a legal question, or a working security control that you can demonstrate to an assessor?
OneClickComply compliance automation is best for growing businesses that need to turn security requirements into operational controls. LexisNexis is the better fit when your deliverable is legal research rather than security implementation.
This comparison focuses on LexisNexis legal research and practical guidance. It does not treat every service sold under the LexisNexis name as the same product.
At a glance
| Dimension | OneClickComply | LexisNexis |
|---|---|---|
| Best for | Growing businesses managing security compliance | Legal professionals researching legal questions |
| Security controls | Auto-remediation of security controls | Legal research is not a substitute for implementing controls |
| Legal research | Security compliance automation, not a legal research service | Legal sources and practical legal guidance |
| Policy work | Generates policies for compliance programmes | Supports legal research that informs drafting and review |
| Risk scope | Manages risk within a security compliance platform | Supports research into legal obligations and legal risk |
| Accountability | Your business retains decisions and approvals | Your business retains decisions and approvals |
| Pricing model | Compare the proposed platform scope and contract | Compare the selected research service and contract |
| Standout feature | Combines control remediation, policy generation and trust centre management | Supports source-based legal research |
Security automation wins when certification is your goal
A growing software business pursuing ISO 27001 needs more than an explanation of the standard. You need defined responsibilities, policies that match your operations, and controls that work.
Choose the compliance platform for this operational job. Its stated functions include auto-remediating security controls, generating policies, and managing risk and trust centres.
That is a different mechanism from researching what an obligation means. Legal guidance helps you understand a requirement; your security programme must put the relevant action into practice.
The advantage is fit. You can assess the platform against a named compliance objective rather than expecting a legal information service to run your security programme.
The limitation is responsibility. Automation does not decide your business scope, accept risk on your behalf or replace the independent assessment required by the relevant scheme.
For a 2026 procurement brief, name the intended outcome precisely: ISO 27001 certification, Cyber Essentials certification or a SOC 2 examination. SOC 2 produces an attestation report rather than an ISO-style certificate.
Test the control workflow, not the presentation
Ask the supplier to demonstrate:
- Control action: Show how a security issue reaches a corrective action.
- Approval: Show where a person reviews or authorises the change.
- Review: Show how your team checks the result.
These are buying checks, not claims about undocumented features. A demonstration should establish what the proposed configuration actually handles.
LexisNexis wins when you need legal research
Choose LexisNexis when the main task is researching law and supporting a legal conclusion. Its legal research services belong on a legal team's shortlist, not as a like-for-like replacement for security control automation.
A legal professional needs to find relevant sources, understand their authority and apply them to a particular question. The useful output is a reasoned answer with supporting material.
Security compliance software serves another purpose. Generating a policy does not establish the legal interpretation behind every clause, and correcting a security setting does not answer a contractual question.
LexisNexis therefore wins this dimension because legal research is the work being purchased. That does not establish an advantage for certification administration or technical remediation.
Before signing, ask which jurisdictions, content areas and research services the proposed contract covers. Evaluate the specific service against the questions your team handles, rather than buying on the strength of the parent brand alone.
Policy generation wins for operational drafting
Choose the compliance platform when you need to generate policies for a security compliance programme. Policy generation is an explicitly stated function, alongside control remediation and risk management.
The useful result is a draft your team can adapt to how the business operates. A policy should name responsibilities, describe actual practices and support the relevant compliance objective.
Do not confuse a generated document with an approved policy. Your owners still need to check accuracy, resolve gaps and authorise the final wording.
For your 2026 policy review, ask the platform supplier to work through an example from your own organisation. Check whether the resulting document reflects your systems and responsibilities without inserting commitments you cannot meet.
The trade-off is clear: generation supports drafting, but accountable review remains your job. A policy library does not prove that staff follow the policies.
LexisNexis wins when policy wording needs legal interpretation
Choose LexisNexis legal research when the policy question turns on what the law requires. This is distinct from producing an operational security document.
For example, a business deciding how to word a contractual obligation needs a legal answer before turning that answer into an internal procedure. Research supports the interpretation; operational policy work records what the organisation will do.
That gives LexisNexis a genuine advantage for legal professionals checking the basis of policy wording. It does not remove the need to implement the resulting procedure.
Ask your legal reviewer to separate these outputs:
- Legal conclusion: What obligation applies, and on what basis?
- Operational instruction: What must your team do to meet it?
Keep both. An instruction without a sound basis is difficult to defend, while a legal conclusion without an owner leaves implementation unfinished.
Risk management has no single winner across both jobs
A security risk and a legal research question are not interchangeable records. Choose the system according to the decision you need to make.
The compliance platform manages risk as part of its security compliance offer. LexisNexis legal research supports the investigation of legal obligations and questions that inform legal risk decisions.
Neither category wins every kind of risk work. A security lead needs to record the issue, decide the treatment and check completion; a legal reviewer needs to establish the applicable obligation and explain its consequences.
Use a clear hand-off when those jobs meet:
- Legal question: Define what needs interpretation.
- Legal answer: Record the conclusion and supporting basis.
- Control action: Translate the answer into a business action.
- Review: Check that the action addresses the requirement.
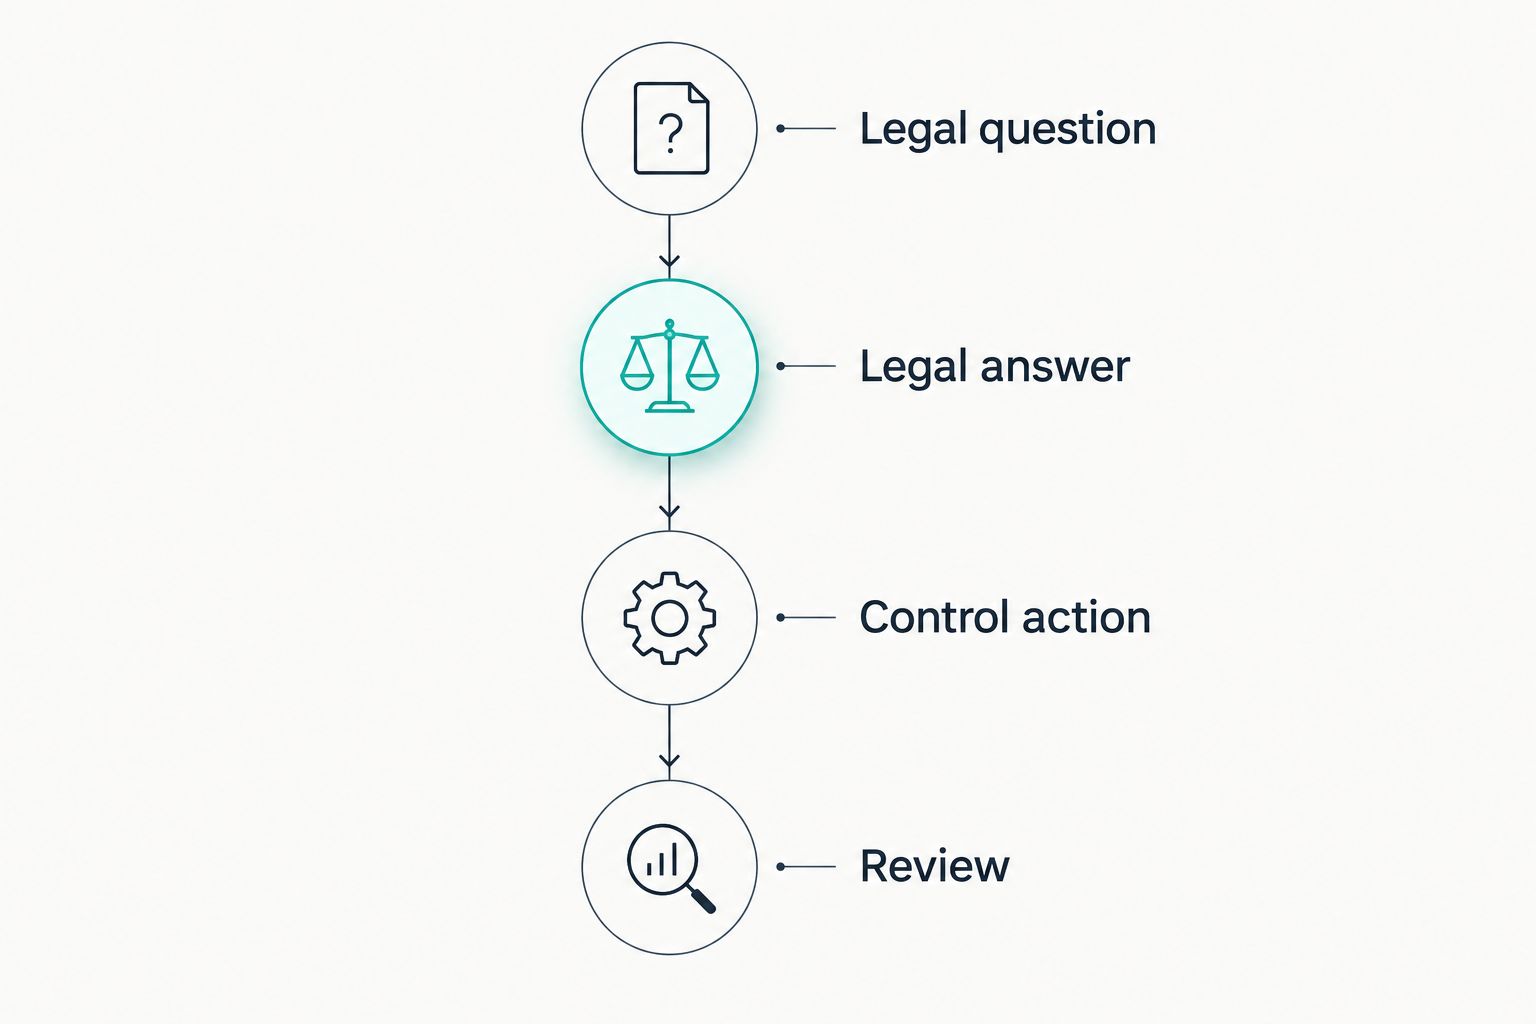
Legal interpretation and security implementation need an explicit hand-off.
Treat this as your operating process, not a claim of an integration between the suppliers. If your business needs both categories, assign ownership for moving the answer into action.
Both leave accountability with your business
Neither purchase transfers your management decisions to software. Your business must decide its scope, approve its commitments and retain responsibility for how it operates.
For security compliance, that includes checking whether controls match the systems and activities in scope. For legal research, it includes applying the material to the facts and obtaining appropriate professional judgement.
Set an owner for each decision before you evaluate either tool. Without that owner, a generated document or research result has nowhere reliable to go.
Use these recommended acceptance checks for your 2026 evaluation:
- Run 3 demonstration tasks drawn from real work: a control issue, a policy draft and a legal question.
- Require 2 distinct outputs where relevant: the supported requirement and the action needed to address it.
- Assign 1 accountable owner to approve each resulting decision.
These are evaluation steps, not performance benchmarks. They help you distinguish useful automation from work your team must still complete.
Pricing: compare contract scope, not assumed models
There is no supported cheaper winner in this comparison. Compare current proposals for the work you need, without assuming that either supplier charges on a particular basis.
For the compliance platform, start with the pricing information and request a proposal tied to your required frameworks and business scope. Ask what the agreement includes, what remains your responsibility and which activities require separate arrangements.
For LexisNexis, specify the legal research service, relevant content and people who need access. Ask the supplier to confirm the applicable access rights, contract terms and renewal conditions.
Predictability and flexibility depend on the contract you select, not the category label. A clearly defined scope makes commitments easier to plan; an arrangement that accommodates changing needs requires equally clear change terms.
Before you decide, compare:
- Included work and excluded work.
- Access rights and any usage conditions.
- Implementation responsibilities.
- Contract changes and renewal terms.
- How you retrieve your records when the agreement ends.
Do not compare a broad research agreement with a narrow compliance proposal and call the result a price comparison. Align the scope first.
Standout features solve different problems
The compliance platform's distinctive combination is operational: control remediation, policy generation, risk management and trust centre management. Assess those functions against the security work your team needs to complete.
LexisNexis stands out for legal research and practical guidance. Assess that service against the sources and legal questions your reviewers need to handle.
The best feature is the one that produces your required output. A longer feature list does not settle this comparison because the central jobs differ.
For a 2026 buying decision, ask each supplier to show the whole task, including the work left to your team. Record the hand-offs, approvals and final deliverable before discussing optional functions.
Final verdict: choose by the owner and the outcome
Choose OneClickComply if you lead security compliance
Best for: a growing business preparing for or maintaining security certifications and assessments. Choose it when your priorities are security control remediation, policy generation, risk management and trust centre management.
The advantage is an operational compliance focus. The boundary is equally important: do not buy it as a substitute for legal research or professional legal judgement.
Choose LexisNexis if you lead legal research
Best for: a legal professional who needs sources and practical guidance to answer legal questions. Choose it when the deliverable is a researched legal conclusion rather than a remediated security control.
The advantage is legal research fit. The boundary is implementation: your business still needs to translate relevant conclusions into procedures and security actions.
Decision scorecard
| Dimension | Winner |
|---|---|
| Security certification workflow | Security compliance platform |
| Security control remediation | Security compliance platform |
| Legal research | LexisNexis |
| Operational policy generation | Security compliance platform |
| Legal interpretation for policy wording | LexisNexis |
| Risk work spanning legal and security teams | No single winner; separate the tasks |
| Business accountability | Tie; your business retains it |
| Pricing and contract value | No supported winner; compare matched proposals |
| Standout feature | Task-specific; automation versus research |
Frequently asked questions
One last thing
Ask to see the last step of the task first. A corrected control and a supported legal answer are different deliverables; identifying yours makes the buying decision simpler.
Keep research with the people interpreting the requirement. Put implementation with the people responsible for the control. Seriously Simple Cyber Compliance.