Yes, NIS2 can apply to UK companies after Brexit when they operate an in-scope EU establishment or provide certain covered digital services into the EU without an EU establishment. A UK registered office does not settle the question, and customer security requirements can still affect your business even when direct regulatory duties do not.
Why this matters
Separate legal duties from customer requirements before you build your compliance plan. A regulator's reporting deadline and a customer's notification clause are different obligations, even when they concern the same incident.
For your 2026 assessment, identify the legal entity, the service it provides and the relevant EU country first. Then use the practical steps in preparing for NIS2 as a UK supplier to organise the work that follows.
Does NIS2 apply to UK companies after Brexit?
Yes, but not simply because a UK company trades with Europe. NIS2's scope and jurisdiction rules distinguish EU-established entities, certain digital providers outside the EU, and suppliers whose obligations arise through contracts.
For a 2026 assessment, the central provisions are NIS2 Article 2 on scope, Annexes I and II on covered activities, and Article 26 on jurisdiction. Apply these alongside the relevant member state's implementing law.
| Your position | Direct NIS2 position | What you should do |
|---|---|---|
| UK-only business with no relevant EU activity | UK incorporation alone does not create NIS2 duties | Check UK requirements separately |
| UK-owned EU subsidiary carrying out a covered activity | The EU entity needs its own scope assessment | Check activity, size, exceptions and national law |
| UK cloud provider serving EU customers without an EU establishment | Special non-EU provider rules can bring the provider into scope | Assess Article 26 and the representative requirement |
| UK supplier to an in-scope EU customer | The customer relationship alone does not establish direct scope | Review security, evidence and incident clauses |
| UK business selling ordinary goods into the EU | Sales alone do not establish direct NIS2 scope | Check establishments and actual activities, not customer location alone |
These routes can overlap. A group can have a regulated EU subsidiary, a UK service provider needing a separate assessment, and supply contracts imposing additional security duties.
What did Brexit change?
NIS2 does not apply across the UK as domestic law merely because it is an EU directive. The UK's Network and Information Systems Regulations remain a separate legal framework.
However, being outside the EU does not remove the specific rules for covered non-EU digital providers. Brexit is not a blanket exemption from NIS2's reach.
UK companies with an EU establishment
Assess the entity carrying out the covered activity. An EU subsidiary does not automatically put its UK parent under the same direct duties, but shared systems and group services need attention when defining the subsidiary's security arrangements.
Covered sectors include energy, transport, health, digital infrastructure and specified manufacturing activities. A sector label is only the starting point: the activity must match the directive and the relevant national legislation.
The general scope rule covers medium-sized and larger entities in listed sectors. Exceptions bring certain entities into scope regardless of size, and linked or partner enterprises can affect the size calculation.
Do not assess a small EU subsidiary using its local headcount alone. Record the ownership structure, relevant group relationships and the basis for the size assessment.
UK digital providers serving the EU without an establishment
Certain digital providers face a different jurisdiction test. Article 26 covers categories including cloud computing, data centres, content delivery networks, managed services and managed security services.
It also covers specified internet infrastructure and online platform providers. Do not assume that every software subscription is a cloud computing service for this purpose; assess the actual service against the legal definition.
A covered provider without an EU establishment that offers services within the EU must designate a representative in an EU member state where it offers those services. The representative requirement does not replace the provider's own obligations.
For your 2026 review, record:
- The precise service category and why it fits.
- Evidence that you offer the service within the EU.
- Whether you have an EU establishment.
- The relevant jurisdiction and representative arrangements.
- The applicable size rule or exception.
A website accessible from the EU is not, by itself, enough to establish that you offer services there. Assess the evidence of intended EU service provision rather than treating internet access as the test.
UK suppliers with contractual security requirements
You do not become directly regulated under NIS2 solely because an EU customer is in scope. However, NIS2 requires covered entities to address supply-chain security, including security-related aspects of relationships with direct suppliers and service providers.
That creates a separate commercial question: what has your customer required you to do? Read the contract and security schedule before answering a questionnaire or accepting a compliance statement.
Typical subjects to examine include:
- Access controls and privileged accounts.
- Vulnerability handling and security updates.
- Incident notification and cooperation.
- Business continuity and recovery evidence.
- Subcontractor controls and assurance rights.
Do not describe a contractual requirement as a statutory duty. Equally, do not ignore an agreed contractual duty because your business falls outside direct NIS2 scope.
Why NIS2 applicability varies
Your registered address is only one part of the assessment. These factors determine which route you need to examine:
- Activity: Your actual service or operation must match a covered category.
- Size: The general size rule has exceptions, and group relationships affect the calculation.
- Establishment: EU establishments and non-EU providers face different jurisdiction rules.
- Service location: Certain digital providers fall within the framework when offering covered services in the EU.
- National law: Member states implement the directive through domestic legislation, so local provisions matter.
- Contracts: Customers can impose security duties without making you directly regulated.
Keep the conclusion specific. “Our UK company is exempt” is less useful than a written assessment identifying the entity, service, countries and legal basis considered.
How do you check whether your UK company is in scope?
Use a documented sequence rather than starting with a control checklist. Revisit the assessment when you launch a service, enter an EU market or change your group structure.
- Map entities. List the legal entities delivering services, their establishments and their ownership relationships.
- Classify services. Match actual activities to the covered categories, including any relevant digital-provider definitions.
- Check size. Apply the size rules, group calculations and exceptions to the correct entity.
- Identify jurisdiction. Determine which national rules and authorities are relevant, including any representative requirement.
- Record duties. Separate direct legal obligations from customer clauses and assign an owner to each.
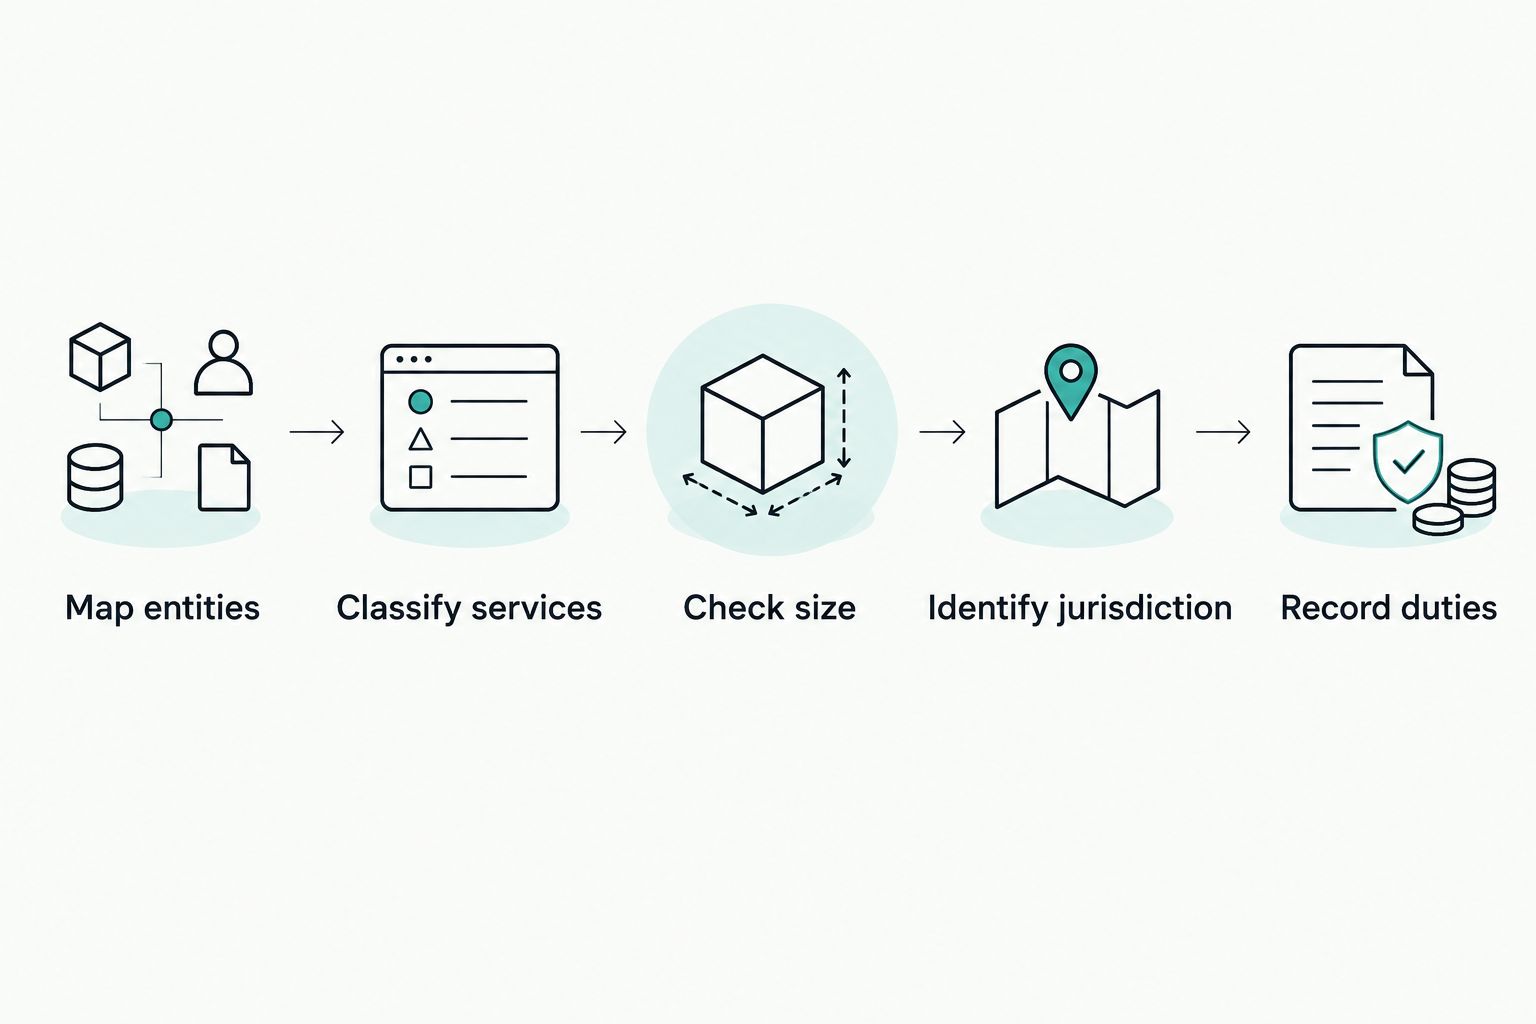
Establish scope before choosing controls or making compliance claims.
Keep the supporting documents with the conclusion. Include your service description, organisation chart, size calculation, relevant contract extracts and the national rules used.
For a 2026 scope record, name the decision owner and review trigger. A conclusion without those details becomes difficult to maintain when the business changes.
What should you prepare if NIS2 applies?
Start with the obligations, then map existing controls against them. NIS2 Article 21 addresses cyber security risk-management measures; Article 20 addresses management approval and oversight.
Assign management ownership
Identify who approves the security measures and who checks their implementation. Management training and oversight are part of the framework, not tasks to leave entirely with an external IT provider.
Keep decisions and actions together. A policy approval without evidence of implementation does not show that the control operates.
Assess risk against the actual service
A cybersecurity risk assessment needs a defined service boundary: assets, dependencies and failure scenarios determine which security measures your business must examine. For a UK provider serving EU customers, include shared infrastructure and the suppliers supporting that service.
Do not treat a generic risk register as the finished assessment. Link each material risk to an owner, a treatment decision and evidence that the chosen action happened.
Prepare incident reporting
Under NIS2 Article 23, the general reporting sequence for significant incidents includes an early warning within 24 hours, an incident notification within 72 hours, and a final report within one month after the incident notification. These clocks run from awareness of a significant incident; specific rules and exceptions require attention.
The 72-hour notification is not permission to wait before acting. Establish escalation, evidence preservation and decision ownership before an incident occurs.
For your 2026 incident procedure, distinguish regulatory reports from customer notifications. A contract can require earlier notice, and a personal data breach can trigger separate data protection duties.
Keep evidence of operational controls
NIS2's risk-management subjects include incident handling, continuity, supply-chain security, vulnerability handling, access security and assessing the effectiveness of measures. Build evidence around what your service actually does.
Useful records include access reviews, recovery test results, supplier assessments and remediation decisions. A document describing a control is different from evidence that the control worked.
Does ISO 27001 make you NIS2 compliant?
No. ISO 27001 certification does not automatically establish NIS2 compliance. It can support your security management and evidence, but it does not settle legal scope, jurisdiction or national reporting duties.
Use existing work rather than rebuilding everything. Match each applicable legal requirement to a control, an owner and evidence, then identify gaps.
| Approach | Best for | Strength | Limitation |
|---|---|---|---|
| ISO 27001 programme | Managing information security systematically | Provides a structured management system and supporting evidence | Certification scope does not automatically match NIS2 obligations |
| NIS2 legal assessment | Determining regulatory duties | Establishes the entity, jurisdiction and applicable requirements | Does not implement security controls |
| Compliance automation | Managing repeatable compliance work | Supports policy, risk and control tasks | Does not replace legal interpretation or management accountability |
OneClickComply is best for growing businesses that want to automate compliance work across ISO 27001, Cyber Essentials and SOC 2. Its compliance automation platform generates policies, manages risk and auto-remediates security controls.
OneClickComply supports those operational tasks; it does not establish your NIS2 scope merely by being part of your compliance programme. Use OneClickComply for the supported work and keep the legal assessment explicit.
Can you tell customers that you are NIS2 compliant?
Make claims against a defined scope and a documented basis. Avoid treating NIS2 as a single certification badge equivalent to an ISO 27001 certificate.
Before making a statement, identify:
- The legal entity and service covered.
- The national legislation assessed.
- The controls and evidence supporting the statement.
- Any open actions and the person authorised to approve the wording.
If you are outside direct scope, answer the customer's actual security questions instead. A precise explanation of your controls is more useful than an unsupported declaration of compliance.
Frequently asked questions
One last thing
Your EU representative and your incident-response owner perform different roles. Appointing a representative does not replace internal responsibility for detecting incidents, making decisions or maintaining evidence.
Write the scope decision before you buy controls or promise compliance. Then automate the repeatable work. Seriously Simple Cyber Compliance.