No. You cannot get Cyber Essentials Plus without Cyber Essentials: you must first pass the basic assessment, then complete the Plus audit within 3 months of that certification. You can arrange both as one programme, but a combined booking does not remove the basic certification requirement.
Can you get Cyber Essentials Plus without basic Cyber Essentials?
No. Basic Cyber Essentials is a prerequisite, not an optional alternative to the Plus audit. IASME, the Cyber Essentials delivery partner, sets out this sequence in its scheme guidance: achieve Cyber Essentials first, then complete Plus within the permitted 3-month window.
The two levels assess the same five technical control areas. The difference is how you demonstrate that those controls work.
| Requirement | Cyber Essentials | Cyber Essentials Plus |
|---|---|---|
| Assessment method | Self-assessment questionnaire reviewed by an assessor | Independent technical audit of the controls |
| Basic certificate needed beforehand | No | Yes |
| Technical control areas | The same five areas | The same five areas |
| Main benefit | Establishes a verified baseline through assessed answers | Adds technical verification of implementation |
| Main limitation | Does not include the Plus technical audit | Requires basic certification and additional assessment work |
| Best for | Businesses whose customer requirements accept basic certification | Businesses whose customers require Plus or that want independent technical assurance |
For the practical work behind the second stage, use the guide to preparing for a Cyber Essentials Plus audit.
Why this matters
If you need Plus for a customer deadline in 2026, plan backwards from the required certificate date. Do not treat the basic questionnaire as paperwork you can complete after the technical audit.
Keep the distinction clear when speaking to suppliers. You can prepare for both levels together, but you still need to pass them in the correct order.
That changes your next move: establish the scope, check your controls and agree the assessment sequence before committing to an audit date.
Cyber Essentials: the prerequisite assessment
Cyber Essentials uses an assessed self-assessment questionnaire. You describe your organisation's scope and explain how your systems meet the scheme's requirements; an assessor reviews those answers.
Self-assessment does not mean self-issued certification. Your organisation supplies the answers, but an authorised certification body assesses the submission.
Prepare answers that match your actual environment. A written policy saying that software stays updated is not the same as knowing which devices run unsupported software.
Before submission, make sure you can explain:
- Which organisation or defined part of it you are certifying.
- Which devices, services and networks fall within that scope.
- Who manages the relevant technical settings.
- How your controls meet the applicable requirements.
- Who has checked and approved the answers.
Basic certification is useful when it meets the requirement you are trying to satisfy. Its limitation is specific: it does not provide the independent technical verification included in Plus.
Cyber Essentials Plus: the technical verification stage
Cyber Essentials Plus adds an independent technical audit. It checks the implementation of the controls rather than relying only on the questionnaire answers.
Plus is not a different set of five controls. It is a different level of assurance. Your preparation should connect each answer in the basic assessment to a setting, system or working practice that an assessor can verify.
Agree the audit scope with the certification body. Make sure it is consistent with the scope covered by the underlying Cyber Essentials certificate, and resolve differences before testing.
Plus provides stronger evidence of implementation, but it also requires access, coordination and technical preparation. It is not a guarantee that your business cannot suffer a security incident.
For a 2026 customer requirement, check the exact wording. A request for Cyber Essentials Plus is not satisfied by a basic certificate alone.
How do you move from no certificate to Cyber Essentials Plus?
Use one preparation programme with two assessment stages. The sequence below keeps the prerequisite visible without duplicating the work of understanding your systems.
1. Define scope
Write down what you want certified. Identify the organisation, locations, devices, networks and cloud services relevant to that scope.
Ask the certification body to resolve unclear boundaries before you submit the questionnaire. Do not assume that a certificate for one part of a business automatically covers every subsidiary, service or customer environment.
2. Check controls
Review the five technical control areas: firewalls, secure configuration, security update management, user access control and malware protection. The NCSC's Cyber Essentials requirements explain these areas.
Use the scheme requirements applicable to your assessment. For a 2026 application, confirm the relevant requirements version with the certification body rather than copying an old questionnaire or checklist.
3. Fix gaps
Turn each gap into a named action with an owner. Separate work you control from work that needs your IT provider, cloud administrator or another supplier.
Check the result after each change. Closing a task is not enough if the underlying setting still fails the requirement.
4. Pass basic
Complete and submit the Cyber Essentials questionnaire once your answers reflect the environment you intend to certify. Respond to assessor queries and achieve the basic certificate.
Record the certification date immediately. That date starts the 3-month window for completing the Plus audit.
5. Complete Plus
Coordinate technical access, the agreed audit activities and the people needed to support them. Leave room in your plan to address findings rather than assuming that the first scheduled session ends the process.
Confirm completion with the certification body. A booking confirmation, preparation report or software dashboard is not the same as a Cyber Essentials Plus certificate.
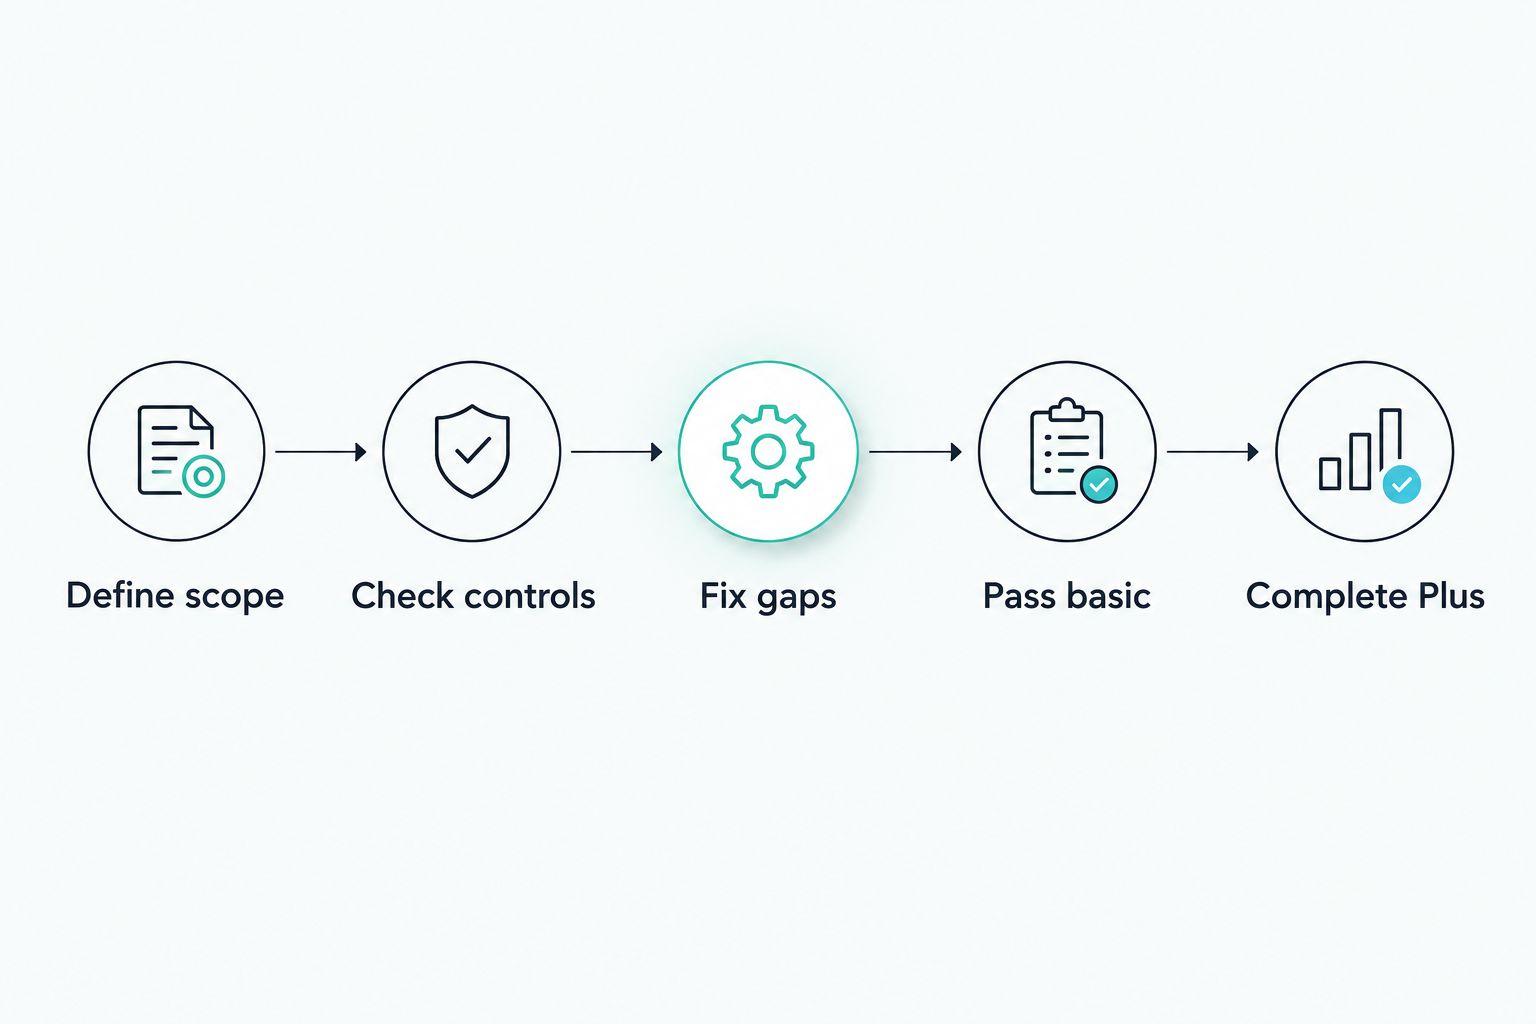
Prepare for both levels together, but pass basic Cyber Essentials before completing Plus.
The sequence stays the same whether you organise the work yourself or use outside support. A combined programme changes how you manage the work, not which certificate comes first.
Why Plus preparation still matters after passing basic
Passing the questionnaire is an important milestone. It does not remove the need to prepare for technical verification.
The difference comes from what the assessor needs to establish:
- Declared controls versus observed settings. Your answers describe implementation; the Plus audit checks it technically.
- Scope consistency. The environment presented for Plus must align with the underlying certification scope.
- Technical access. The assessor needs the agreed access and cooperation to complete the audit.
- Changes since submission. New devices, accounts or configuration changes need attention before assessment.
- Findings that need action. A technical issue needs a technical fix, not just revised wording in a policy.
Do not create a second, disconnected checklist for Plus. Keep the questionnaire, system inventory and remediation tasks tied to the same scope.
That makes it easier to explain what changed, who changed it and how you confirmed the result. It also gives your IT provider a clear list of actions instead of a general request to make the business compliant.
What should you ask before booking both assessments?
Ask how the provider will manage the dependency between the two certificates. A combined offer should make the sequence clearer, not hide it.
Use these questions before agreeing your 2026 assessment plan:
- Does the programme include both the basic assessment and the Plus audit?
- Which certification body will assess and issue each certificate?
- Is the proposed Plus scope consistent with the basic scope?
- How will you schedule Plus within the required window?
- What technical access must your team arrange?
- How will findings and any follow-up assessment be handled?
- Which tasks remain with your business or IT provider?
Separate preparation support from certification decisions. A supplier can help you organise work without being the body that decides whether you pass.
Get responsibilities in writing. Your internal owner should know who completes the questionnaire, who changes system settings and who coordinates the assessor.
Where does compliance automation fit?
OneClickComply is best suited to growing businesses that want Cyber Essentials compliance automation. The platform helps businesses achieve and maintain compliance through automated security control remediation, policy generation and risk management.
OneClickComply supports the preparation and maintenance work around Cyber Essentials. Its role is distinct from the certification body's independent assessment.
The benefit is practical: automate supported compliance tasks and manage the work required to keep controls in place. The limit is equally clear: software does not remove the basic prerequisite or replace the Plus audit.
Keep a person accountable for scope, accurate answers and assessment coordination. Automation supports that owner; it does not turn a certificate into an automatic outcome.
How long after basic Cyber Essentials can you complete Plus?
Within 3 months of achieving basic Cyber Essentials, you must complete the Plus audit. IASME's scheme guidance sets this window; do not confuse it with the certificate's annual validity period.
Confirm the underlying certification date before booking. If your certificate is outside the permitted window, ask the certification body what fresh basic assessment is required before proceeding.
Can you buy Cyber Essentials and Plus together?
Yes. You can arrange both assessments as one programme, but basic certification must still come first. A combined booking is a purchasing arrangement, not an exemption from the scheme sequence.
Ask the provider to show both milestones in the plan. Avoid treating a single order confirmation as evidence that either certification has already been achieved.
Does an existing Cyber Essentials certificate last long enough?
Cyber Essentials certificates are valid for 12 months, but the Plus prerequisite window is 3 months. A basic certificate can therefore remain valid while being too old to support a new Plus assessment under that window.
For a 2026 upgrade, check the issue date rather than relying on the expiry date. Send the certificate and scope to the certification body before agreeing the next step.
Frequently asked questions
One last thing
Check the basic certificate's issue date, not just its expiry date. The 12-month validity period and the 3-month Plus window answer different questions.
Before you book, send the certification body your certificate, scope and required completion date. Resolve eligibility first, then organise the work. Seriously Simple Cyber Compliance.